TGViewer
Channel Public Channel
Netlas.io

Netlas.io

@netlas

Explore the latest in cybersecurity with Netlas.io. Stay ahead with updates on high-profile vulnerabilities, expert tutorials, essential safety tips, and the latest Netlas developments.
Subscribers
2.33K
Photos
434
Videos
3
Links
575

Showing posts older than #335 · Back to latest

Older Posts 20 shown
Post #334 588
CVE-2024-13487: Code Injection in The CURCY WooCommerce Plugin, 7.3 rating❗️

The vulnerability allows unauthenticated users to execute arbitrary shortcodes into popular free currency exchange plugin.

Search at Netlas.io:
👉 Link: https://nt.ls/QhoHC
👉 Dork: http.body:"plugins/woo-multi-currency"

Read more: https://www.wordfence.com/threat-intel/vulnerabilities/wordpress-plugins/woo-multi-currency/curcy-multi-currency-for-woocommerce-225-unauthenticated-arbitrary-shortcode-execution-via-get-products-price-function
  • 👍 3
  • 👾 3
Post #333 499
CVE-2025-0890, -40890, -40891: Vulnerabilities in Zyxel CPE, 8.8 - 9.8 rating 🔥

The vulnerabilities include two OS Command Injections, and Improper Authentication via Telnet.

Search at Netlas.io:
👉 Link: https://nt.ls/Lxf7h
👉 Dork: telnet.banner:"Zyxel VDSL"

Vendor's advisory: https://www.zyxel.com/global/en/support/security-advisories/zyxel-security-advisory-for-command-injection-and-insecure-default-credentials-vulnerabilities-in-certain-legacy-dsl-cpe-02-04-2025
  • 🔥 4
  • 👍 3
  • 👾 2
Post #332 516
Unauthorized Data Upload in Alibaba Cloud – PoC by Chirag Artani 🔥

A new video is out on our friend’s channel, showcasing the discovery of a fresh vulnerability. The video includes an interesting query and a practical example of exploitation. Don’t miss it! 🔍

We also recommend checking out Chirag Artani’s website and Twitter for more cybersecurity insights:

👉 Website: 3rag.com
👉 Twitter: x.com/Chirag99Artani
YouTube I found 9322 Targets For Unauthorized Data Upload In Alibaba Cloud | POC Exploit Explained Live Note: do not harm any server, do not upload any malicious files like malware or anything. This is high severity bug which is leading to upload unauthorized data. I found 9321 targets which are vulnerable for this vulnerability. This is just for learning…
  • ❤ 3
  • 👾 3
Post #330 528
💯 Planned Maintenance completed 💯

Netlas is fully online again and you can get back to your projects! 👾
  • ❤ 2
  • 👾 2
  • 👍 1
  • 👎 1
Post #329 543
🚧 Planned Maintenance 🚧

We remind you that the planned work will begin in an hour, at 07:00 UTC. Our team will do our best to complete it as quickly as possible.

Please remember to save your work before this time.
  • 💊 2
  • 👨‍💻 1
Post #328 578
🚧 Planned Maintenance 🚧

We remind you, at 07:00 UTC the application will become temporarily unavailable. The work will take a couple of hours, and we will do our best to complete it as quickly as possible.

Please remember to save your work before this time.
  • ❤ 2
Post #327 892
CVE-2024-11187, -12705: Vulnerabilities in BIND DNS Software, 7.5 rating❗️

Two vulnerabilities in BIND allow DoS against DNS servers, which can be a preparatory step before the main attacks.

Search at Netlas.io:
👉 Link: https://nt.ls/bGSFv
👉 Dork: dns.banner:"BIND" OR dns_tcp.banner:"BIND"

Read more: https://kb.isc.org/docs/cve-2024-12705
  • 🔥 3
  • 👾 3
  • 👍 2
Post #326 582
🚧 Planned Maintenance 🚧
The application will be unavailable for a period of time❗️

The maintenance is scheduled to start on February 02, 2025, at 07:00 UTC ⏰. It is expected to take a couple of hours, and we will do our best to complete it as quickly as possible.

Please remember to save your work before this time.
  • 👍 2
  • 💊 2
  • 👨‍💻 1
Post #325 606
CVE-2025-22609, -22611, -22612: Multiple vulnerabilities in Coolify, 10.0 rating 🔥🔥🔥

Three vulnerabilities of highest severity in Coolify allow for RCE, privilege escalation, and authentication bypass.

Search at Netlas.io:
👉 Link: https://nt.ls/vUWWf
👉 Dork: http.favicon.hash_sha256:eaf648b6000a49599ed58bda49e576d0f981e535a8075d524a4be890edcf96d0 AND uri:*login*

Vendor's advisory: https://github.com/coollabsio/coolify/security/advisories/GHSA-3w2c-jfr2-9pg9
  • 🔥 4
  • 👾 3
  • ❤ 1
Post #324 527
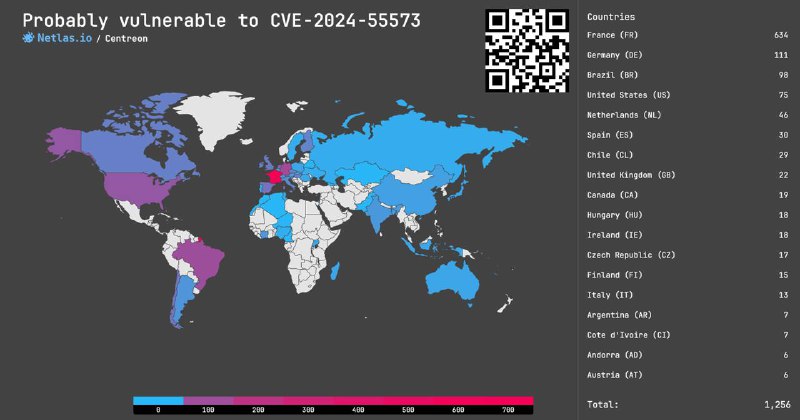
CVE-2024-55573, -53923: SQLi in Centreon, 9.1 rating 🔥

The vulnerabilities allow an attacker with high privileges to perform SQL injection into a form for uploading media.

Search at Netlas.io:
👉 Link: https://nt.ls/NETLB
👉 Dork: http.favicon.hash_sha256:795c0f8c1ff23b992d6ccb91df5e6488d4c259585da58b2e2f8eeee71147516a OR http.favicon.hash_sha256:c95e0dc8a2cc9a45d29c5381e62e48bde88f661408d4b811e72933fa7da32d4e

Vendor's advisory: https://thewatch.centreon.com/latest-security-bulletins-64/cve-2024-55573-centreon-web-critical-severity-4264
  • 🔥 3
  • 👍 2
  • 👾 2
Post #322 615
CVE-2025-0314 and other: Multiple vulnerabilities in GitLab, 4.3 - 8.7 rating❗️

In a recent advisory, GitLab writed about three vulnerabilities, including stored XSS, resource exhaustion, and protected CI/CD variables exfiltration.

Search at Netlas.io:
👉 Link: https://nt.ls/BNKS8
👉 Dork: http.favicon.hash_sha256:72a2cad5025aa931d6ea56c3201d1f18e68a8cd39788c7c80d5b2b82aa5143ef OR http.headers.set_cookie:"gitlab" OR http.headers.location:"gitlab"

Vendor's advisory: https://about.gitlab.com/releases/2025/01/22/patch-release-gitlab-17-8-1-released/
  • 👾 3
  • ❤ 1
  • 👍 1
Post #318 571
CVE-2024-12365: Missing Authorization in W3 Total Cache WordPress Plugin, 8.5 rating❗️

The vulnerability allows an authenticated attacker to access sensitive data and make unauthorized web requests to collect information from internal services.

Search at Netlas.io:
👉 Link: https://nt.ls/BpOAJ
👉 Dork: http.body:"plugins/w3-total-cache"

Read more: https://www.wordfence.com/threat-intel/vulnerabilities/wordpress-plugins/w3-total-cache/w3-total-cache-281-authenticated-subscriber-missing-authorization-to-server-side-request-forgery
  • 👾 3
  • 🔥 2
Post #316 544
CVE-2025-21598: Out-of-bounds Read in Juniper Junos OS, 8.2 rating❗️

An out-of-bouds read vulnerability in the RDP daemon, fixed last week, could potentially lead to DoS.

Search at
Netlas.io:
👉 Link: https://nt.ls/HqWq2
👉 Dork: http.title:"Juniper"

Vendor's advisory: https://supportportal.juniper.net/s/article/2025-01-Security-Bulletin-Junos-OS-and-Junos-OS-Evolved-When-BGP-traceoptions-are-configured-receipt-of-malformed-BGP-packets-causes-RPD-to-crash-CVE-2025-21598
  • 👍 2
  • 🔥 2
  • 👾 1
Older posts →
Threads Profile ViewerView any public Threads profile without an account.Open ThreadLook →Writing with AI? Make it sound human.Metric37 rewrites AI drafts so they read naturally. Free AI detector, 1,500 words free.Try Metric37 →