
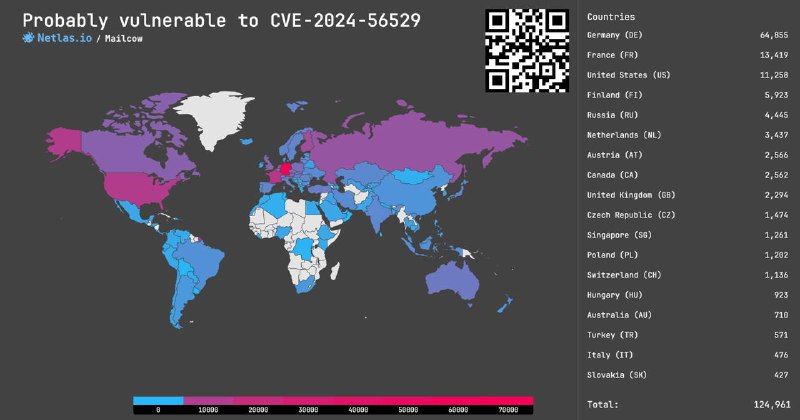
CVE-2024-56529: Session Fixation in Mailcow, 7.5 rating❗️
The application does not disable old session IDs, which allows a remote attacker to use existing IDs in the victim's browser.
Search at Netlas.io:
👉 Link: https://nt.ls/AuyJw
👉 Dork: http.title:"mailcow UI"
Vendor's advisory: https://github.com/mailcow/mailcow-dockerized/security/advisories/GHSA-23c8-4wwr-g3c6
Post #331
507
- 👍 2
- 🔥 2
- 👾 2