TGViewer
Channel Public Channel
Netlas.io

Netlas.io

@netlas

Explore the latest in cybersecurity with Netlas.io. Stay ahead with updates on high-profile vulnerabilities, expert tutorials, essential safety tips, and the latest Netlas developments.
Subscribers
2.33K
Photos
436
Videos
3
Links
577

Showing posts older than #174 · Back to latest

Older Posts 20 shown
Post #172 924
CVE-2024-3400: command injection in Palo Alto Networks PAN-OS, 10.0 rating 🔥🔥🔥

A 0-day vulnerability in PAN-OS that allows an unauthenticated attacker to execute arbitrary code on the firewall with root rights. According to Palo Alto Networks, attacks have already been carried out that exploit this vulnerability!

Search at Netlas.io:
👉 Link: https://nt.ls/eprag
👉 Dork: tag.name:"palo_alto"

Vendor's advisory: https://security.paloaltonetworks.com/CVE-2024-3400
  • 🔥 5
  • 👾 2
Post #170 811
❗️Cookie consent update❗️

To improve usability and functionality of the site, as well as in connection with new requirements from Google, we are changing the mechanism for obtaining cookie consent.

After the update, consent will be consistent across all of our resources, including the website, app, and help portal.

We would be grateful if you check the box again ✅
  • 👾 5
  • 🤝 1
Post #169 1.08K
CVE-2024-3273: RCE in D-Link NAS, 7.3 rating 🔥

The vulnerability can be exploited due to a combination of two weaknesses: a hardcoded account and the ability to inject commands through the “system” parameter. There are many devices affected that have reached the end of their lifespan.

According to GreyNoise, hackers are already carrying out attacks! 😨

Search at Netlas.io:
👉 Link: https://nt.ls/TyD6H
👉 Dork: http.body:"Text:In order to access the ShareCenter"

Read more: https://www.bleepingcomputer.com/news/security/critical-rce-bug-in-92-000-d-link-nas-devices-now-exploited-in-attacks/
  • 🔥 4
  • 👾 3
  • 👍 2
Post #168 702
👾 Netlas 0.23.1 update 👾

👉 Two API endpoints added, one depricated
👉 API schema documentation updated
🐞 Super annoying autocomplete bug fixed!

❗ We also noticed that Netlas is often used through a proxy without registration. To reduce the load on the servers, the number of requests available to unregistered users has been reduced to 10 ❗


Changelog: https://nt.ls/changelog


📖 Netlas Docs update 📖

👉 To learn more about the features of Netlas Search tools, read the recently published help topic: https://nt.ls/pPte1
👉 Details and examples of usage Netlas IP/Domain tool: https://nt.ls/wDuYN
  • 👍 4
  • 👾 3
Post #167 1.08K
CVE-2024-2879: SQL injection in LayerSlider plugin for WordPress, 9.8 rating 🔥

Plugin used on millions of websites had a feature that was vulnerable to blind SQL injection. If the vulnerability was successfully exploited, the attacker could gain access to any confidential information.

Search at Netlas.io:
👉 Link: https://nt.ls/8CmgD
👉 Dork: http.body:"plugins/layerslider"

Read more: https://www.wordfence.com/blog/2024/04/5500-bounty-awarded-for-unauthenticated-sql-injection-vulnerability-patched-in-layerslider-wordpress-plugin/
  • 🔥 6
  • 👾 2
Post #164 1.63K
CVE-2024-21677: Path Traversal in Atlassian Confluence, 8.3 rating❗

The vulnerability discovered during the Bug Bounty program allows an unauthenticated attacker to carry out actions that threaten the confidentiality and availability of the system. The patch has already been released.

Search at Netlas.io:
👉 Link: https://nt.ls/mghaY
👉 Dork: http.meta:"confluence-base-url"

Vendor's bulletin: https://confluence.atlassian.com/security/security-bulletin-march-19-2024-1369444862.html
  • 👾 5
  • ❤ 3
  • 🔥 3
  • 👍 1
  • 💋 1
Post #161 730
🚧Planned update 🚧

The update will last 21.03.2024 from ~08:00 - 09:00 UTC ⏰, during which time the application will be unavailable.

Don't forget to save the results of your work before this.
  • 👾 3
  • 🙏 2
  • 👍 1
  • 🔥 1
Post #160 1.27K
CVE-2024-23334: Path Traversal in aiohttp Python lib, 7.5 rating❗

An old vulnerability that has started to gain attention again recently. According to Cyble research, attackers have been scanning nodes with a vulnerable version of the library since the end of February. We recommend that everyone who uses it update immediately!

Search at Netlas.io:
👉 Link: https://nt.ls/lrzzv
👉 Dork: http.headers.server:"aiohttp"

Read more: https://www.bleepingcomputer.com/news/security/hackers-exploit-aiohttp-bug-to-find-vulnerable-networks/
  • 👾 5
  • 🔥 3
  • ❤ 2
  • 👍 2
Post #159 798
APSB24-05, APSB24-14: Multiple vulns in Adobe products, critical rating 🔥

Two vulnerabilities from the new Adobe security bulletin, the exploitation of which will allow an attacker to achieve arbitrary file system read, code execution, and security feature bypass.

Search at Netlas.io:
👉🏻 Link: https://nt.ls/EEZn7
👉🏻 Dork: tag.name:"adobe_experience_manager" OR tag.name:"adobe_coldfusion"

Vendor's advisory: https://helpx.adobe.com/security/security-bulletin.html
  • 👾 4
  • 🔥 3
  • ❤ 2
Post #158 825
CVE-2024-21899, -21900, -21901: Improper Authentication and other in QNAP NAS, 4.3 - 9.8 rating 🔥

Code injection, execution of arbitrary commands and, most interestingly, a vulnerability in the authentication that allows an attacker to compromise the entire system via network.

Search at Netlas.io:
👉🏻 Link: https://nt.ls/Wnycw
👉🏻 Dork: http.body_sha256:4a1815f3e87d6d623c22921d9c39b2de614351d71831976bbc807f571953ff21

Vendor's advisory: https://www.qnap.com/en/security-advisory/qsa-24-09
  • 🔥 7
  • 👾 2
  • ❤ 1
  • 🙏 1
Post #156 782
CVE-2024-27198, -27199: Auth Bypass in JetBrains TeamCity, 9.8 rating 🔥

The vulnerabilities may enable an attacker to bypass authentication checks and gain administrative permissions on the TeamCity server. Affected all versions through 2023.11.3!

Search at Netlas.io:
👉 Link: https://nt.ls/7DYva
👉 Dork: http.headers.set_cookie:TCSESSIONID NOT http.body:"2023.11.3" NOT http.body:"2023.11.4"

Vendor's advisory: https://blog.jetbrains.com/teamcity/2024/03/additional-critical-security-issues-affecting-teamcity-on-premises-cve-2024-27198-and-cve-2024-27199-update-to-2023-11-4-now/
  • 👾 5
  • 🔥 3
  • 👍 2
Post #155 758
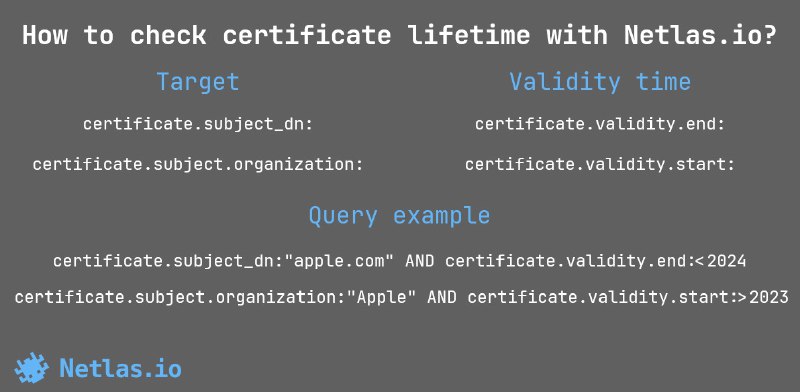
Fact: old SSL/TLS certificate threatens both the reputation of the website and the security of the data the user is working with❗

How to check the certificate for yourself or a contractor?

👉 Just use Netlas: https://app.netlas.io/certs/
  • 👾 3
  • ❤ 1
  • 👍 1
Older posts →
Threads Profile ViewerView any public Threads profile without an account.Open ThreadLook →Writing with AI? Make it sound human.Metric37 rewrites AI drafts so they read naturally. Free AI detector, 1,500 words free.Try Metric37 →