
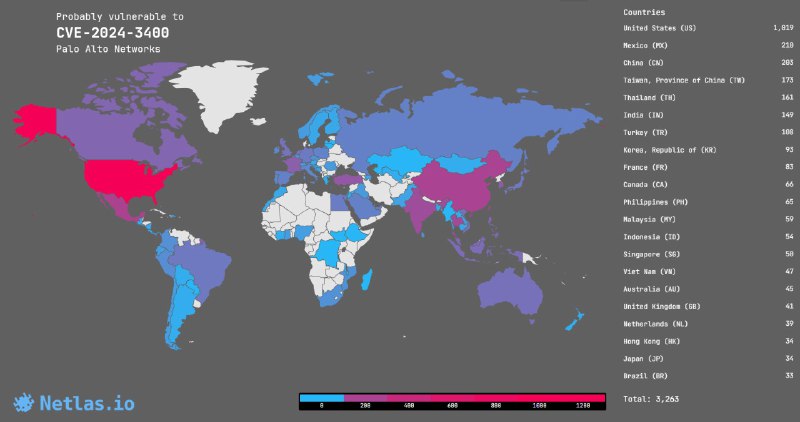
CVE-2024-3400: command injection in Palo Alto Networks PAN-OS, 10.0 rating 🔥🔥🔥
A 0-day vulnerability in PAN-OS that allows an unauthenticated attacker to execute arbitrary code on the firewall with root rights. According to Palo Alto Networks, attacks have already been carried out that exploit this vulnerability!
Search at Netlas.io:
👉 Link: https://nt.ls/eprag
👉 Dork: tag.name:"palo_alto"
Vendor's advisory: https://security.paloaltonetworks.com/CVE-2024-3400
Post #172
924
- 🔥 5
- 👾 2