Post #337
3.06K
Channel Public Channel
 LI
Linux Kernel Security
@linkersec
Links related to Linux kernel security and exploitation | Chat @linkersec_chat | @xairy @a13xp0p0v | Mirrors on https://xairy.io/linkersec
- Subscribers
- 4.72K
- Photos
- 122
- Videos
- 0
- Links
- 355
Showing posts older than #338 · Back to latest
Older Posts 18 shown

Post #335
6.41K


USB HID info-leak exploit for CVE-2025-38494/CVE-2025-38495
Exploit by Andrey Konovalov for an integer underflow bug in the HID subsystem that allows leaking up to 64 KB of kernel memory over USB.
The bug is still not fixed in the Pixel and Ubuntu kernels.
Exploit by Andrey Konovalov for an integer underflow bug in the HID subsystem that allows leaking up to 64 KB of kernel memory over USB.
The bug is still not fixed in the Pixel and Ubuntu kernels.
- 🔥 22
- 😱 7
- 👍 1
Post #334
8.76K

ksmbd - Fuzzing Improvements and Vulnerability Discovery
Another article by Norbert Szetei about fuzzing the ksmbd module with syzkaller.
Covers the improvements made to the fuzzer since the previous article. These improvements allowed finding an impressive amount of 23 bugs in ksmbd.
Another article by Norbert Szetei about fuzzing the ksmbd module with syzkaller.
Covers the improvements made to the fuzzer since the previous article. These improvements allowed finding an impressive amount of 23 bugs in ksmbd.
- 🔥 5
- 🎉 1
Post #333
3.13K

arm64: Linear mapping is mapped at the same static virtual address
Bug report by Seth Jenkins and Jann Horn showing that the physmap region is mapped at a fixed virtual address on Android despite KASLR.
Bug report by Seth Jenkins and Jann Horn showing that the physmap region is mapped at a fixed virtual address on Android despite KASLR.
- 🤯 12
- 👍 2
- 🔥 2
Post #331
3.91K


Kernel-hack-drill and a new approach to exploiting CVE-2024-50264 in the Linux kernel
Alexander Popov (me) published an article about exploiting a race condition in AF_VSOCK subsystem, the bug that received a Pwnie Award 2025.
Despite the bug collision with other researchers, Alexander found a new exploitation method for this bug by relying on his pet project kernel-hack-drill.
Alexander Popov (me) published an article about exploiting a race condition in AF_VSOCK subsystem, the bug that received a Pwnie Award 2025.
Despite the bug collision with other researchers, Alexander found a new exploitation method for this bug by relying on his pet project kernel-hack-drill.
- 🔥 19
- 👍 3
- 👏 3
Post #329
4.21K
From Chrome renderer code exec to kernel with MSG_OOB
Jann Horn posted an article about exploiting CVE-2025-38236, a UAF in the UNIX domain sockets. The article contains many interesting notes and takeaways on writing kernel exploits that work from within the Chrome renderer sandbox.
Jann Horn posted an article about exploiting CVE-2025-38236, a UAF in the UNIX domain sockets. The article contains many interesting notes and takeaways on writing kernel exploits that work from within the Chrome renderer sandbox.

- 🔥 14
- 👍 2
- 👏 2
Post #328
4.68K
Exploiting All Google kernelCTF Instances And Debian 12 With A 0-Day For $82k: A RBTree Family Drama
Crusaders of Rust posted an article about exploiting a UAF in the network packet scheduler. The researchers manipulated red-black trees in the kernel to achieve a page-level UAF, which they used to escalate privileges.
Crusaders of Rust posted an article about exploiting a UAF in the network packet scheduler. The researchers manipulated red-black trees in the kernel to achieve a page-level UAF, which they used to escalate privileges.

- 🔥 13
- 😱 2
Post #327
3.47K
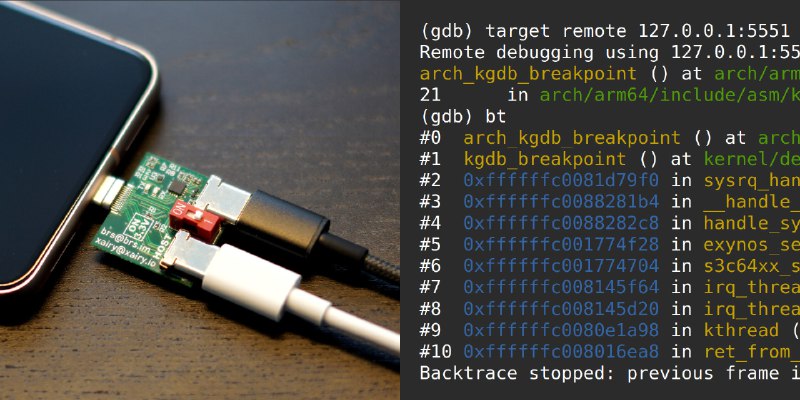
Debugging the Pixel 8 kernel via KGDB
Article by Andrey Konovalov about setting up KGDB on Pixel 8 for debugging its kernel.
Provides instructions for getting the kernel log over UART via USB-Cereal, building and flashing a kernel with KGDB, breaking into KGDB via /proc/sysrq-trigger or by sending SysRq-G over a serial connection, dealing with watchdogs, etc.
Article by Andrey Konovalov about setting up KGDB on Pixel 8 for debugging its kernel.
Provides instructions for getting the kernel log over UART via USB-Cereal, building and flashing a kernel with KGDB, breaking into KGDB via /proc/sysrq-trigger or by sending SysRq-G over a serial connection, dealing with watchdogs, etc.
- 🔥 21
- 👍 6
Post #326
4.52K

CVE-2023-52927 - Turning a Forgotten Syzkaller Report into kCTF Exploit
Article by Hoàng Hải Long about finding an unfixed netfilter use-after-free bug reported by syzbot. The researcher exploited it to pwn the kernelCTF COS instance.
Article by Hoàng Hải Long about finding an unfixed netfilter use-after-free bug reported by syzbot. The researcher exploited it to pwn the kernelCTF COS instance.
- 🔥 21
Post #325
3.74K
Fuzzing Linux Kernel Modules, with Slava Moskvin
Stream by Slava Moskvin hosted by Stephen Sims about building a custom fuzzer to rediscover CVE-2025-0927 in the HFS+ filesystem implementation.
Slava started with a simple fuzzer implementation and then improved it step-by-step by adding coverage collection, proper seed generation, mutations, etc.
The source code of the fuzzer is public.
YouTube Fuzzing Linux Kernel Modules, with Slava Moskvin In this video/stream, we’ll walk through the process of fuzzing Linux kernel modules from scratch: picking a subsystem, analyzing its attack surface, compiling a custom kernel, writing a simple fuzzer, and progressively making it smarter—eventually turning… Stream by Slava Moskvin hosted by Stephen Sims about building a custom fuzzer to rediscover CVE-2025-0927 in the HFS+ filesystem implementation.
Slava started with a simple fuzzer implementation and then improved it step-by-step by adding coverage collection, proper seed generation, mutations, etc.
The source code of the fuzzer is public.
- 🔥 19
Post #324
3.17K

Post #323
4.33K

Bypass Kernel Barriers: Fuzzing Linux Kernel in Userspace With LKL
Xuan Xing & Eugene Rodionov gave a talk (slides) about fuzzing the Linux kernel interfaces fully in user space using LKL (Linux Kernel Library).
Xuan Xing & Eugene Rodionov gave a talk (slides) about fuzzing the Linux kernel interfaces fully in user space using LKL (Linux Kernel Library).
- 🔥 16
- 🤔 4
- 👍 3
Post #322
3.46K

Post #321
4.32K

Exploiting the CVE-2025-21756 1-day vulnerability
Hyunwoo Kim and Wongi Lee posted a kernelCTF report about exploiting a UAF in the vsock subsystem of the Linux kernel.
The researchers leaked the kernel base address using the EntryBleed side-channel attack and then turned the UAF on the vsock_sock structure into a RIP control primitive to execute a ROP-chain.
Hyunwoo Kim and Wongi Lee posted a kernelCTF report about exploiting a UAF in the vsock subsystem of the Linux kernel.
The researchers leaked the kernel base address using the EntryBleed side-channel attack and then turned the UAF on the vsock_sock structure into a RIP control primitive to execute a ROP-chain.
- 👍 16
- 🔥 5
Post #320
3.52K

Solo: A Pixel 6 Pro Story (When one bug is all you need)
Awesome article by Lin Ze Wei about adapting the Pixel 7/8 exploit for a bug in the Mali GPU driver to Pixel 6 Pro.
Awesome article by Lin Ze Wei about adapting the Pixel 7/8 exploit for a bug in the Mali GPU driver to Pixel 6 Pro.
- 🔥 11
- 👍 2
Post #319
4.31K

Bypassing MTE with CVE-2025-0072
Article by Man Yue Mo about exploiting a page use-after-free vulnerability in the ARM's Mali GPU driver in the code that manages userspace-mapped pages.
Author published an exploit for this bug that disable SELinux and gains root privileges on Pixel 8 running from the untrusted_app context. The exploit is not affected by MTE.
Article by Man Yue Mo about exploiting a page use-after-free vulnerability in the ARM's Mali GPU driver in the code that manages userspace-mapped pages.
Author published an exploit for this bug that disable SELinux and gains root privileges on Pixel 8 running from the untrusted_app context. The exploit is not affected by MTE.
- 👍 13
- 🔥 5
Post #318
3.77K

How I used o3 to find CVE-2025-37899, a remote zeroday vulnerability in the Linux kernel's SMB implementation
Article by Sean Heelan about rediscovering a bug in the ksmbd module via the OpenAI's o3 model and then finding a 0-day vulnerability as well.
The researcher had to rerun the prompt multiple times before getting a true-positive result. The o3 model managed to find the 0-day vulnerability in only ~1 out of 50 runs.
Article by Sean Heelan about rediscovering a bug in the ksmbd module via the OpenAI's o3 model and then finding a 0-day vulnerability as well.
The researcher had to rerun the prompt multiple times before getting a true-positive result. The o3 model managed to find the 0-day vulnerability in only ~1 out of 50 runs.
- 👍 19
- 🔥 1
Post #317
3.45K
Android In-The-Wild: Unexpectedly Excavating a Kernel Exploit
Talk by Seth Jenkins about analyzing the traces of an In-The-Wild exploit that targeted the Qualcomm adsprpc driver.
Based on a previously published article.
Talk by Seth Jenkins about analyzing the traces of an In-The-Wild exploit that targeted the Qualcomm adsprpc driver.
Based on a previously published article.
- 👍 7