TGViewer
Linux Kernel Security Linux Kernel Security @linkersec · 4.72K subscribers
Post #314 5.85K
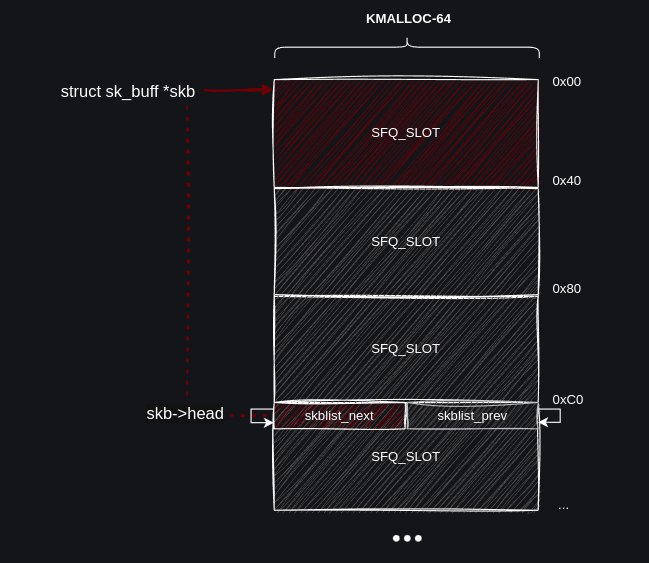
[CVE-2025-37752] Two Bytes Of Madness: Pwning The Linux Kernel With A 0x0000 Written 262636 Bytes Out-Of-Bounds

Great article by D3vil about exploiting a type confusion in the network scheduler subsystem and pwning all kernelCTF instances.

Author exploited a severely-limited OOB side-effect of the bug to corrupt pipe_inode_info->tmp_page and gain a page UAF read/write primitive. Researcher then swapped the private_data and f_cred fields of a signalfd file structure and overwrote the credentials via signalfd_ctx.
  • 🔥 17
  • 👏 3
More from @linkersec
  1. Sep 21, 2026CROSS-X: Generalized and Stable Cross-Cache Attack on the Linux Kernel Paper by Dong-ok Ki…
  2. Sep 16, 2026Testing race conditions with memory access tracing and stack-based delay injection Article…
  3. Sep 8, 2026SCTPhantom: An 18-Year-Old SCTP ASCONF Transport Use-After-Free Article about exploiting C…
  4. Aug 14, 2026Gone in 60 Frames – USB Video Exploitation Article (and slides) by Alex Plaskett and Rober…
  5. Aug 11, 2026IonStack part III: Rooting Android 17 with GhostLock Article about adapting the exploit of…
  6. Jul 23, 2026I handed the epoll UAF to an agent Article by Guy Beck about using Claude for porting an e…
Threads Profile ViewerView any public Threads profile without an account.Open ThreadLook →Writing with AI? Make it sound human.Metric37 rewrites AI drafts so they read naturally. Free AI detector, 1,500 words free.Try Metric37 →