TGViewer
Linux Kernel Security Linux Kernel Security @linkersec · 4.72K subscribers
Post #160 2.75K
How The Tables Have Turned: An analysis of two new Linux vulnerabilities in nf_tables

A detailed article by David Bouman about exploiting an integer-overflow leading to a limited stack-out-of-bounds read/write in the nf_tables module.

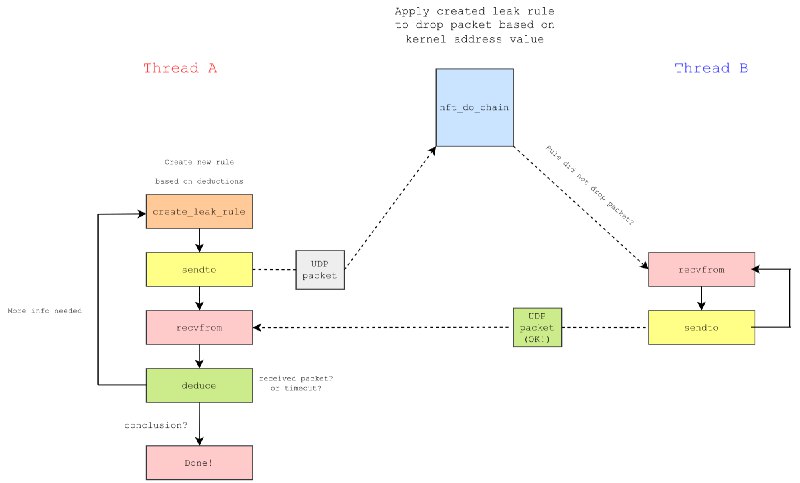
The exploit constructs a filter whose logic depends on the value of a kernel address that happens to be on the stack. This way, it leaks the KASLR offset by observing the side-effects.

The exploit then builds a ROP chain that leaves the softirq context where the bug is triggered, switches to the root network namespace, and gains root privileges.
David's Blog How The Tables Have Turned: An analysis of two new Linux vulnerabilities in nf_tables Analysis and exploitation of Linux kernel vulnerabilities CVE-2022-1015 and CVE-2022-1016. I talk about how I found these vulnerabilities, explain the internals of nf_tables and come up with an local privilege escalation exploitation strategy.
  • 🔥 5
  • 👍 1
More from @linkersec
  1. Sep 28, 2026PageJack in Action: CVE-2022-0995 exploit Article by Jean Vincent describing how a relativ…
  2. Sep 21, 2026CROSS-X: Generalized and Stable Cross-Cache Attack on the Linux Kernel Paper by Dong-ok Ki…
  3. Sep 16, 2026Testing race conditions with memory access tracing and stack-based delay injection Article…
  4. Sep 8, 2026SCTPhantom: An 18-Year-Old SCTP ASCONF Transport Use-After-Free Article about exploiting C…
  5. Aug 14, 2026Gone in 60 Frames – USB Video Exploitation Article (and slides) by Alex Plaskett and Rober…
  6. Aug 11, 2026IonStack part III: Rooting Android 17 with GhostLock Article about adapting the exploit of…
Threads Profile ViewerView any public Threads profile without an account.Open ThreadLook →Writing with AI? Make it sound human.Metric37 rewrites AI drafts so they read naturally. Free AI detector, 1,500 words free.Try Metric37 →