TGViewer
Channel Public Channel
Kubesploit

Kubesploit

@kubesploit

News and links on Kubernetes security curated by the @Learnk8s team
Website: https://kubesploit.io/
Subscribers
2.13K
Photos
955
Videos
206
Links
1.9K

Showing posts older than #1688 · Back to latest

Older Posts 20 shown
Post #1687 1.04K
This article shows how to use tofu-controller to manage Terraform resources with GitOps for external systems like Grafana dashboards and HashiCorp Vault policies with continuous reconciliation and automatic drift detection.

More: https://ku.bz/B3y_Zflr7
Post #1686 266

Forwarded from KubeFM

Fernando from SadServers on how he cut his Kubernetes bill from $1,000/month on GKE to $30/month on Hetzner with Edka — a 500% cost reduction for the same capacity.

You will learn:

- Why Kubernetes hasn't delivered on its original promise of cost savings through bin packing — and what it actually provides instead
- A real cost comparison: $1,000/month on GKE vs. $30/month on Hetzner with Edka for the same nominal capacity
- What you need to bring with you (observability, logging, dashboards) when leaving a fully managed cloud provider

Watch (or listen to) it here: https://ku.bz/6nSDbz9m4

🌟 This episode is brought to you by LearnKube — get started on your Kubernetes journey through comprehensive online, in-person or remote training https://learnkube.com/training

With @Birthmarkb
Post #1685 665
Linnix is an eBPF + PSI-powered Kubernetes observability agent written in Rust that identifies which pod is actually stalling your services, not just consuming CPU.

More: https://ku.bz/x-VQLHwSW
Post #1684 375

Forwarded from KubeFM

Zero trust in Kubernetes works best as a layered model, not a single toggle.

Abhishek Rao breaks down a phased approach: start with micro-segmentation, add identity with mTLS, and enforce cluster-level ingress and egress controls. This creates security boundaries teams can reason about and maintain.

Strong security comes from structure, not one-off rules.


Watch the full interview: https://ku.bz/_q9XBgY2c

This interview is a reaction to John Howard's episode https://ku.bz/sk-ZF1PG9
Post #1683 411
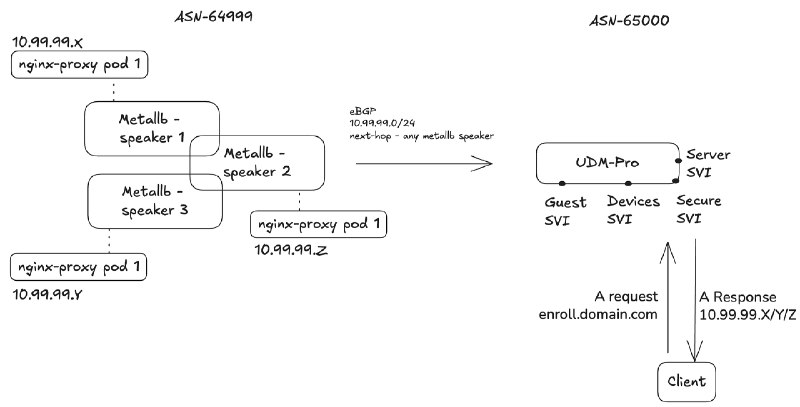
This article solves automated certificate distribution for EAP-TLS WiFi authentication using nginx-proxy on Kubernetes with step-ca, avoiding traditional MDM by hosting mobileconfig files at an HTTPS endpoint with mTLS authentication.

More: https://ku.bz/spclMhjDz
Post #1682 453

Forwarded from KubeFM

Spectro Cloud just announced Hadron Linux — a brand new Linux distribution engineered from scratch by the Kairos team.

Ettore Di Giacinto explains: Hadron is purpose-built as a minimal, immutable base layer for edge infrastructure. Unlike retrofitted general-purpose distributions, it is specifically designed to eliminate common friction points when deploying Kubernetes at scale.

The goal: a Linux foundation that treats edge as a first-class target, not an afterthought.


Watch the announcement: https://ku.bz/wMhKpZ5bQ

Read the announcement: https://ku.bz/_9RmXnjDJ
Post #1681 750
cek is a command-line tool for exploring OCI container image filesystems, reading file contents, and inspecting layer mechanics without running containers by connecting to container daemons or pulling from registries.

More: https://ku.bz/VWLLdYCbb
Post #1680 353

Forwarded from KubeFM

Nicholaos Mouzourakis, Staff Product Security Engineer at Gusto, breaks down the common deployment patterns for Open Policy Agent (OPA) in Kubernetes environments. He explains the tradeoffs between individual pods, auto-scaling groups, daemon sets, sidecars, and WASM modules.

He outlines critical considerations for selecting the right deployment option:

- Latency requirements
- Bandwidth constraints
- Development overhead
- Feature compatibility (noting WASM modules lack full standard library support)
- Cloud costs and policy size implications

He notes that co-located pods typically achieve a few milliseconds of latency, and suggests WASM modules for those requiring even better performance.

Watch the full episode: https://kube.fmhttps://ku.bz/S-2vQ_j-4
Post #1679 347

Forwarded from Kube Careers

This week's 6 best Kubernetes vacancies that focus on security are:

DevSecOps Engineer with Anthropic
💰 $40.5M to $48.5M a year
🏠 From the office in San Francisco, CA, USA
→ https://ku.bz/wrrnmcjDQ

DevSecOps Engineer with Tailscale
💰 $15.96M to $19.97M a year
🌎 Fully remote
→ https://ku.bz/J9Cs7QBBp

DevSecOps Engineer with Accenture Federal Services
💰 $11.49M to $15.13M a year
👨‍💻 Remote from
→ https://ku.bz/bsl59cPMh

DevSecOps Engineer with OpenAI
💰 $364.5K to $490K a year
👨‍💻 Remote from the United States of America
→ https://ku.bz/NXd17JHfV

DevSecOps Engineer with Faire
💰 $268K to $368.5K a year
🏠 From the office in San Francisco, CA, USA
→ https://ku.bz/Lt703grhh

👉 Browse 2459 jobs on Kube Careers https://kube.careers
Post #1678 354
This article demonstrates how to exploit Kubernetes PKI and kubelet credentials after gaining node access to escalate from pod compromise to full cluster control.

More: https://ku.bz/NxVxjKtt0
Post #1677 294

Forwarded from Kube Builders

pwru is an eBPF-based tool for tracing network packets in the Linux kernel with advanced filtering capabilities.

It allows fine-grained introspection of kernel state to facilitate debugging network connectivity issues.

More: https://ku.bz/Q3X1ngZGC
Post #1676 266

Forwarded from LearnKube news

This week on Learn Kubernetes Weekly 173:

🔥 Kubernetes Egress Control with Squid Proxy
💪 How We Turned a Forced OS Migration into a 30% Infrastructure Reduction
⚡ Auto-scaling and Load-based Scaling in Kubernetes
🎯 Smart Scheduler: Intelligent Pod Placement for Kubernetes Cost Optimization
🤖 Using Claude Code to Pilot Kubernetes on Autodock

Read it now: https://kube.today/issues/173

⭐️ This newsletter is brought to you by Hadron, the new lightweight secure Linux OS from the Kairos team https://ku.bz/mMZytrj-z
Post #1675 319
Chainloop is an evidence store and policy engine for Software Supply Chain attestations, SBOMs, VEX, SARIF, and QA reports, with contract-based workflows, Rego policy evaluation, and third-party integrations such as Dependency-Track and Guac.

More: https://ku.bz/_wQslV4bc
Post #1674 246

Forwarded from KubeFM

Karpenter can rotate your nodes for three reasons: they're underutilized, they're empty, or the AMI has drifted from what you specified.

You can set a disruption budget for each reason to control how many nodes rotate at once. But here's the catch: if you only set budgets for two reasons and skip the third, Karpenter doesn't disable it. It silently applies a default 10% budget to any reason you didn't mention.

Adhi Sutandi's team found this the hard way — drift events fired during maintenance windows they thought were locked down. The fix? Set a single budget of one node with no reason qualifier, so it applies to everything.


New episode out now: https://ku.bz/XyVfsSQPr
Post #1673 282
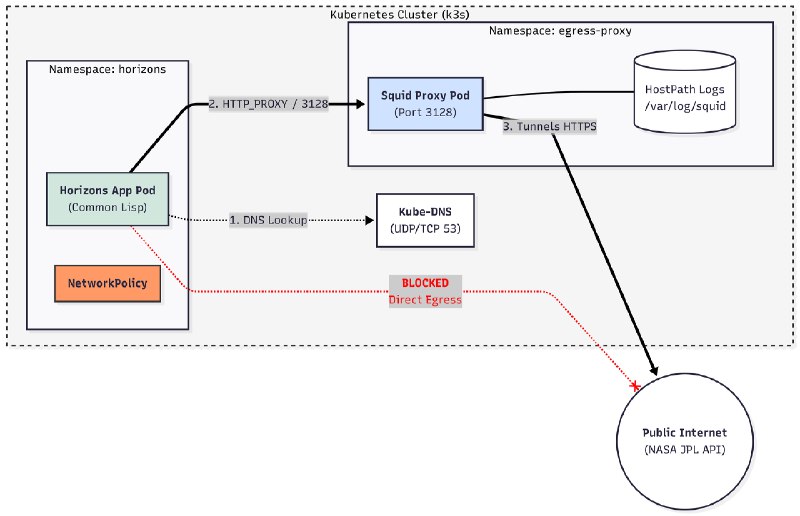
This tutorial teaches how to implement Kubernetes egress control using Squid proxy and NetworkPolicy for visibility and enforcement of outbound traffic without service mesh complexity.

More: https://ku.bz/XyLs9nnzh
Post #1672 299

Forwarded from KubeFM

"The supply chain has become the sharp end of the wedge."

Andrew Martin traces the evolution of software supply chain attacks from boot sector viruses to modern npm-borne worms. His team signs everything, generates SBOMs, and verifies Cosign artifacts at admission time into Kubernetes clusters.

The prediction for 2026: continuous validation of supply chain security metadata at runtime will become a staple in Kubernetes security tooling this year.


Watch the full interview: https://ku.bz/wyMlWGTqf
Post #1671 193

Forwarded from LearnKube news

📕 We published a book on optimising and right-sizing GPUs in Kubernetes.

Most GPU clusters show 100% allocation and single-digit actual usage.

The book helps you:

- Tell whether your GPUs are actually computing or just allocated
- Pick the right metrics instead of trusting nvidia-smi
- Choose between time-slicing, MIG, and dedicated GPUs based on real data
- Stop GPU waste from cascading into CPU and memory waste

Download it for free here: ku.bz/KL4jRvsL4

This book was made possible by Kubex.
Post #1670 298
cert-manager-webhook-pdns is a PowerDNS webhook for cert-manager that enables automated Let's Encrypt certificate issuance using DNS-01 challenges by integrating with PowerDNS API for DNS record management.

More: https://ku.bz/x3vxd7ZpJ
Post #1669 258

Forwarded from KubeFM

"I don't want to see AI agents autonomously control clusters right now."

Nick Eberts draws a clear line: AI assistants are valuable for read-only troubleshooting — giving hints, explaining what's wrong. But making changes? That should go through pull requests and human review, especially in a GitOps workflow. He also flags an emerging challenge: securing agent-to-agent communication between MCP servers and clients, and extending Istio authorization policies into the agent layer.

The takeaway: AI should assist, not act — until the guardrails catch up.


Watch the full interview: https://ku.bz/G1QSYQTn2

This interview is a reaction to Mai Nishitani's episode https://ku.bz/3hWvQjXxp
Post #1668 290

Forwarded from KubeFM

Shyam Jeedigunta, Principal Engineer at Amazon Web Services (AWS), explains the security challenges and solutions for onboarding Kubernetes nodes from different infrastructure providers.

He discusses how to handle identity management, certificate issuance, and trust establishment when nodes come from edge locations, on-premises infrastructure, or other cloud providers rather than the same infrastructure as the control plane.

Watch the full interview: https://ku.bz/m89tLbgcq
Older posts →
Threads Profile ViewerView any public Threads profile without an account.Open ThreadLook →Writing with AI? Make it sound human.Metric37 rewrites AI drafts so they read naturally. Free AI detector, 1,500 words free.Try Metric37 →