TGViewer
Channel Public Channel
Kubesploit

Kubesploit

@kubesploit

News and links on Kubernetes security curated by the @Learnk8s team
Website: https://kubesploit.io/
Subscribers
2.13K
Photos
961
Videos
208
Links
1.9K

Showing posts older than #1367 · Back to latest

Older Posts 20 shown
Post #1366 2.26K
This article shows how to use Kyverno policies and Helm to rewrite container image registry URLs at admission for all pod container types.

This image mutation enables namespace-controlled migration to new registries without editing every manifest.

More: https://ku.bz/Hn4LDyShr
Post #1365 608
Gatekeeper is a Kubernetes admission controller that enforces policies defined with Open Policy Agent (OPA).

It uses CRDs like ConstraintTemplate and Constraint to validate and mutate resources, supporting audit and external data integration.

More: https://ku.bz/J_2l-lqQZ
Post #1364 507

Forwarded from KubeFM

Harsha Koushik, a Security Researcher and Technical Product Manager at Palo Alto Networks, emphasizes that fewer binaries and libraries result in fewer vulnerabilities.

He points out that even newer libraries add functionality but also introduce additional vulnerabilities.

This highlights the importance of minimizing unnecessary components to enhance security, as simply removing a shell does not guarantee safety.

Watch the full episode: https://ku.bz/n_sJ04xMY
Post #1363 2.01K
flux2-multi-tenancy provides GitOps templates and Kyverno policies to automate tenant onboarding.

It provisions namespaces, RBAC, and policy controls in Kubernetes using pull requests, enabling secure multi-tenant cluster management from Git.

More: https://ku.bz/_X6s8kP28
Post #1362 380

Forwarded from Kube Architect

By leveraging Kyverno, Kueue, and Argo CD, IBM Research transformed chaotic GPU resource sharing into a policy-driven, fair computing environment—solving GPU hogging, scheduling conflicts, and administrative overhead in research computing.

More: https://ku.bz/XhPWZypGS
Post #1361 367

Forwarded from LearnKube news

This week on Learn Kubernetes Weekly 131:

♻️ Synchronizing Database schema updates between projects and environments
🛡️ Building Resilient Applications on Kubernetes
🤺 Amazon EKS Auto Mode vs Azure AKS Automatic: Which is the Better Managed Kubernetes Solution?
🤔 A CNI 'chicken-and-egg' dilemma: How does Calico assign IPs to itself?
🤏 API Streaming in Kubernetes: Memory-Efficient List Responses

Read it now: https://learnk8s.io/issues/131

⭐️ This newsletter is sponsored by RunWhen — build AI Engineering Assistants with thousands of tools for your infrastructure, platform services, logs, metrics and more https://ku.bz/FxmM9QtQ4
Post #1360 2.04K
kubectl-validate is a SIG-CLI subproject to support the local validation of resources for native Kubernetes types and CRDs.

More: https://ku.bz/Mc8q9qGCz
Post #1359 505
The article analyzes attacker entry points to control plane, including API server exposure, etcd compromise, misconfigured authentication, and insecure kubeconfigs.

It explains exploitation steps, providing technical mitigation for each vector.

More: https://ku.bz/x-vZVkmkd
Post #1358 582
This article details how Distroless images reduce attack surface by removing shells and package managers.

It compares image sizes, shows how to build with multistage Dockerfiles, and validates security via Grype—finding 53 vs 107 CVEs in slim images.

More: https://ku.bz/Njn7BN6S-
Post #1357 564
This article demonstrates how to extend Kubernetes RBAC using Aggregate ClusterRoles.

Learn how to combine multiple roles for dynamic access control, simplify permission management, and apply changes declaratively with best practices.

More: https://ku.bz/2YT-Hy9vX
Post #1356 566
Vals is a Helm-compatible tool that injects secrets and config values from backends like Vault, AWS SSM, GCP Secrets Manager, and Kubernetes.

It resolves ref+ URIs in YAML, supporting helmfile, direnv, and kubectl workflows.

More: https://ku.bz/ZrrpTvVCl
Post #1355 430

Forwarded from LearnKube news

This week on Learn Kubernetes Weekly 130:

🚀 L4-L7 Performance: Comparing LoxiLB, MetalLB, NGINX, and HAProxy
🧹 The Karpenter effect: redefining our Kubernetes operations
💿 Replacing StatefulSets with a custom operator in our Postgres cloud platform
🔒 Kubernetes Authentication: comparing solutions
9️⃣ From four to five 9s of uptime by migrating to Kubernetes

Read it now: https://learnk8s.io/issues/130

⭐️ This newsletter is brought to you by Fairwinds - Expert-led fully managed Kubernetes services, designed for engineering teams who need production-grade infrastructure without the operational burden https://ku.bz/HT6WyTF-H
Post #1354 465
This article explains Kubernetes NetworkPolicies, which control pod traffic at OSI layers 3 and 4.

It covers enforcement via iptables and eBPF, detailing how CNIs like Calico and Cilium apply rules using pod labels, namespaces, and IP blocks.

More: https://ku.bz/lW0TStBL9
Post #1353 374

Forwarded from KubeFM

Discover how Adevinta manages Kubernetes upgrades at scale in this conversation with Tanat.

You will learn:

- How to transition from blue-green to in-place Kubernetes upgrades while maintaining service reliability
- Techniques for tracking and addressing API deprecations using tools like Pluto and Kube-no-trouble
- Strategies for minimizing SLO impact during node rebuilds through serialized approaches and proper PDB configuration
- Why a phased upgrade approach with "cluster waves" provides safer production deployments even with thorough testing

Watch (or listen to) it here: https://ku.bz/VVHFfXGl_

🌟 This episode is brought to you by Learnk8s — get started on your Kubernetes journey through comprehensive online, in-person or remote training https://learnk8s.io/training

With @Birthmarkb "Secret explorer" Farrell
Post #1352 443
In this article, you will learn how Apko can build container images via YAML configuration using the APK package format from Alpine.

It creates small, fast booting images with less memory and disk footprint, thereby reducing security risks.

More: https://gsantoro.dev/apko-from-chainguard
Post #1351 473

Forwarded from KubeFM

Tim Miller CEO and Co-founder at Kusari discusses why implementing robust processes is more critical than relying on scanning tools for secret management.

While multiple scanning approaches (regex and entropy-based) can detect secrets, the priority should be on preventing leaks through SLSA attestations, proper access controls, and using short-lived credentials. This proactive approach addresses the root cause rather than detecting secrets after they've entered repositories.

Watch the full interview: https://ku.bz/-2Sqn9Jb9

This interview is a reaction to Assaf Morag and Yakir Kadkoda's episode https://ku.bz/5RKVBGlQR
Post #1350 2.7K
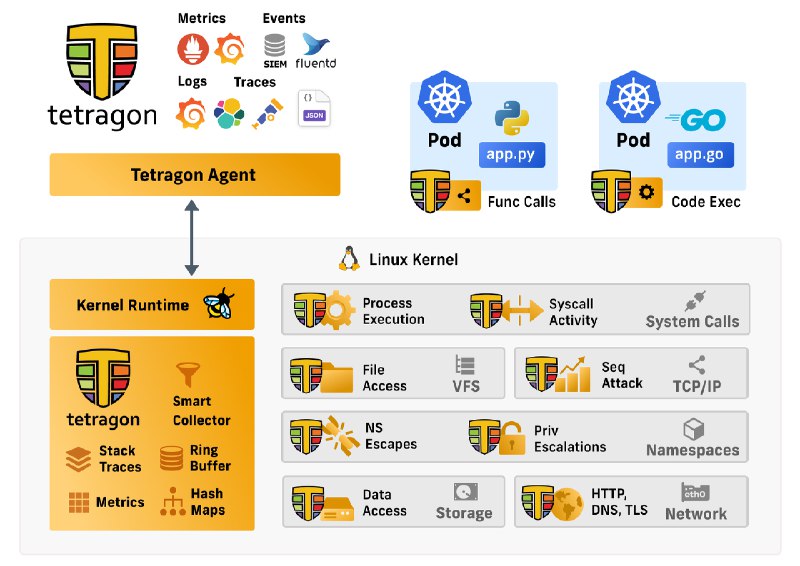
Tetragon enables powerful real-time, eBPF-based security observability and runtime enforcement.

It is Kubernetes-aware and understands identities so that security event detection can be configured in relation to individual workloads.

More: https://github.com/cilium/tetragon
Post #1348 416

Forwarded from KubeFM

Hillai Ben-Sasson and Ronen Shustin, Security Researchers at Wiz, discuss crucial strategies for implementing multi-tenancy in Kubernetes. They emphasize two primary areas:

1. Network Security: Kubernetes does not inherently prevent network access between nodes, making robust network isolation essential.
2. Namespace Separation.

They also highlight the importance of advanced container security technologies, such as GVisor and Kata Containers, to prevent container escapes.

Watch the full episode: https://ku.bz/yr16qNTFx
Post #1347 478
helmper is a Go program that reads Helm Charts from remote OCI registries and pushes the charts container images to your registries with optional OS-level vulnerability patching.

More: https://ku.bz/sjn0NBtXQ
Older posts →
Threads Profile ViewerView any public Threads profile without an account.Open ThreadLook →Writing with AI? Make it sound human.Metric37 rewrites AI drafts so they read naturally. Free AI detector, 1,500 words free.Try Metric37 →