TGViewer
Channel Public Channel
Kubesploit

Kubesploit

@kubesploit

News and links on Kubernetes security curated by the @Learnk8s team
Website: https://kubesploit.io/
Subscribers
2.13K
Photos
961
Videos
208
Links
1.9K

Showing posts older than #1347 · Back to latest

Older Posts 20 shown
Post #1346 488

Forwarded from KubeFM

Jim Bugwadia, Co-Founder & CEO @ Nirmata, explains how policy as code addresses the tension between platform standardization and team autonomy in Kubernetes environments.

He highlights how Kyverno, a policy engine for Kubernetes, enables teams to write declarative policies using CEL and other languages. This approach creates a collaborative framework where developers and security operations teams can work together on policies, striking the right balance between necessary guardrails and self-service capabilities.

Watch the full interview: https://ku.bz/hYZXTmPV9

This interview is a reaction to Calin Florescu's episode https://ku.bz/mcPtH5395
Post #1345 332

Forwarded from LearnKube news

This week on Learn Kubernetes Weekly 129:

🤔 How CoreDNS and NodeLocalDNS Work in a Kubernetes Cluster
👋 Building a container filesytem by hand
🏃‍♀️ Migrating GitLab CI from Docker+Machine to Kubernetes
📈 Scaling a development environment on a budget
💪 Karpenter: The Future of Worker Management and Autoscaling on Kubernetes

Read it now: https://learnk8s.io/issues/129

⭐️ This issue is brought to you by Akamai Cloud — Akamai is offering up to $5,000 in cloud credits to our subscribers (see details inside). Build and deliver low-latency, edge native applications on the world's most distributed cloud computing platform.
Post #1344 1.77K
helm-secrets is a Helm plugin for decrypting encrypted Helm value files on the fly.

- Use SOPS to encrypt value files and store them in git.
- Store your secrets in a cloud native secret manager and inject them into value files or templates.

More: https://ku.bz/jhX4NWYKs
Post #1343 373

Forwarded from KubeFM

Grzegorz, Kubernetes Engineer at Cloud Kitchens, shares his team's journey developing a comprehensive self-healing framework for Kubernetes.

You will learn:

- How managed Kubernetes services like AKS provide benefits but require customization for specific use cases
- The architecture of an effective self-healing framework using DaemonSets and deployments with Kubernetes-native components
- Practical solutions for common challenges like StatefulSet pods stuck on unreachable nodes and cleaning up orphaned pods
- Techniques for workload-level automation, including throttling CPU-hungry pods and automating diagnostic data collection

Watch (or listen to) it here: https://ku.bz/yg_fkP0LN

🌟 This episode is brought to you by Learnk8s — get started on your Kubernetes journey through comprehensive online, in-person or remote training https://learnk8s.io/training

With @Birthmarkb "Making you smile" Farrell
Post #1342 431
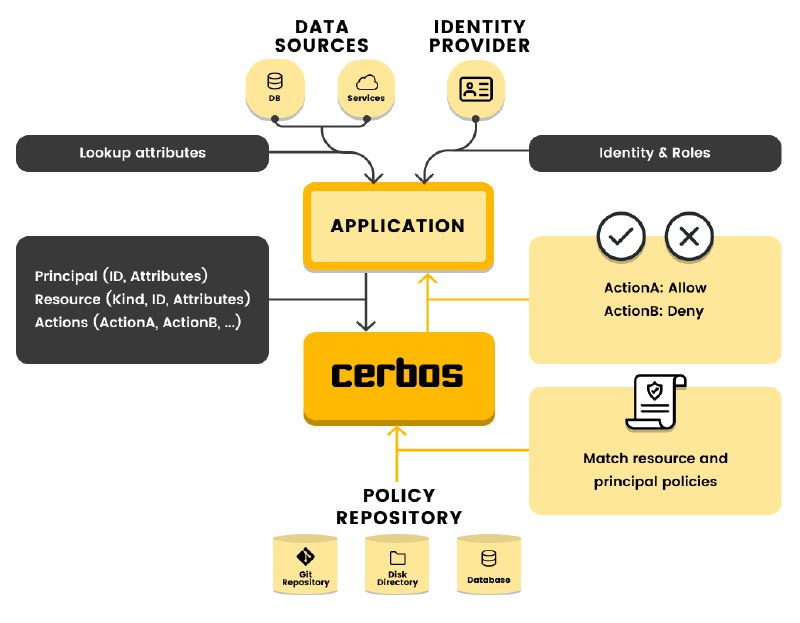
Cerbos is an authorization layer that enables you to define context-aware access control rules for your application resources in simple, intuitive YAML policies managed and deployed via your Git-ops infrastructure.

More: https://ku.bz/_l3Jd0L1b
Post #1341 516
Learn how to secure applications by deploying Keycloak on Kubernetes using Helm, automating user management, implementing strong security policies, and creating a scalable identity infrastructure with minimal manual configuration.

More: https://ku.bz/g3BC2BCw_
Post #1340 424

Forwarded from Kube Events

🚀 KubeCrash is Coming! Mark Your Calendars for May 8th!

KubeCrash brings together open source maintainers and industry experts to share cloud native best practices specifically for platform engineers.

At this event, you'll learn about:

- Platform engineering approaches that work in the real world
- Observability implementation strategies
- Kubernetes management techniques
- Practical solutions used by companies like Intuit, Bloomberg, and Capital One

Join to hear from an exceptional lineup of speakers including @Birthmarkb (KubeFM), Ramiro Berrelleza (Okteto), Guy Menahem (The Platformers Community), and many more.

Plus, it's completely FREE and supports the "Deaf Kids Code" charity.

📆 May 8, 2025
🕓 4 pm CET | 10 am ET | 7 am PT
📍 Online

More info: https://ku.bz/KD73z_cTY
Post #1339 512
Trousseau is an open-source project that leverages the Kubernetes Key Management Service (KMS) provider framework to secure Secrets within the Kubernetes etcd instance using a Transit Key stored within a remote KMS.

More: https://ku.bz/lM2hC3Hkz
Post #1338 555
Integrate Azure Policy with AKS to automatically enforce Kubernetes security standards.

Learn how to use built-in policies, prevent privileged containers, and implement compliance checks across your cluster infrastructure.

More: https://ku.bz/PkGQptrMt
Post #1337 433

Forwarded from LearnKube news

This week on Learn Kubernetes Weekly 128:

🤔 Why Pull Base Images When You Can Build Your Own?
☁️ Scaling in the Clouds: Istio Ambient vs Cilium
🧹 Kubernetes configuration linting tools
♻️ Git happens: how Argo CD took over our deployments
🤗 I Stopped Using Kubernetes: Our DevOps Team Is Happier Than Ever

Read it now: https://learnk8s.io/issues/128

⭐️ This issue is brought to you by Akamai Cloud — build and deliver low-latency, edge native applications on the world's most distributed cloud computing platform https://ku.bz/93rJKSr_V
Post #1336 1.86K
Kubeconform is a Kubernetes manifests validation tool.

Similar to Kubeval, but with the following improvements:

1. High performance.
2. Remote or local schema locations
3. Up-to-date schemas for all recent versions of Kubernetes.

More: https://ku.bz/4MJn8zKDH
Post #1335 409

Forwarded from KubeFM

Andrew Charlton, Staff Software Engineer at Timescale, explains how they replaced Kubernetes StatefulSets with a custom operator called Popper for their PostgreSQL Cloud Platform.

You will learn:

- Why StatefulSets fall short for managing high-availability PostgreSQL clusters, particularly around pod ordering and volume management
- How Timescale's instance matching approach solves complex reconciliation challenges when managing heterogeneous database workloads
- The benefits of implementing discrete, idempotent actions rather than workflows in Kubernetes operators

Watch (or listen to) it here: https://ku.bz/fhZ_pNXM3

🌟 This episode is brought to you by [MetalBear] mirrord — run local code like in your Kubernetes cluster without deploying first https://ku.bz/lHtPqsdjq

With @Birthmarkb "Yo quiero Taco Bell" Farrell
Post #1334 485
In this tutorial, you'll explore an approach to setting up a Keycloak token exchange in a local Kubernetes environment with Istio ingress.

More: https://ku.bz/bqrqDBxNw
Post #1333 597
Sealed Secrets provides declarative Kubernetes Secret Management in a secure way.

Since the Sealed Secrets are encrypted, they can be safely stored in a code repository.

More: https://ku.bz/Gpl8p7ZQB
Post #1332 1.36K
Over 300,000 Prometheus servers and exporters are exposed to the internet without authentication, posing significant security risks, including information disclosure, DoS attacks, and remote code execution through "RepoJacking" vulnerabilities

More: https://ku.bz/kfm9gDp_x
Post #1331 2.08K
KubeLinter is a static analysis tool that checks Kubernetes YAML files and Helm charts to ensure that applications adhere to best practices.

More: https://ku.bz/5V9YXG-Br
Post #1330 481

Forwarded from LearnKube news

This week on Learn Kubernetes Weekly 127:

👯‍♀️ Using database read replicas in distributed systems
🕵️‍♂️ Kubernetes Cluster Networking: Differences Between Flannel and Calico
💰 The value of NGINX Upstreams
🤔 What is ProviderID in Kubernetes, Cluster API, and Cloud Controller Manager?
👌 Improving Kubernetes-Mixin API Server Rules Consistency

Read it now: https://learnk8s.io/issues/127

⭐️ This issue is sponsored by KubeFM — the new Kubernetes podcast episodes are starting next week. Don't miss them! https://kube.fm
Post #1329 526
Confidential Containers simplifies confidential computing via "vault" sealed secrets, managed by Trustee components (KBS, AS, RVPS), ensuring secure secret access within Trusted Execution Environments (TEE) while maintaining Kubernetes compatibility.

More: https://ku.bz/l1LjZVL0W
Post #1327 1.09K
AWS ACM Private CA is a module of the AWS Certificate Manager that can set up and manage private CAs.

This project acts as an addon to cert-manager that signs off certificate requests using AWS PCA.

More: https://ku.bz/jRGYV3XzS
Older posts →
Threads Profile ViewerView any public Threads profile without an account.Open ThreadLook →Writing with AI? Make it sound human.Metric37 rewrites AI drafts so they read naturally. Free AI detector, 1,500 words free.Try Metric37 →