TGViewer
Channel Public Channel
Daily Security

Daily Security

@ethers_security

Admin: @minefolelser
Subscribers
4.02K
Photos
77
Videos
0
Links
278

Showing posts older than #382 · Back to latest

Older Posts 20 shown
Post #381 722

Forwarded from Cointelegraph

🚨 JUST IN: Sui reports a mainnet outage, with the network currently at a standstill as the core team investigates.

News | Markets | YouTube
Post #378 663

Forwarded from Investigations by ZachXBT

Community alert: A number of Trust Wallet users have reported that funds were drained from wallet addresses within the past couple of hours.

While the exact root cause has not been determined coincidentally the Trust Wallet Chrome extension pushed a new update yesterday.

Theft addresses
0x3b09A3c9aDD7D0262e6E9724D7e823Cd767a0c74
0x463452C356322D463B84891eBDa33DAED274cB40
0xa42297ff42a3b65091967945131cd1db962afae4

0xe072358070506a4DDA5521B19260011A490a5aaA
0xc22b8126ca21616424a22bf012fd1b7cf48f02b1
bc1qjj7mj50s2e38m4nn7pt2j0ffddxmuxh2g8tyd8
bc1ql9r9a4uxmsdwkenjwx7t5clslsf62gxt8ru7e8

bc1q4g8u7kctk6f2x3f6nh43x76qm4fd0xyv3jugdy
bc1qw7s35umfzgcc7nmjdj9wsyuy9z3g6kqjr0vc7w
bc1qgccgl9d0wzxxnvklj4j55wqeqczgkn6qfcgjdg
bc1q3ykewj0xu0wrwxd2dy4g47yp75gxxm565kaw6m

Send me a DM on X (Twitter) if you were affected and I will update the list of theft addresses as I verify more.
Post #377 758
Post #376 833

Forwarded from Viktor🔮

FHE (Fully Homomorphic Encryption in Practice) Webinar

Join
  • ❤ 2
Post #375 702
Might be interesting for you 🙏
Post #374 838

Forwarded from Security Harvester

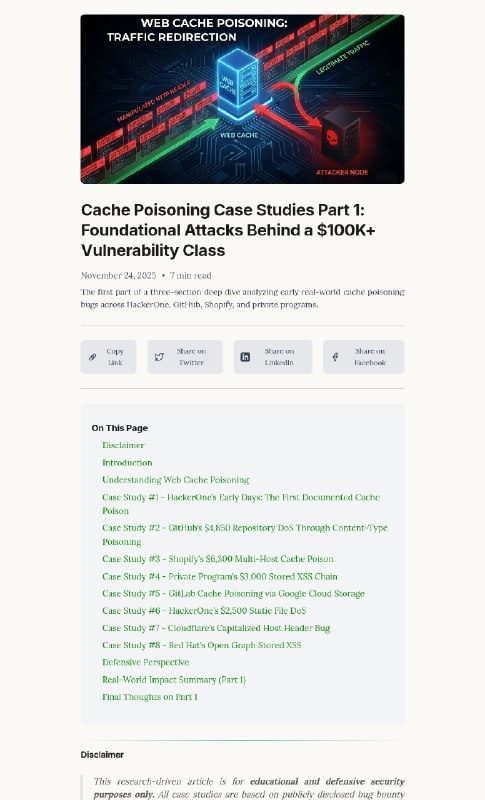
Analysis of 8 Foundational Cache Poisoning Attacks (HackerOne, GitHub, Shopify) - Part 1
https://herish.me/blog/cache-poisoning-case-studies-part-1-foundational-attacks/:

1. The first part of a three-section deep dive analyzing early real-world cache poisoning bugs across HackerOne, GitHub, Shopify, and private programs.
2. Although it once appeared niche, cache poisoning has evolved into a high-impact attack vector affecting CDNs, cloud platforms, server frameworks, and multi-tenant SaaS providers.
3. These early reports demonstrate not only how straightforward misconfigurations can lead to devastating effects, but also how attackers learned to weaponize headers, request behaviors, and cache key inconsistencies to breach platforms with millions of users.

@secharvester
Post #371 678

Forwarded from AISecHub

AI-Powered CAPTCHA Solver

This project is a Python-based command-line tool that uses large multimodal models (LMMs) like OpenAI's GPT-4o and Google's Gemini to automatically solve various types of CAPTCHAs. It leverages Selenium for web browser automation to interact with web pages and solve CAPTCHAs in real-time.

https://github.com/aydinnyunus/ai-captcha-bypass
GitHub GitHub - aydinnyunus/ai-captcha-bypass: AI Captcha Bypass AI Captcha Bypass. Contribute to aydinnyunus/ai-captcha-bypass development by creating an account on GitHub.
  • 🤝 3
Post #369 555
Worth a read
Post #368 760

Forwarded from AISecHub

12 LLM CTFs & Challenges - https://taleliyahu.medium.com/llm-ctfs-challenges-03dd55a9b7e4

Hands on CTFs and labs for LLM security. Train on prompt injection, jailbreaks, guardrail bypass, tool and agent abuse, data leaks, model inversion, and MCP issues.
Medium LLM CTFs & Challenges LLM CTFs & Challenges Hands on CTFs and labs for LLM security. Train on prompt injection, jailbreaks, guardrail bypass, tool and agent abuse, data leaks, model inversion, and MCP issues. Join the AI …
  • ❤ 2
  • 🔥 2
Post #366 523
be careful)
Post #365 627

Forwarded from Netlas.io

📌 LLM Vulnerabilities: how AI apps break — and how to harden them

This piece maps the most common ways LLM-powered systems fail in the real world and turns them into a practical hardening plan. From prompt and indirect injection to over-privileged tools, leaky RAG pipelines, data poisoning, jailbreaks, and supply-chain traps — plus the guardrails that actually help in production.

Key takeaways:
1️⃣ Prompt & indirect injection: attackers hide instructions in web pages, files, or retrieved notes; the model obeys them and exfiltrates secrets or performs unwanted actions.
2️⃣ Jailbreaks & policy evasion: harmless-looking reformulations bypass safety layers; outputs become unsafe or operationally risky.
3️⃣ RAG data leaks: sloppy retrieval exposes internal docs, customer data, and system prompts; cross-tenant bleed is a real risk.
4️⃣ Over-privileged tools/agents: broad filesystem, network, or payment permissions turn one prompt into a breach.
5️⃣ Poisoning & supply chain: tainted datasets, third-party prompts, and unpinned models/extensions undermine trust.
6️⃣ Output trust & hallucinations: fabricated facts sneak into workflows, tickets, or code — and humans often rubber-stamp them.
7️⃣ Telemetry gaps: without red-team sims and runtime monitoring, you won’t see injection attempts until damage is done.

👉 Read here: https://netlas.io/blog/llm_vulnerabilities/
netlas.io LLM Vulnerabilities: Why AI Models Are the Next Big Attack Surface - Netlas Blog LLM vulnerabilities explained: prompt injection, data leaks, RAG risk, supply chain, and real incidents — plus OWASP guidance, mitigations, and testing tactics.
  • ❤ 2
Post #363 470
Post #362 596

Forwarded from Atoms Research

🔴 Balancer Exploit Update

The project team commented on the incident:

We’re aware of a potential exploit impacting Balancer v2 pools.

Our engineering and security teams are investigating with high priority.

We’ll share verified updates and next steps as soon as we have more information.


🫡 Atoms Research | ✈️ Boost | 💬 Chat
  • ❤ 1
Older posts →
Threads Profile ViewerView any public Threads profile without an account.Open ThreadLook →Writing with AI? Make it sound human.Metric37 rewrites AI drafts so they read naturally. Free AI detector, 1,500 words free.Try Metric37 →