TGViewer
Channel Public Channel
CloudSec Wine

CloudSec Wine

@cloud_sec

All about cloud security

Contacts:
@AMark0f
@dvyakimov

About DevSecOps:
@sec_devops
Subscribers
2.27K
Photos
1.1K
Videos
0
Links
1.4K

Showing posts older than #738 · Back to latest

Older Posts 20 shown
Post #733 667
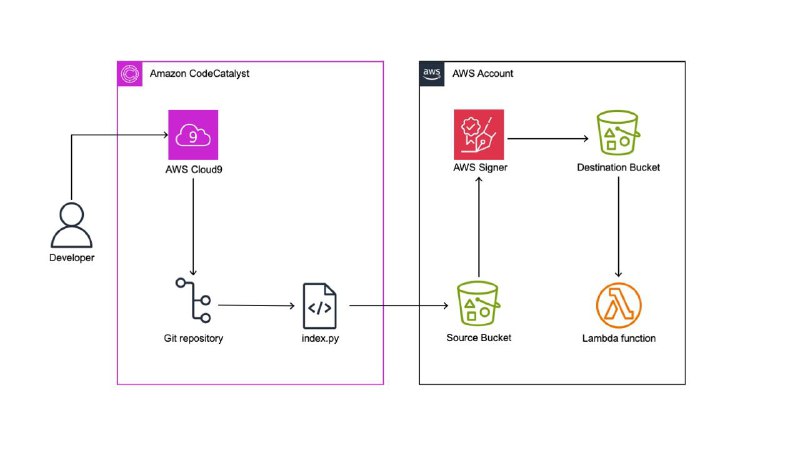
🔶 Remote analysis on cloud object-storage

The journey of making the volatility3 framework compatible with S3 object-storage to perform memory analysis over the network.

https://www.forensicxlab.com/posts/vols3/

#aws
  • 👍 4
  • ❤ 1
  • 🔥 1
Post #732 785
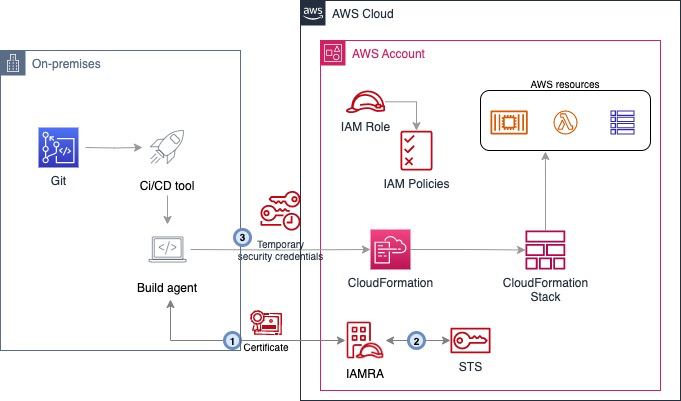
🔶 AWS's Hidden Threat: AMBERSQUID Cloud-Native Cryptojacking Operation

The Sysdig Threat Research Team (TRT) has uncovered a novel cloud-native cryptojacking operation which they've named AMBERSQUID. This operation leverages AWS services not commonly used by attackers, such as AWS Amplify, AWS Fargate, and Amazon SageMaker.

https://sysdig.com/blog/ambersquid/

(Use VPN to open from Russia)

#aws
  • 👍 3
  • ❤ 1
  • 🔥 1
Post #731 733
🔴 Maintaining persistence via Shared sessions on Cloud Workstations

When an owner initiates a session and performs actions like gcloud auth login, the session state persists, shared across multiple users accessing the workstation through the same URL. This means that any user with access to the workstation can view and interact with the session artifacts created by the owner.

https://saransh-rana.gitbook.io/aboutme/maintaining-persistence-via-shared-sessions-on-cloud-workstations

#gcp
  • 👍 3
  • ❤ 1
  • 🔥 1
Post #725 701
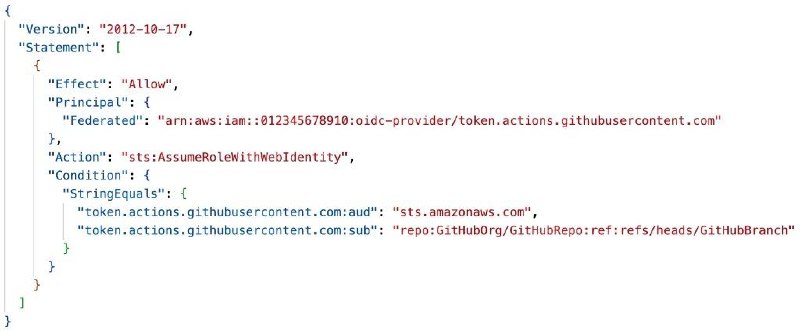
🔶 A security community success story of mitigating a misconfiguration

Learn about the process of preventing security issues by changing things outside of your environment by looking at how a misconfiguration was occurring when Github Actions were integrated with AWS IAM roles and the improvements made that have now made this misconfiguration much less likely.

https://www.wiz.io/blog/a-security-community-success-story-of-mitigating-a-misconfiguration

#aws
  • 🔥 4
  • ❤ 1
  • 👍 1
Post #718 898
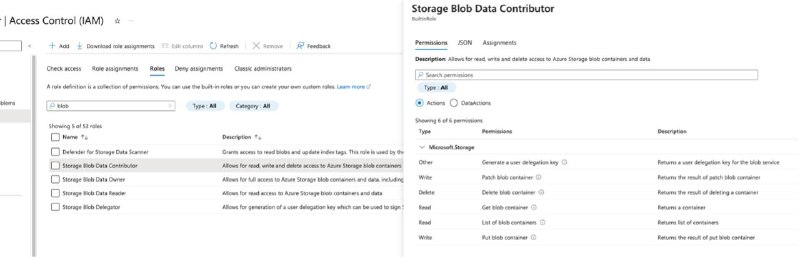
🔶🔷🔴 New Attack Vector In The Cloud: Attackers caught exploiting Object Storage Services

Security Joes Incident Response team recently became aware of a set of relatively new CVEs that were released at the end of March 2023. Surprisingly, these vulnerabilities have received little to no media coverage regarding their ease of exploitation and the potential security implications they pose to any cluster running a non-native object storage.

https://www.securityjoes.com/post/new-attack-vector-in-the-cloud-attackers-caught-exploiting-object-storage-services

#aws #azure #gcp
  • 👍 3
  • 🔥 1
  • 👏 1
Older posts →
Threads Profile ViewerView any public Threads profile without an account.Open ThreadLook →Writing with AI? Make it sound human.Metric37 rewrites AI drafts so they read naturally. Free AI detector, 1,500 words free.Try Metric37 →