TGViewer
Channel Public Channel
CloudSec Wine

CloudSec Wine

@cloud_sec

All about cloud security

Contacts:
@AMark0f
@dvyakimov

About DevSecOps:
@sec_devops
Subscribers
2.27K
Photos
1.1K
Videos
0
Links
1.4K

Showing posts older than #697 · Back to latest

Older Posts 20 shown
Post #692 646
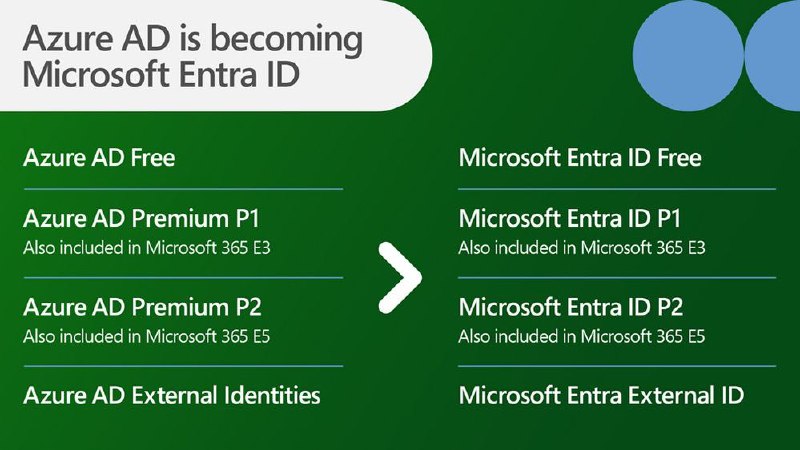
🔷 Microsoft Entra Workload ID - Introduction and Delegated Permissions

Post providing an overview about some aspects and features which are important in delegating management of Workload ID in Microsoft Entra: Who can see and create apps? Why you should avoid assigning owners to service principals or application objects?

https://www.cloud-architekt.net/entra-workload-id-introduction-and-delegation

#azure
  • 👍 4
  • 🔥 1
  • 😱 1
Post #682 711
🔶 Abusing Amazon VPC CNI plugin for Kubernetes

The article discusses a security vulnerability in the Amazon VPC CNI plugin, used by Amazon EKS. The flaw allows an attacker to move laterally to other VPCs in the AWS account.

https://www.elttam.com/blog/amazon-vpc-cni/

#aws
  • 👍 2
  • ❤ 1
  • 🔥 1
Post #680 686
🔶 How to Monitor AWS IAM Root Users at Scale: Best Practices

CloudYali provides insights into best practices and effective strategies for managing IAM users at scale. The article delves into IAM user monitoring, emphasising the importance of the root user, and highlighting essential IAM security practices. It also covers automation of IAM Credential Report generation at scale, streamlining the collection of IAM user information and facilitating more efficient monitoring and management for cloud teams.

https://www.cloudyali.io/blogs/how-to-monitor-aws-iam-root-users-at-scale-best-practices?utm_source=tldrsec.com&utm_medium=referral&utm_campaign=tl-dr-sec-191-badzure-detection-response-pipelines-18k-subscribers

#aws
  • 👍 2
  • 🔥 1
  • 👏 1
Post #676 627
🔷 Microsoft mitigates China-based threat actor Storm-0558 targeting of customer email

Microsoft has mitigated an attack by a China-based threat actor Microsoft tracks as Storm-0558 which targeted customer emails. Storm-0558 primarily targets government agencies in Western Europe and focuses on espionage, data theft, and credential access.

https://msrc.microsoft.com/blog/2023/07/microsoft-mitigates-china-based-threat-actor-storm-0558-targeting-of-customer-email/

#azure
  • ❤ 2
  • 👍 2
  • 🔥 1
Older posts →
Threads Profile ViewerView any public Threads profile without an account.Open ThreadLook →Writing with AI? Make it sound human.Metric37 rewrites AI drafts so they read naturally. Free AI detector, 1,500 words free.Try Metric37 →