TGViewer
Channel Public Channel
CloudSec Wine

CloudSec Wine

@cloud_sec

All about cloud security

Contacts:
@AMark0f
@dvyakimov

About DevSecOps:
@sec_devops
Subscribers
2.27K
Photos
1.1K
Videos
0
Links
1.4K

Showing posts older than #635 · Back to latest

Older Posts 20 shown
Post #633 728
🔶🔷 Manage multiple Terraform projects in monorepo

A look at one possible way to organize and manage a monorepo setup, which will contain multiple projects and Terraform modules, with deployments spanning across multiple targets such as AWS accounts or Azure subscriptions.

https://janik6n.net/posts/manage-multiple-terraform-projects-in-monorepo

#aws #azure
  • 🔥 2
  • 👍 1
  • 😱 1
Post #632 620
🔶 An AWS IAM Wishlist

A wishlist of AWS IAM feature requests: IAM Authorization Debugging, Mapping of API Calls/IAM Permissions/CloudTrail Events, SCP Audit Mode, SCP for Resources, and API Request Parameters as Condition Keys.

https://www.zeuscloud.io/post/an-aws-iam-wishlist

#aws
  • 🔥 3
  • 👍 1
  • 👏 1
Post #631 617
🔴 Cloud Run Security design overview

This article outlines the security features provided by Cloud Run, including automatic TLS encryption, secure communication between services, and integration with Cloud IAM for access control.

https://cloud.google.com/run/docs/securing/security

#gcp
  • 👍 2
  • 🔥 2
  • 👏 1
Post #630 634
Call for Papers for DevOops 2023 is open until June 1st.

The conference will run for four days: September 5–6 online and September 17–18 in Moscow, with the option to join online.

Want to share your DevOps experience? Submit your proposal at DevOops 2023.

All you need is the material and the desire to perform, and the organizers will help at every stage, from idea to performance: they'll work with you on the material, conduct rehearsals, and give recommendations on the presentation.

Choose any presentation format—talk, workshop, interview, discussion, BoF session—or come up with something of your own. You can select a topic from the list or propose your own.

Submit your proposal on the DevOops website.

#advertising
  • 🔥 3
  • 👍 2
  • 👏 1
Post #629 621
🔶 My Love/Hate Relationship with Cloud Custodian

Cloud Custodian is a powerful tool for managing and enforcing policies in cloud environments, but it can be difficult to learn and use effectively. The author shares their experiences with using Cloud Custodian, including its benefits and drawbacks, and offers tips for getting started with the tool.

https://badshah.io/my-love-hate-relationship-with-cloud-custodian

#aws
  • 👍 3
  • 🔥 2
  • 👏 1
Post #628 712
🔶🔷🔴 Cloudy with a Chance of Bad Logs: Cloud Platform Log Configurations to Consider in Investigations

Post describing a hypothetical scenario of a cloud platform compromise with multiple components that would require investigation. Each component is an example of a real intrusion tactic that Mandiant has investigated across various cloud platforms, sometimes with logs available and sometimes without logs available.

https://www.mandiant.com/resources/blog/cloud-bad-log-configurations

#aws #azure #gcp
  • 👍 3
  • 🔥 1
  • 👏 1
Post #627 723
🔷 Azure Future SIEM

Great visualization of the future Microsoft Sentinel architecture using Microsoft's cloud-based Azure infrastructure!

#azure
  • 🔥 4
  • 👍 1
  • 👏 1
Post #621 694
🔶 When MFA becomes SFA

A particular case where possession of an AWS access key/secret key alone was equivalent to possession of those keys and a previously configured MFA.

* P. S. use VPN for Russian IPs *

https://www.mwrcybersec.com/when-mfa-becomes-sfa

#aws
  • 👍 5
  • 🔥 2
  • 👏 1
Post #620 633
🔴 GhostToken: Exploiting GCP application infrastructure to create invisible, unremovable trojan app on Google accounts

The vulnerability could allow threat actors to change a malicious application to be invisible and unremovable, effectively leaving the victim's Google account infected with a trojan app forever.

https://astrix.security/ghosttoken-exploiting-gcp-application-infrastructure-to-create-invisible-unremovable-trojan-app-on-google-accounts

#gcp
  • 👍 2
  • 🔥 1
  • 👏 1
Post #619 665
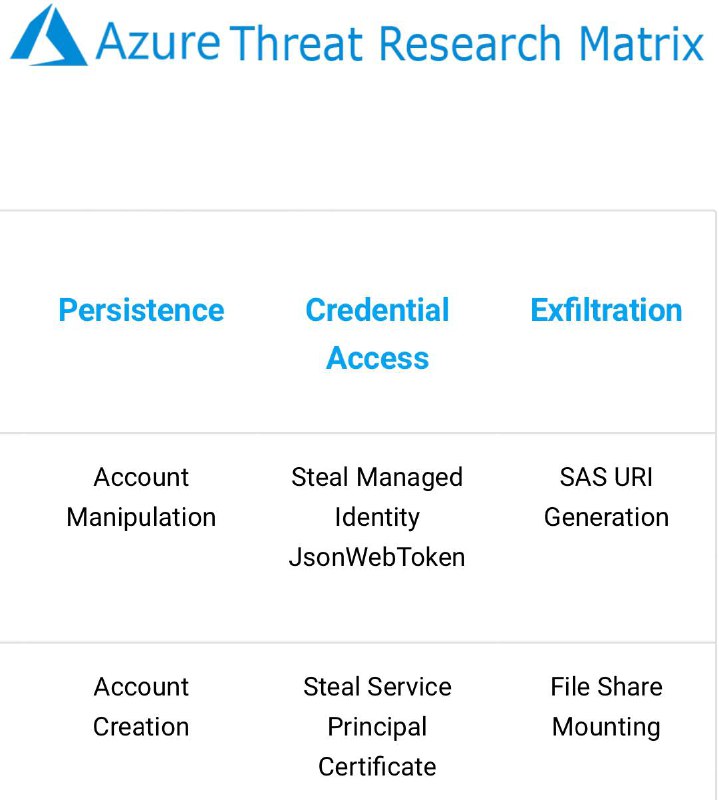
🔷 Azure Threat Research Matrix

The purpose of the Azure Threat Research Matrix (ATRM) is to conceptualize the known tactics, techniques, and procedures (TTP) that adversaries may use against the Azure platform.

https://microsoft.github.io/Azure-Threat-Research-Matrix

#azure
  • 🔥 3
  • 👍 1
  • 👏 1
Post #616 661
🔴 Asset Key Thief security vulnerability technical details

A persistent Service Account private key exfiltration privilege escalation technique that potentially affected Google Cloud Service Accounts, now remediated promptly by the Google Cloud team.

https://engineering.sada.com/asset-key-thief-disclosure-cfae4f1778b6

#gcp
  • 👍 3
  • 🔥 3
  • ❤ 1
  • 😱 1
Post #615 602
🔶 New Phone, Who Dis? How Cloud Environments Are Exploited for Smishing Campaigns

Commodity threat actors have recently begun to exploit cloud environments for smishing campaigns, employing techniques strikingly similar to those used in SES enumeration and abuse.

https://permiso.io/blog/s/smishing-attack-on-aws-sms-new-phone-who-dis

#aws
  • 🔥 2
  • 👍 1
  • 👏 1
Older posts →
Threads Profile ViewerView any public Threads profile without an account.Open ThreadLook →Writing with AI? Make it sound human.Metric37 rewrites AI drafts so they read naturally. Free AI detector, 1,500 words free.Try Metric37 →