TGViewer
Channel Public Channel
CloudSec Wine

CloudSec Wine

@cloud_sec

All about cloud security

Contacts:
@AMark0f
@dvyakimov

About DevSecOps:
@sec_devops
Subscribers
2.27K
Photos
1.1K
Videos
0
Links
1.4K

Showing posts older than #515 · Back to latest

Older Posts 20 shown
Post #513 708
Post #511 687
🔷 Abusing tcp tunneling in Azure Bastion

How Azure Bastion Native Client support works, and how an adversary could abuse this feature to perform attacks against Azure VMs over private IP addresses, without having direct network connectivity to the VM.

https://codyburkard.com/blog/bastionabuse

#azure
  • 🔥 2
Post #509 641
🔷 Token tactics: How to prevent, detect, and respond to cloud token theft

As organizations increase their coverage of multifactor authentication (MFA), threat actors have begun to move to more sophisticated techniques to allow them to compromise corporate resources without needing to satisfy MFA. Recently, the Microsoft Detection and Response Team (DART) has seen an increase in attackers utilizing token theft for this purpose.

https://www.microsoft.com/en-us/security/blog/2022/11/16/token-tactics-how-to-prevent-detect-and-respond-to-cloud-token-theft

#azure
  • 🔥 2
Post #505 945
🔶 FivexL's Reaction to the AWS Security Baseline for Startups

FivexL shares its outlook on AWS Security Guidelines for startups. Find out how to improve your AWS security efficiently.

https://fivexl.io/blog/fivexl-reaction

#aws
  • 👍 2
Post #503 757
🔷 Bypassing Azure AD home tenant MFA and CA

Because of the Azure AD authentication platform architecture, users can bypass home tenant MFA and CA policies when logging in directly to resource tenants.

https://aadinternals.com/post/ests

#azure
  • 🔥 2
Post #502 802
🔶 AWS security assessment: what scanners are missing and how threat modeling may help you?

SoftServe’s Pawel Rzepa discusses what scanners are missing and why he think tools cannot fully replace a human assessor in performing an effective AWS security assessment. Key points: scanners lack context, more findings don’t mean a better result, scanners may have security check gaps, skipped data flows and relations. Address these gaps via threat modeling.

https://towardsaws.com/aws-security-assessment-what-scanners-are-missing-and-how-threat-modeling-may-help-you-6a76c1c843f3

#aws
  • 👍 3
Post #497 752
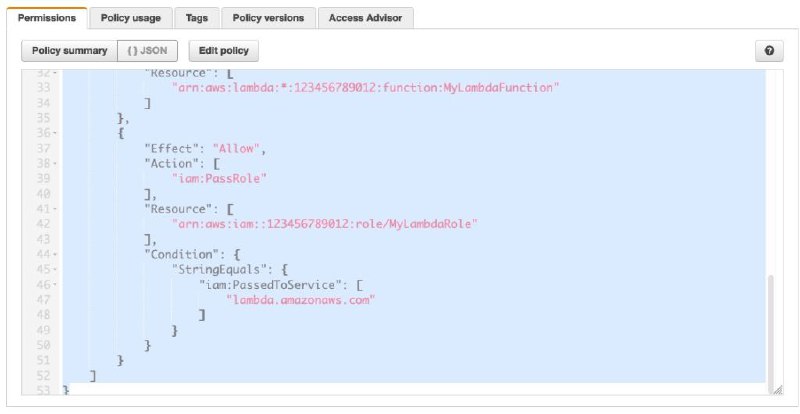
🔶 Use IAM Access Analyzer policy generation to grant fine-grained permissions for your AWS CloudFormation service roles

IAM Access Analyzer policy generation creates fine-grained policies based on your AWS CloudTrail access activity—for example, the actions you use with ECS, Lambda and S3. AWS has expanded policy generation capabilities to support the identification of actions used from over 140 services, including CloudFormation, DynamoDB, and SQS.

https://aws.amazon.com/ru/blogs/security/use-iam-access-analyzer-policy-generation-to-grant-fine-grained-permissions-for-your-aws-cloudformation-service-roles
  • 🔥 1
Older posts →
Threads Profile ViewerView any public Threads profile without an account.Open ThreadLook →Writing with AI? Make it sound human.Metric37 rewrites AI drafts so they read naturally. Free AI detector, 1,500 words free.Try Metric37 →