TGViewer
Channel Public Channel
CloudSec Wine

CloudSec Wine

@cloud_sec

All about cloud security

Contacts:
@AMark0f
@dvyakimov

About DevSecOps:
@sec_devops
Subscribers
2.27K
Photos
1.1K
Videos
0
Links
1.4K

Showing posts older than #430 · Back to latest

Older Posts 20 shown
Post #425 1.33K
🔶 AWS Security by Dylan Shields

An excellent book by software engineer working on Quantum Computing at Amazon Dylan Shields describing that running your systems in the cloud doesn’t automatically make them secure. Learn the tools and new management approaches you need to create secure apps and infrastructure on AWS.

#aws
  • 🔥 3
  • ❤ 2
Post #424 779
🔶 Dependency confusion in AWS CodeArtifact

At the time of the finding Code Artifact did not have any features to specify which packages were internal and therefore should not be pulled from public repositories.

https://zego.engineering/dependency-confusion-in-aws-codeartifact-86b9ff68963d?gi=eb56bfabbd85

#aws
Medium Dependency confusion in AWS CodeArtifact Last year we found AWS Code Artifact to be vulnerable to dependency confusion. This blogs covers the disclosure and remediation process.
  • 👏 1
Post #422 806
🔶 IAM-Deescalate: An Open Source Tool to Help Users Reduce the Risk of Privilege Escalation

Palo Alto Networks Jay Chen describes IAM-Deescalate, a tool to mitigate privilege escalation risks in AWS. It first identifies the users and roles with privilege escalation risks using PMapper.

For each risky principal, IAM-Deescalate calculates a minimal set of permissions granted to this principal that can be revoked to eliminate the risks. IAM-Deescalate inserts an inline policy to explicitly deny the risky permissions that could allow the principal to escalate to administrator privilege.

https://unit42.paloaltonetworks.com/iam-deescalate

#aws
Unit 42 IAM-Deescalate: An Open Source Tool to Help Users Reduce the Risk of Privilege Escalation We developed an open source tool, IAM-Deescalate, to help mitigate the privilege escalation risks of overly permissive identities in AWS.
  • 🔥 2
Post #420 773
🔶 Hacking an AWS hosted Kubernetes backed product, and failing

Tales from a recent pentest of a product hosted on the AWS cloud backed by Kubernetes (EKS) and a whole lot of secure design goodness that withstood attack attempts.

https://blog.appsecco.com/hacking-an-aws-hosted-kubernetes-backed-product-and-failing-904cbe0b7c0d

#aws
Medium Hacking an AWS hosted Kubernetes backed product, and failing Tales from a recent pentest of a product hosted on the AWS cloud backed by Kubernetes (EKS) and a whole lot of secure design goodness that…
  • 🔥 2
  • 👍 1
Post #418 861
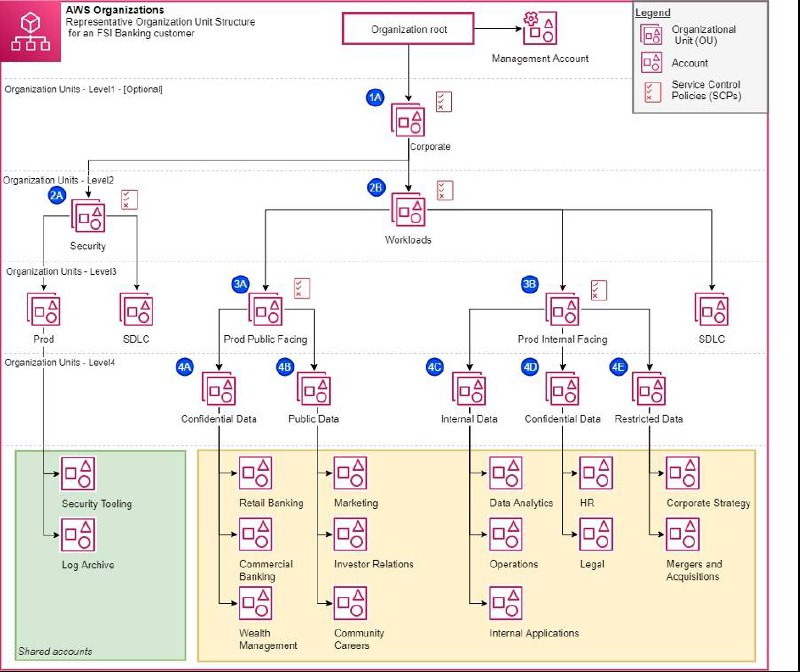
🔶 Best Practices for AWS Organizations Service Control Policies in a Multi-Account Environment

AWS’s Rajeswari Malladi and People’s United Bank’s Jim Kozlowski provide a representative organization unit (OU) structure for a financial services industry customer, and also best practice guidance and starter service control policies (SCPs) to consider in a multi-account AWS environment to establish governance and control.

https://aws.amazon.com/ru/blogs/industries/best-practices-for-aws-organizations-service-control-policies-in-a-multi-account-environment

#aws
  • 🔥 1
Post #417 806
(in Russian)

Встречайте наше первое небольшое, но полноценное мероприятие по облачной безопасности в гибридном формате в уютном (но пока еще тайном) месте в центре летней Москвы.

Ждем с нетерпением инженеров по безопасности, директоров по ИБ, специалистов по DevSecOps, security инженеров и всех, кто интересуется этой тематикой.

На офлайн-мероприятие приглашаем участников нашего чата по безопасности, которые зарегистрируются в форме ниже. Мероприятие бесплатное.

Для тех, кто не сможет посетить нас очно, мы организуем трансляцию мероприятия.

Подробнее о мероприятии →
Творческое объединение WIP, Яузский бул., 11, стр. 1

#advertising
  • 👍 8
  • 👎 8
Post #415 694
🔶 Abusing the Replicator: Silently Exfiltrating Data with the AWS S3 Replication Service

A comprehensive backup strategy is a cornerstone of any DR plan. But how would you distinguish between legitimate backup activity and malicious data exfiltration?

https://www.vectra.ai/blogpost/abusing-the-replicator-silently-exfiltrating-data-with-the-aws-s3-replication-service

#aws
www.vectra.ai Abusing the Replicator: Silently Exfiltrating Data with the AWS S3 Replication Service by Kat Traxler A comprehensive backup strategy is a cornerstone of any DR plan. But how would you distinguish between legitimate backup activity and malicious data exfiltration?
  • 🔥 1
Post #414 649
🔷 Azure’s Security Vulnerabilities Are Out of Control

Azure's multiple security vulnerabilities are highly concerning, for both customer data and the cloud's reputation. It's time we put public pressure on Azure.

https://www.lastweekinaws.com/blog/azures_vulnerabilities_are_quack

#azure
Last Week in AWS Azure’s Security Vulnerabilities Are Out of Control Azure's multiple security vulnerabilities are highly concerning, for both customer data and the cloud's reputation. It's time we put public pressure on Azure.
  • 😱 1
Post #413 720
Post #412 1.06K
🔶aidansteele/openrolesanywhere

An open-source proof-of-concept client for AWS IAM Roles Anywhere by Aidan Steele. Unlike the official client, this project lets you use private keys stored in an SSH agent. This is more flexible - and more secure if you use something like Secretive which stores unexportable keys in the macOS Secure Enclave hardware.

https://github.com/aidansteele/openrolesanywhere

#aws
GitHub GitHub - aidansteele/openrolesanywhere: Open-source proof-of-concept client for AWS IAM Roles Anywhere Open-source proof-of-concept client for AWS IAM Roles Anywhere - aidansteele/openrolesanywhere
  • 👍 1
Older posts →
Threads Profile ViewerView any public Threads profile without an account.Open ThreadLook →Writing with AI? Make it sound human.Metric37 rewrites AI drafts so they read naturally. Free AI detector, 1,500 words free.Try Metric37 →