TGViewer
Channel Public Channel
CloudSec Wine

CloudSec Wine

@cloud_sec

All about cloud security

Contacts:
@AMark0f
@dvyakimov

About DevSecOps:
@sec_devops
Subscribers
2.27K
Photos
1.1K
Videos
0
Links
1.4K

Showing posts older than #326 · Back to latest

Older Posts 20 shown
Post #324 814
🔷 Abusing Family Refresh Tokens for Unauthorized Access and Persistence in Azure Active Directory

Undocumented functionality in Azure Active Directory allows a group of Microsoft OAuth client applications to obtain special "family refresh tokens", which can be redeemed for bearer tokens as any other client in the family.

https://github.com/secureworks/family-of-client-ids-research

#azure
GitHub GitHub - secureworks/family-of-client-ids-research: Research into Undocumented Behavior of Azure AD Refresh Tokens Research into Undocumented Behavior of Azure AD Refresh Tokens - secureworks/family-of-client-ids-research
Post #323 768
🔷 Escalating from Logic App Contributor to Root Owner in Azure

Having Contributor access to an Azure Resource Manager (ARM) API Connection would allow you to create arbitrary role assignments as the connected user. This was supposed to be limited to actions at the Resource Group level, but an attacker could escape to the Subscription or Root level with a path traversal payload.

https://www.netspi.com/blog/technical/cloud-penetration-testing/azure-logic-app-contributor-escalation-to-root-owner

#azure
NetSPI Escalating from Logic App Contributor to Root Owner in Azure Discover how a penetration test led to gaining owner access at the root level of a tenant in Azure. Read on for a walkthrough and disclosure to MSRC.
Post #322 738
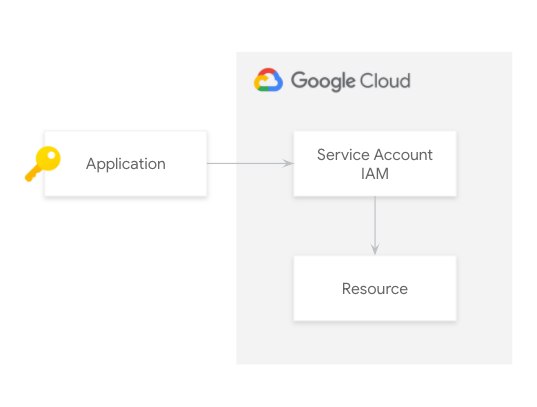
🔴 Lateral Movement in Google Cloud: Abusing the Infamous Default Service Account Misconfiguration

This post covers how a malicious actor can conduct lateral movement in Google Cloud across compute engine instances using the default service account.

https://orca.security/resources/blog/lateral-movement-google-cloud-default-service-account

#gcp
Orca Security Google Cloud: Default Service Account Misconfiguration This post covers how a malicious actor can conduct lateral movement in Google Cloud across compute engine instances using the default service account.
Post #321 721
🔷 AutoWarp: Critical Cross-Account Vulnerability in Microsoft Azure Automation Service

AutoWarp is a critical vulnerability in Microsoft Azure Automation Service that allows unauthorized access to other customer accounts using the service.

https://orca.security/resources/blog/autowarp-microsoft-azure-automation-service-vulnerability

#azure
Orca Security AutoWarp: Azure Automation Vulnerability | Orca Research Pod AutoWarp is a critical vulnerability in Microsoft Azure Automation Service that allows unauthorized access to other customer accounts using the service.
Post #320 734
🔶🔷🔴 CVE-2022-0847 (aka Dirty Pipe): What does it mean for defenders

A quick summary and actionable advice for defenders of cloud environments and those teams who are asked to determine the impact of CVE-2022-0847 on their company's infrastructure.

https://www.marcolancini.it/2022/blog-cve-2022-0847-dirty-pipe

#aws #azure #gcp
Post #317 732
Post #316 761
🔶 awslabs/aws-cloudsaga

Tool to test security controls and alerts within your AWS environment, using generated alerts based on security events seen by the AWS Customer Incident Response Team (CIRT).

https://github.com/awslabs/aws-cloudsaga

#aws
GitHub GitHub - awslabs/aws-cloudsaga: AWS CloudSaga - Simulate security events in AWS AWS CloudSaga - Simulate security events in AWS. Contribute to awslabs/aws-cloudsaga development by creating an account on GitHub.
Post #311 1.47K
🔶🔷🔴 Cloud 9: Top Cloud Penetration Testing Tools

Here are nine cloud pen testing tools use by pentesters in 2022, and additional resources for enhancing your cloud pentesting skills.

https://bishopfox.com/blog/cloud-pen-testing-tools

#aws #azure #gcp
Bishop Fox Cloud 9: Top Cloud Penetration Testing Tools Here are nine of our favorite cloud pen testing tools use by our pen testers in 2022 and additional resources for enhancing your cloud pen testing skills.
Post #310 700
🔶 Are AWS account IDs sensitive information?

One of the often-debated questions in AWS is whether AWS account IDs are sensitive information or not and the question has been oddly-difficult to answer definitively.

https://www.lastweekinaws.com/blog/are-aws-account-ids-sensitive-information/

#aws
Last Week in AWS Are AWS account IDs sensitive information? One of the often-debated questions in AWS is whether AWS account IDs are sensitive information or not and the question has been oddly-difficult to answer
Post #309 697
🔷🔴 Google Cloud: configuring workload identity federation with Azure

How to configure workload identity federation with Azure (OIDC-compliant IdP) so workloads running on an Azure VM can impersonate a service account to perform operations on a Google Cloud resource.

https://medium.com/google-cloud/configuring-workload-identity-federation-with-azure-672a1e1f3eec

#azure #gcp
Medium Google Cloud: configuring workload identity federation with Azure The most straightforward way for workloads running outside of Google Cloud to call Google Cloud APIs is by using a downloaded service…
Post #308 4.35K
Post #307 744
Post #306 683
Older posts →
Threads Profile ViewerView any public Threads profile without an account.Open ThreadLook →Writing with AI? Make it sound human.Metric37 rewrites AI drafts so they read naturally. Free AI detector, 1,500 words free.Try Metric37 →