TGViewer
Channel Public Channel
CloudSec Wine

CloudSec Wine

@cloud_sec

All about cloud security

Contacts:
@AMark0f
@dvyakimov

About DevSecOps:
@sec_devops
Subscribers
2.27K
Photos
1.1K
Videos
0
Links
1.4K

Showing posts older than #182 · Back to latest

Older Posts 20 shown
Post #181 901
🔶 Inside Figma: securing internal web apps

A deep-dive into how Figma built a system for securing internal web applications that lets them require SSO authentication, enforce fine-grained authorization (via Okta groups), and support CLI tools, all using ALBs, AWS Cognito, and Okta.

https://www.figma.com/blog/inside-figma-securing-internal-web-apps/

#aws
Post #179 699
Post #176 978
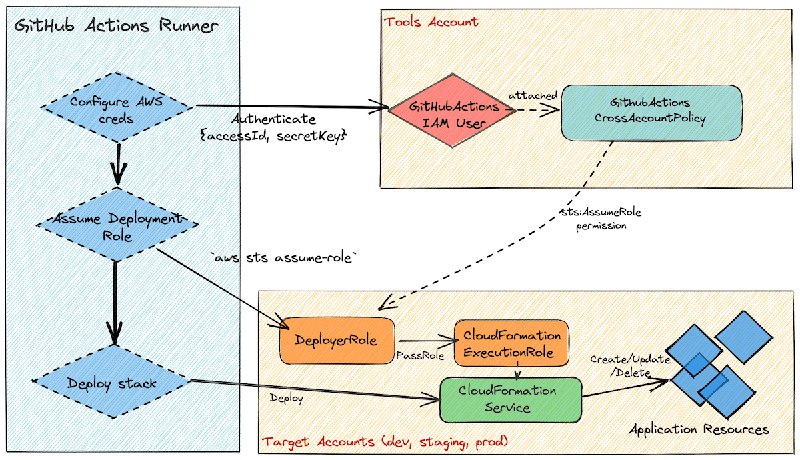
🔶 How to create IAM roles for deploying your AWS Serverless app

An in-depth guide to creating production-ready, least privilege IAM roles for deploying your serverless application across multiple AWS accounts.

https://serverlessfirst.com/create-iam-deployer-roles-serverless-app/

#aws
Serverless First How to create IAM roles for deploying your AWS Serverless app | Serverless First An in-depth guide to creating production-ready, least privilege IAM roles for deploying your serverless application across multiple AWS accounts.
Post #175 722
Post #172 700
🔶 Expanding Secrets Infrastructure to AWS Lambda

How Square extended their datacenter-based secrets infrastructure to enable a cloud migration supporting Lambda. They added SPIFFE compatibility to their secrets infrastructure and developed a Lambda secrets syncer that Square engineers can deploy via a Terraform module.

https://developer.squareup.com/blog/expanding-secrets-infrastructure-to-aws-lambda/

#aws
Square Corner Blog Expanding Secrets Infrastructure to AWS Lambda Extending our data center to the cloud
Post #169 689
Post #167 712
Post #166 783
🔶 S3 backups and other strategies for ensuring data durability through ransomware attacks

This post will discuss options for ensuring the durability of data stored on S3, through protections in place and backup strategies. The AWS backup service on AWS unfortunately does not backup S3 buckets and a lot of discussions of backups and data durability on AWS do not describe the implementation in sufficient detail, which allows a number of potential dangers. This post will show you the two best options (s3 object locks and replication policies), explains how to use these, and what to watch out for.

https://summitroute.com/blog/2021/08/03/S3_backups_and_other_strategies_for_ensuring_data_durability_through_ransomware_attacks/

#aws
Summitroute Summit Route - S3 backups and other strategies for ensuring data durability through ransomware attacks AWS Security Consulting
Post #165 734
🔶 So You Inherited an AWS Account. A 30-day security guide for engineers…

A guide to help you filter through the mess, isolate the changes you need to make, and start to tame your environment by Matt Fuller, founder of CloudSploit. He proposes: get stable access, stop using the root user, update billing info, enable CloudTrail logging and monitoring, clean up IAM entities, locate exposed services, lock down your domains, find expiring certificates, untangle the web of services, and monitor and migrate.

https://medium.com/swlh/so-you-inherited-an-aws-account-e5fe6550607d

#aws
Twitter Matt Fuller (@matthewdfuller) | Twitter The latest Tweets from Matt Fuller (@matthewdfuller). Founder of @CloudSploit, acq. by @AquaSecTeam. Former Infra / Sec / Manager @Adobe, @Aviary & @Mozilla intern, @RITtigers grad, @NYC resident, @NYRangers fan. New York, NY
Post #164 740
🔷 Cloud Guardrails

Tool by Lead Security Engineer of Salesforce, Kinnaird McQuade, that allows you to rapidly cherry-pick cloud security guardrails by generating Terraform files that create Azure Policy Initiatives (basically AWS SCPs but for Azure). Cherry-pick and bulk-select the security policies you want, enforce low-friction policies within minutes, and easily roll back policies that you don’t want. See Kinnaird’s great thread about it here.

https://github.com/salesforce/cloud-guardrails

#azure
Post #163 695
🔷 Network Isolated AKS - Part 1: Controlling network traffic

First part of a series on AKS (Azure Kubernetes Service) network isolation, elaborating how to protect AKS from a networking perspective. You can also reference the companion repository.

https://itnext.io/network-isolated-aks-part-1-controlling-network-traffic-2cd0e045352d

#azure
GitHub GitHub - geekzter/azure-aks: Network Isolated AKS Network Isolated AKS. Contribute to geekzter/azure-aks development by creating an account on GitHub.
Post #162 702
Older posts →
Threads Profile ViewerView any public Threads profile without an account.Open ThreadLook →Writing with AI? Make it sound human.Metric37 rewrites AI drafts so they read naturally. Free AI detector, 1,500 words free.Try Metric37 →