TGViewer
Channel Public Channel
CloudSec Wine

CloudSec Wine

@cloud_sec

All about cloud security

Contacts:
@AMark0f
@dvyakimov

About DevSecOps:
@sec_devops
Subscribers
2.27K
Photos
1.1K
Videos
0
Links
1.4K

Showing posts older than #1436 · Back to latest

Older Posts 17 shown
Post #1435 419
🤖 AI Threat Readiness Framework

Wiz proposes a 4-pillar AI Threat Readiness Framework: (1) reduce attack surface and AI-scan all exposures; (2) accelerate CVE patching and zero-day response; (3) perform deep AI-driven code analysis; (4) automate real-time threat detection and containment.

https://www.wiz.io/blog/ai-threat-readiness-framework

#AI
  • ❤ 1
  • 👍 1
  • 🔥 1
Post #1433 468
🤖 Skill Issues: How We Discovered Supply Chain Attack Vectors in an AI Agent Skills Marketplace

Orca Security identified four supply chain attack primitives in an AI agent skills marketplace: unauthenticated install count inflation, non-deterministic security scanning, silent skill name override, and blind bulk updates. All enabling bait-and-switch, nested skill injection, and delayed weaponization attacks achieving real-world RCE.

https://orca.security/resources/blog/ai-agent-skill-supply-chain-security

#AI
  • 👍 2
  • ❤ 1
  • 🔥 1
Post #1432 475
20 мая в 12:00 (мск) пройдёт бесплатный вебинар «Автоматизация процессов безопасности в Kubernetes: опыт MWS Cloud Platform». 

Руководитель направления облачной безопасности Алексей Федулаев расскажет: 
- Какие есть подводные камни при переходе с ручных сканов 
- Как покрыть тепловыми картами кластеры и отслеживать нарушения
- Как находить аномалии в поведении пользователей 
- И наконец, как это всё подружить с центром безопасности

Вебинар будет полезен директорам по ИТ и ИБ, ИБ-специалистам и инженерам, работающим в облачных средах. 

Регистрируйтесь, подключайтесь к прямому эфиру и задавайте вопросы в чате. 

📆 20 мая в 12:00

#advertising
  • ❤ 1
  • 👍 1
  • 🔥 1
  • 😱 1
Post #1431 432
🤖 The (In)security Landscape of AI-Powered GitHub Actions (Part 2/2)

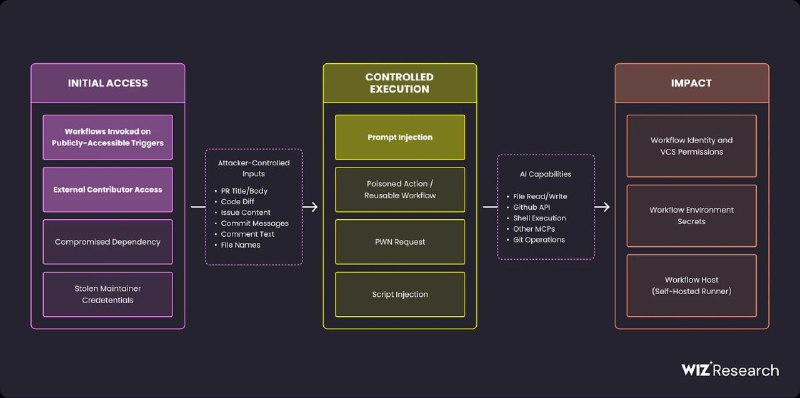
Wiz researchers analysed popular AI GitHub Actions (Anthropic, OpenAI, Google) and found: bot permission-check bypasses enabling untrusted external apps to trigger AI workflows, novel credential-file exfiltration vectors unrecognised by LLMs as sensitive, and widespread misconfigurations in repos with 200,000+ combined stars.

https://www.wiz.io/blog/github-actions-security-ai-powered-actions-vulnerabilities

#AI
  • ❤ 1
  • 👍 1
  • 🔥 1
Post #1430 991
🤖 LeakyLM: AI Assistants Are Leaking Your Conversations

Research disclosing that ChatGPT, Claude, Grok, and Perplexity embed third-party trackers (Meta, Google, TikTok) that leak conversation URLs, email hashes, and user identifiers, often bypassing cookie consent. via client-side pixels and server-side forwarding.

https://leakylm.github.io

#AI
  • ❤ 1
  • 👍 1
  • 🔥 1
Post #1429 454
🔶 The Danger of Multi-SSO AWS Cognito User Pools

This post explores security anti-patterns in multi-SSO AWS Cognito User Pools: ghost identity injection via misconfigured Lambda triggers, "triggerSource" blind spots, sub-splitting attacks on "event.userName", and IdP identifier hijacks. It also introduces "maSSO", a weaponized OIDC/SAML IdP for pentesting.

https://blog.doyensec.com/2026/05/05/cloudsectidbits-masso-cognito-sso.html

#aws
  • ❤ 1
  • 👍 1
  • 🔥 1
Post #1427 535
🤖 Building an AI Ready Vulnerability Management Program After NVD Changes and Claude Mythos

NVD's April 2026 scope reduction (enriching only KEVs and critical federal software) collides with AI-accelerated vulnerability discovery (e.g., Claude Mythos), creating a dangerous gap in OSS CVE coverage.

https://pulse.latio.tech/p/building-an-ai-ready-vulnerability

#AI
  • ❤ 1
  • 👍 1
  • 🔥 1
Post #1422 577
👨‍💻 GitHub RCE Vulnerability: CVE-2026-3854 Breakdown

Wiz Research discovered CVE-2026-3854 (CVSS 8.7): an unsanitized semicolon injection in GitHub's X-Stat internal header allows any authenticated user to override security fields via git push -o, achieving RCE on GitHub com and full GHES server compromise.

https://www.wiz.io/blog/github-rce-vulnerability-cve-2026-3854

#github
  • 👍 3
  • ❤ 1
  • 🔥 1
Post #1419 576
🌩 My Claude Code Setup (2026 Edition)

A walkthrough of my Claude Code setup across a multi-project monorepo: global settings, safety guardrails, a context/plan/code workflow, subagents and plugins, and the StarCraft-themed customisations that make the terminal feel like mine.

https://blog.marcolancini.it/2026/blog-my-claude-code-setup

#ClaudeCode
  • ❤ 2
  • 👍 2
  • 🔥 2
Post #1417 525
🤖 Orchestrating AI Code Review at scale

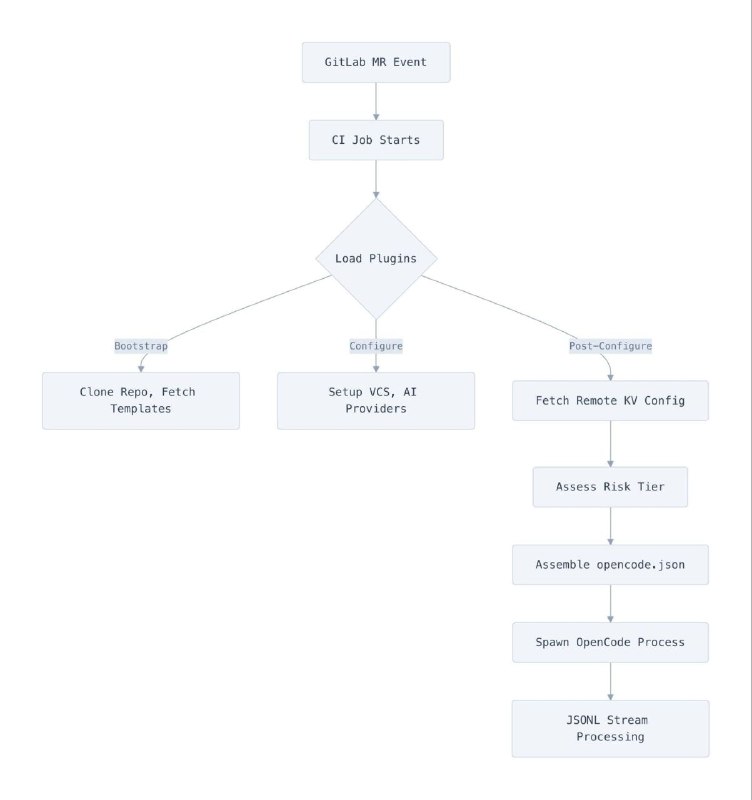
Cloudflare built a CI-native, plugin-based AI code review system using OpenCode, orchestrating up to 7 specialised agents (security, performance, code quality, etc.) per merge request. It processed 131K reviews across 48K MRs, averaging $0.98/review at 3m39s median latency, with an 85.7% prompt cache hit rate.

https://blog.cloudflare.com/ai-code-review

#AI
  • ❤ 1
  • 👍 1
  • 🔥 1
Post #1416 761
🤖 How Amazon uses agentic AI for vulnerability detection at global scale

Amazon's RuleForge is a multi-agent AI system that auto-generates CVE detection rules from exploit PoC code. It uses parallel generation (via Amazon Bedrock/Fargate), a separate judge model (reducing false positives by 67%), and multistage validation, achieving 336% faster rule production than manual workflows while keeping humans in the final approval loop.

https://www.amazon.science/blog/how-amazon-uses-agentic-ai-for-vulnerability-detection-at-global-scale

#AI
  • ❤ 2
  • 👍 2
  • 🔥 1
Older posts →
Threads Profile ViewerView any public Threads profile without an account.Open ThreadLook →Writing with AI? Make it sound human.Metric37 rewrites AI drafts so they read naturally. Free AI detector, 1,500 words free.Try Metric37 →