TGViewer
Channel Public Channel
CloudSec Wine

CloudSec Wine

@cloud_sec

All about cloud security

Contacts:
@AMark0f
@dvyakimov

About DevSecOps:
@sec_devops
Subscribers
2.28K
Photos
1.1K
Videos
0
Links
1.4K

Showing posts older than #1189 · Back to latest

Older Posts 19 shown
Post #1188 410
👩‍💻 Microsoft Entra ID OAuth Phishing and Detections

This article explores OAuth phishing and token-based abuse in Microsoft Entra ID. Through emulation and analysis of tokens, scope, and device behavior during sign-in activity, it surfaces high-fidelity signals defenders can use to detect and hunt for OAuth misuse.

https://www.elastic.co/security-labs/entra-id-oauth-phishing-detection

#azure
  • 🔥 2
  • ❤ 1
  • 👍 1
Post #1186 434
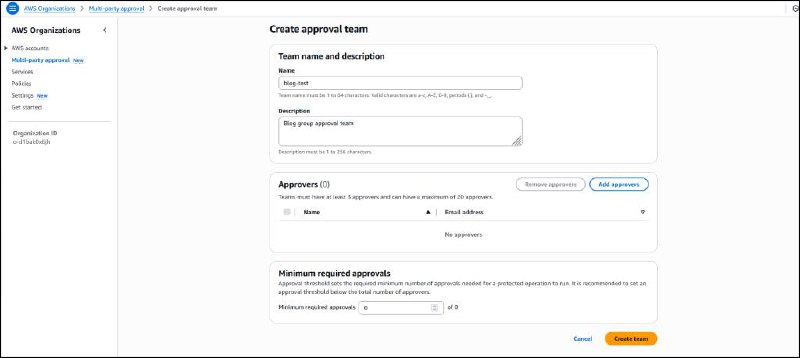
🔶 AWS Backup adds new Multi-party approval for logically air-gapped vaults

Multi-party approval for AWS Backup logically air-gapped vaults enables organizations to recover their backup data even when their AWS account is compromised, by creating approval teams of trusted individuals who can authorize vault sharing with a recovery account through a separate authentication path.

https://aws.amazon.com/ru/blogs/aws/aws-backup-adds-new-multi-party-approval-for-logically-air-gapped-vaults/

(Use VPN to open from Russia)

#aws
  • ❤ 1
  • 👍 1
  • 🔥 1
Post #1185 437
🔶 Amazon GuardDuty expands Extended Threat Detection coverage to Amazon EKS clusters

GuardDuty Extended Threat Detection introduces a new critical severity finding type, which automatically correlates security signals across Amazon EKS audit logs, runtime behaviors of processes associated with EKS clusters, malware execution in EKS clusters, and AWS API activity to identify sophisticated attack patterns that might otherwise go unnoticed.

https://aws.amazon.com/ru/blogs/aws/amazon-guardduty-expands-extended-threat-detection-coverage-to-amazon-eks-clusters/

(Use VPN to open from Russia)

#aws
  • ❤ 1
  • 👍 1
  • 🔥 1
Post #1182 487
🔶 How to use on-demand rotation for AWS KMS imported keys

AWS announced support for on-demand rotation of symmetric encryption AWS Key Management Service (AWS KMS) keys with imported key material (EXTERNAL origin). This new capability enables you to rotate the cryptographic key material of these keys without changing the key identifier.

https://aws.amazon.com/ru/blogs/security/how-to-use-on-demand-rotation-for-aws-kms-imported-keys/

(Use VPN to open from Russia)

#aws
  • ❤ 1
  • 👍 1
  • 🔥 1
Post #1181 470
🔶 Introducing AWS API models and publicly available resources for AWS API definitions

AWS now provides daily updates of Smithy API models on GitHub, enabling developers to build custom SDK clients, understand AWS API behaviors, and create developer tools for better AWS service integration.

https://aws.amazon.com/ru/blogs/aws/introducing-aws-api-models-and-publicly-available-resources-for-aws-api-definitions/

(Use VPN to open from Russia)

#aws
  • ❤ 1
  • 👍 1
  • 🔥 1
Post #1179 429
🔶 Roles Here? Roles There? Roles Anywhere: Exploring the Security of AWS IAM Roles Anywhere

This examination of the AWS Roles Anywhere service looks at potential risks, analyzed from both defender and attacker perspectives.

https://unit42.paloaltonetworks.com/aws-roles-anywhere/

#aws
  • ❤ 1
  • 👍 1
  • 🔥 1
Post #1177 422
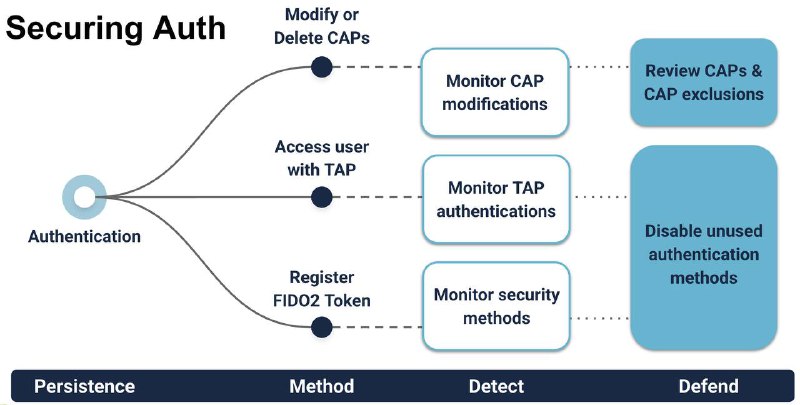
👩‍💻 Persisting Unseen: Defending against Entra ID persistence

Post covering some methods attackers may use now or in the near future to maintain access to Entra ID (formerly Azure AD) once they've obtained a privileged foothold.

https://kknowl.es/posts/defending-against-entra-id-persistence/

#azure
  • ❤ 1
  • 👍 1
  • 🔥 1
Post #1176 445
🔶 Implementing just-in-time privileged access to AWS with Microsoft Entra and AWS IAM Identity Center

By using security groups in Entra and mapping them to permission sets in IAM Identity Center, you can automate the provisioning and deprovisioning of privileged access based on defined policies and approval workflows.

https://aws.amazon.com/ru/blogs/security/implementing-just-in-time-privileged-access-to-aws-with-microsoft-entra-and-aws-iam-identity-center/

#aws
  • ❤ 1
  • 👍 1
  • 🔥 1
Post #1174 425
👩‍💻 Lost in Resolution: Azure OpenAI's DNS Resolution Issue

Unit 42 researchers discovered an issue with Azure OpenAI's Domain Name System (DNS) resolution logic that could have enabled cross-tenant data leaks and meddler-in-the-middle (MitM) attacks.

https://unit42.paloaltonetworks.com/azure-openai-dns-resolution/

#azure
  • ❤ 1
  • 👍 1
  • 🔥 1
Post #1173 482
🔶 CloudTrail Logging Evasion: Where Policy Size Matters

Permiso uncovered a subtle yet critical logging evasion vulnerability within AWS environments - mainly the differing size limitations of individual AWS CloudTrail logs versus the actual content being logged. By exploiting whitespace and other syntactic quirks, an attacker can create valid IAM policies that effectively bypass CloudTrail logging.

https://permiso.io/blog/cloudtrail-logging-evasion-where-policy-size-matters

#aws
  • ❤ 1
  • 👍 1
  • 🔥 1
Post #1172 452
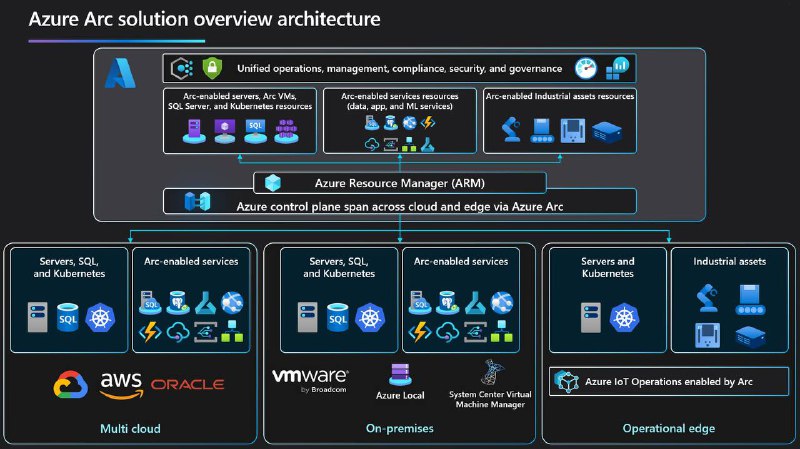
👩‍💻 Azure Arc - C2aaS

Post exploring Azure Arc's overlooked C2aaS potential: attacking and defending against its usage and exploring use cases for Red Teams.

https://blog.zsec.uk/azure-arc-c2aas/

#azure
  • ❤ 1
  • 👍 1
  • 🔥 1
Older posts →
Threads Profile ViewerView any public Threads profile without an account.Open ThreadLook →Writing with AI? Make it sound human.Metric37 rewrites AI drafts so they read naturally. Free AI detector, 1,500 words free.Try Metric37 →