TGViewer
CloudSec Wine CloudSec Wine @cloud_sec · 2.27K subscribers
Post #746 722
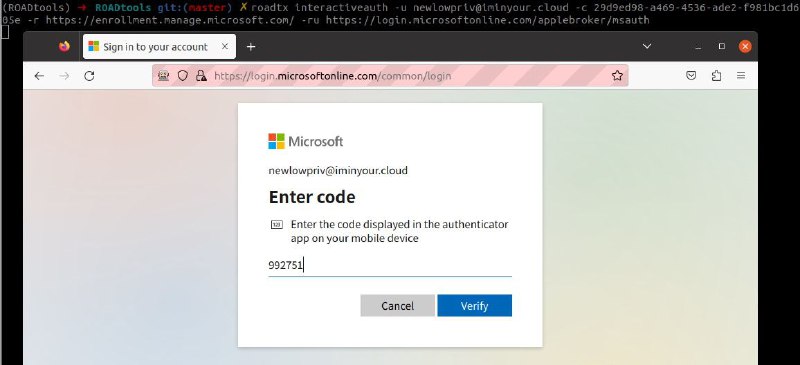
🔷 Phishing for Primary Refresh Tokens and Windows Hello keys

Post describing new techniques to phish for Primary Refresh Tokens, and in some scenarios also deploy passwordless credentials that comply with even the strictest MFA policies.

https://dirkjanm.io/phishing-for-microsoft-entra-primary-refresh-tokens/

#azure
  • 😱 4
  • 🔥 2
  • 👍 1
More from @cloud_sec
  1. Oct 7, 2026👩‍💻 Storm-3168: Agentic-driven cloud attacks using compromised service principals Storm-…
  2. Oct 6, 2026🤖 Securing the software factory at machine speed GitLab's CISO argues that agentic AI dev…
  3. Oct 5, 2026🤖 Throw Away the Playbook: Security in the AI-Native SDLC We, as an industry, should have…
  4. Oct 2, 2026🔴 Strengthen your CI/CD pipeline with new Secure Source Manager capabilities Google Cloud…
  5. Oct 1, 2026🔶 Exploring the new AWS Sign Up experience This post will explore what this new concept d…
  6. Sep 30, 2026🤖 Hacking OpenAI Researchers chained a libheif heap buffer overflow (via Discourse/ImageM…
Threads Profile ViewerView any public Threads profile without an account.Open ThreadLook →Writing with AI? Make it sound human.Metric37 rewrites AI drafts so they read naturally. Free AI detector, 1,500 words free.Try Metric37 →