TGViewer
CloudSec Wine CloudSec Wine @cloud_sec · 2.28K subscribers
Post #1023 549
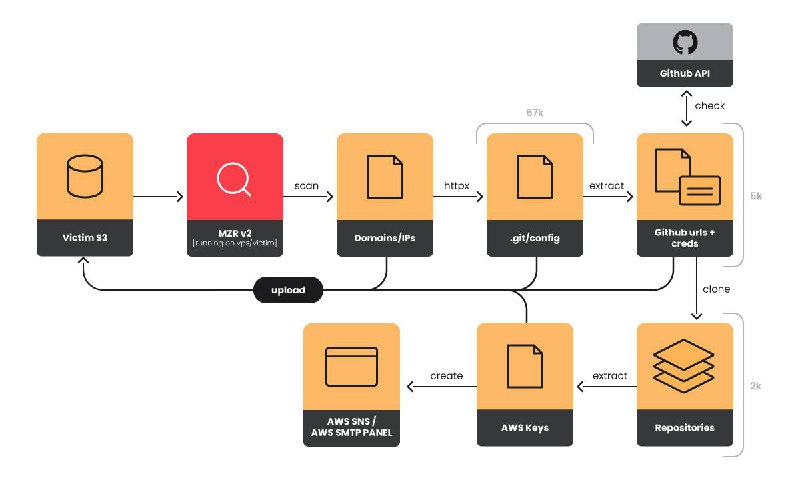
🔶 EMERALDWHALE: 15k Cloud Credentials Stolen in Operation Targeting Exposed Git Config Files

This campaign used multiple private tools that abused multiple misconfigured web services, allowing attackers to steal credentials, clone private repositories, and extract cloud credentials from their source code. Credentials for over 10,000 private repositories were collected during the operation.

https://sysdig.com/blog/emeraldwhale/

(Use VPN to open from Russia)

#aws
  • 🔥 4
  • ❤ 1
  • 👍 1
More from @cloud_sec
  1. Oct 2, 2026🔴 Strengthen your CI/CD pipeline with new Secure Source Manager capabilities Google Cloud…
  2. Oct 1, 2026🔶 Exploring the new AWS Sign Up experience This post will explore what this new concept d…
  3. Sep 30, 2026🤖 Hacking OpenAI Researchers chained a libheif heap buffer overflow (via Discourse/ImageM…
  4. Sep 29, 2026👩‍💻 How to secure edge AI in customer-owned environments Edge AI shifts trust responsibi…
  5. Sep 28, 2026🤖 Containers Are No Longer a Security Boundary AI-accelerated kernel vuln discovery (5,97…
  6. Sep 25, 2026🔶 Introducing Amazon EBS Volume Clones across AWS account AWS introduces Amazon EBS Volum…
Threads Profile ViewerView any public Threads profile without an account.Open ThreadLook →Writing with AI? Make it sound human.Metric37 rewrites AI drafts so they read naturally. Free AI detector, 1,500 words free.Try Metric37 →