TGViewer
Channel Public Channel
πŸ›‘ Cybersecurity & Privacy πŸ›‘ - News

πŸ›‘ Cybersecurity & Privacy πŸ›‘ - News

@cibsecurity

πŸ—ž The finest daily news on cybersecurity and privacy.

πŸ”” Daily releases.

πŸ’» Is your online life secure?

πŸ“© lalilolalo.dev@gmail.com
Subscribers
28.5K
Photos
0
Videos
0
Links
91.1K

Showing posts older than #90493 Β· Back to latest

Older Posts 20 shown
Post #90492 352
πŸ•΅οΈβ€β™‚οΈ China-Linked Hacker Shows AI Capabilities in APAC Attack πŸ•΅οΈβ€β™‚οΈ

In the first purported "nearautonomous" attack on a nationstate, a Chineselanguage operator used a complex AI framework to target and compromise government agencies, likely in Taiwan.

πŸ“– Read more.

πŸ”— Via "Dark Reading"

----------
πŸ‘οΈ Seen on @cibsecurity
Post #90491 416
πŸ“’ Why software supply chain security is the next accountability challenge for channel partners πŸ“’

Partners need to be able to confidently answer key client questions relating to supply chain security going forward...

πŸ“– Read more.

πŸ”— Via "ITPro"

----------
πŸ‘οΈ Seen on @cibsecurity
ChannelPro Why software supply chain security is the next accountability challenge for channel partners Partners need to be able to confidently answer key client questions relating to supply chain security going forward...
Post #90490 544
πŸ“” Wiz AI Agent Finds Critical Snowflake GitHub Repo Flaw Advanced Security Missed πŸ“”

The security flaw in Snowflakes GitHub Actions workflow had been missed by a GitHub Advanced Security scan, said a Wiz researcher.

πŸ“– Read more.

πŸ”— Via "Infosecurity Magazine"

----------
πŸ‘οΈ Seen on @cibsecurity
Infosecurity Magazine Wiz AI Agent Finds Critical Snowflake GitHub Repo Flaw The security flaw in Snowflake’s GitHub Actions workflow had been missed by a GitHub Advanced Security scan, said a Wiz researcher
Post #90489 495
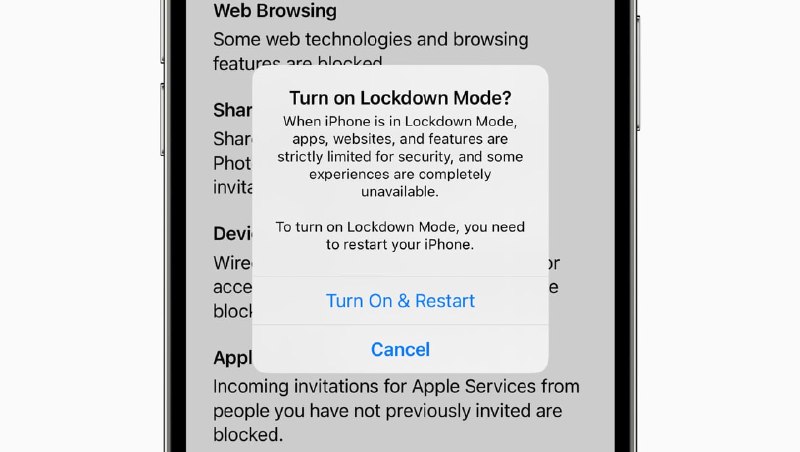
🦿 Apple Warns Users in 110 Countries of Mercenary Spyware as iPhone Alerts Get Harder to Miss 🦿

Apple sent a new wave of mercenary spyware threat notifications to targeted users in 110 countries, while making the warnings more visible on iPhones. The alerts signal suspected targeting, not confirmed compromise, and Apple is urging affected users to verify the warning, consider Lockdown Mode, and seek expert help. The post Apple Warns Users in 110 Countries of Mercenary Spyware as iPhone Alerts Get Harder to Miss appeared first on TechRepublic.

πŸ“– Read more.

πŸ”— Via "Tech Republic"

----------
πŸ‘οΈ Seen on @cibsecurity
TechRepublic Apple Warns Users in 110 Countries of Mercenary Spyware as iPhone Alerts Get Harder to Miss - TechRepublic Apple warns targeted users in 110 countries of mercenary spyware attacks as new iPhone alerts surface on the Lock Screen and in Settings.
Post #90488 427
πŸ“” Enterprise Applications Carry 4.31x More Critical and High Vulnerabilities πŸ“”

Enterprise software creation has accelerated as vulnerability levels rise, Sonatype finds.

πŸ“– Read more.

πŸ”— Via "Infosecurity Magazine"

----------
πŸ‘οΈ Seen on @cibsecurity
Infosecurity Magazine Enterprise Applications Carry 4.31x More Critical and High Vulnerabili Enterprise software creation has accelerated as vulnerability levels rise, Sonatype finds
Post #90487 454
πŸ“” NASA Ground Control Software Flaw Enables Unauthenticated Commands πŸ“”

Critical AITGUI flaws expose spacecraft commands and scripts to unauthenticated attackers.

πŸ“– Read more.

πŸ”— Via "Infosecurity Magazine"

----------
πŸ‘οΈ Seen on @cibsecurity
Infosecurity Magazine NASA Ground Control Software Flaw Enables Unauthenticated Commands Critical AIT-GUI flaws expose spacecraft commands and scripts to unauthenticated attackers
  • πŸ”₯ 1
Post #90486 395
πŸ–‹οΈ TWINLOOT Abuses SharePoint and Teams to Steal Credentials and Move Across Networks πŸ–‹οΈ

Cybersecurity researchers have disclosed details of a previously undocumented Python implant framework dubbed TWINLOOT. "TWINLOOT is a modular, PyArmorhardened Python implant designed to operate its entire commandandcontrol infrastructure inside trusted Microsoft services," Ontinue said in a technical report shared with The Hacker News. "Tasking flows through SharePoint Online file.

πŸ“– Read more.

πŸ”— Via "The Hacker News"

----------
πŸ‘οΈ Seen on @cibsecurity
Post #90485 356
πŸ–‹οΈ AI "Mind Viruses" Can Spread Between Agents Through Persistent Prompt Files πŸ–‹οΈ

Security researchers at Anthropic and Switzerland's EPFL have demonstrated that selfpropagating payloads can spread from one artificial intelligence AI agent to the next through the editable system prompt files that autonomous agent harnesses use to carry state between sessions. The work, released as a preprint on August 10, 2026, tests the technique in a simulated sixagent coding.

πŸ“– Read more.

πŸ”— Via "The Hacker News"

----------
πŸ‘οΈ Seen on @cibsecurity
Post #90484 305
πŸ•΅οΈβ€β™‚οΈ 'Ransom Busters': Ransomware Actor Poses as Incident-Recovery Service πŸ•΅οΈβ€β™‚οΈ

A ransomware affiliate appears to be sidling up to victims with offers of aid, masking its true intention of diverting ransom payments.

πŸ“– Read more.

πŸ”— Via "Dark Reading"

----------
πŸ‘οΈ Seen on @cibsecurity
Dark Reading 'Ransom Busters': Ransomware Actor Poses as Recovery Service A ransomware affiliate appears to be sidling up to victims with offers of aid, masking its true intention of diverting ransom payments.
Post #90483 317
🦿 FBI Pegasus Records Expose a Blind Spot in US Spyware Oversight 🦿

Federal court records show how far the FBIs Pegasus review progressed and why new US spyware reporting will still leave major gaps in government hacking transparency. The post FBI Pegasus Records Expose a Blind Spot in US Spyware Oversight appeared first on TechRepublic.

πŸ“– Read more.

πŸ”— Via "Tech Republic"

----------
πŸ‘οΈ Seen on @cibsecurity
TechRepublic FBI Pegasus Records Expose a Blind Spot in US Spyware Oversight - TechRepublic FBI Pegasus records reveal gaps in new US spyware oversight, showing what future court wiretap statistics may still fail to capture.
Post #90482 322
🌊 AI SOC vs. SOAR: What the Architectural Difference Means for a Team Evaluating Both 🌊

AI SOC vs SOAR vs MDR explained by practitioners see how architecture decides breach outcomes. Discover which layer your team should run today. The post AI SOC vs. SOAR What the Architectural Difference Means for a Team Evaluating Both appeared first on UnderDefense.

πŸ“– Read more.

πŸ”— Via "UnderDefense"

----------
πŸ‘οΈ Seen on @cibsecurity
UnderDefense AI SOC vs SOAR: What Every Security Team Must Know AI SOC vs SOAR explained by practitioners: see how architecture decides breach outcomes. Discover which layer your team should run today.
Post #90481 289
πŸ“” Three-quarters of Ransomware Attacks Target Mid-Market Firms πŸ“”

Black Kite finds midmarket is the sweet spot for ransomware as manufacturers are most likely to be hit.

πŸ“– Read more.

πŸ”— Via "Infosecurity Magazine"

----------
πŸ‘οΈ Seen on @cibsecurity
Infosecurity Magazine Three-quarters of Ransomware Attacks Target Mid-Market Firms Black Kite finds mid-market is the sweet spot for ransomware as manufacturers are most likely to be hit
Post #90480 263
πŸ“” Cyber Incident Disrupts Student Services at UT San Antonio πŸ“”

UT San Antonio has taken IT systems offline following a cyber incident, disrupting student registration and tuition payments days before term is due to resume.

πŸ“– Read more.

πŸ”— Via "Infosecurity Magazine"

----------
πŸ‘οΈ Seen on @cibsecurity
Post #90479 299
πŸ–‹οΈ CISA Flags Actively Exploited Ray Flaw That Can Trigger Browser-Based RCE πŸ–‹οΈ

The U.S. Cybersecurity and Infrastructure Security Agency CISA on Monday added a critical flaw impacting Ray to its Known Exploited Vulnerabilities KEV catalog, citing evidence of active exploitation. Ray is an opensource, Pythonnative distributed computing framework designed to scale artificial intelligence and machine learning workloads. As of writing, the GitHub project has more than.

πŸ“– Read more.

πŸ”— Via "The Hacker News"

----------
πŸ‘οΈ Seen on @cibsecurity
Post #90478 244
πŸ–‹οΈ SafePal Hardware Wallet Maker Says Flaw Exposed Data of Nearly 40,000 Customers πŸ–‹οΈ

SafePal has disclosed that an authorization flaw in an ordertracking plugin exposed the names, email addresses, shipping addresses, phone numbers, and purchase details of approximately 39,798 customers. The hardware wallet maker said all affected customers were notified individually by email on August 16 from securitysafepal.com, with the subject line "Important Your SafePal Order.

πŸ“– Read more.

πŸ”— Via "The Hacker News"

----------
πŸ‘οΈ Seen on @cibsecurity
Post #90477 232
πŸ–‹οΈ One Attacker Has Scraped Both Salesforce and ServiceNow Portals Since 2025 πŸ–‹οΈ

A single piece of infrastructure has been pulling records out of Salesforce and ServiceNow customer portals across multiple industries for more than a year, according to research published this week by agent security platform Reco. The activity, which Reco has named the City Forum campaign after a domain tied to the attacker's IP address, traces back to one server 158.220.87.79, hosted on a.

πŸ“– Read more.

πŸ”— Via "The Hacker News"

----------
πŸ‘οΈ Seen on @cibsecurity
Post #90476 260
πŸ–‹οΈ 16 Typosquatted RubyGems Packages Steal Browser Credentials and Crypto Wallets πŸ–‹οΈ

Cybersecurity researchers have flagged a new typosquatting campaign targeting RubyGems users with a Windowsbased information stealer. OpenSourceMalware, which discovered the activity on August 15, 2026, is tracking the threat under the moniker StubMaker. The complete list of packages published as part of the campaign is below ubnuler ubnlder ri18nr reaker rakier orakw joxn.

πŸ“– Read more.

πŸ”— Via "The Hacker News"

----------
πŸ‘οΈ Seen on @cibsecurity
Post #90475 344
πŸ“’ Hacker claims to have stolen millions of Azure customer records from McDonald’s, Vodafone, Kyndryl, and others – here's what we know so far πŸ“’

TheHatman claims the data has been stolen from the victims' Azure and Entra tenants using compromised credentials.

πŸ“– Read more.

πŸ”— Via "ITPro"

----------
πŸ‘οΈ Seen on @cibsecurity
IT Pro Hacker claims to have stolen millions of Azure customer records from McDonald’s, Vodafone, Kyndryl, and others – here's what we… TheHatman claims the data has been stolen from the victims' Azure and Entra tenants using compromised credentials
Post #90474 432
πŸ“” UK Legal Regulator Raises AI Misuse Concerns πŸ“”

Solicitors Regulation Authority sounds the alarm over AI hallucinations and data leaks.

πŸ“– Read more.

πŸ”— Via "Infosecurity Magazine"

----------
πŸ‘οΈ Seen on @cibsecurity
Post #90473 463
πŸͺ– Stronger Cybersecurity Programs Start with People: NIST Wants Your Input on the Path Forward for Human-Centered Cybersecurity πŸͺ–

When was the last time a cybersecurity process at work made you want to scream? Maybe it was a password requirement so complicated you had to write it down defeating the purpose, a phishing simulation test that felt more like a trap than a lesson, or a confusing security warning popup that interrupted your work. Or maybe youre on the other side of the equation, working as a cybersecurity professional who is wrangling a half dozen disconnected dashboards, drowning in alerts all flagged "urgent", or struggling to make a sound judgment call at midnight because youre tired and your tools.

πŸ“– Read more.

πŸ”— Via "NIST"

----------
πŸ‘οΈ Seen on @cibsecurity
NIST Stronger Cybersecurity Programs Start with People: NIST Wants Your Input on the Path Forward for Human-Centered Cybersecurity Credit: Shutterstock
Older posts β†’
Threads Profile ViewerView any public Threads profile without an account.Open ThreadLook β†’Writing with AI? Make it sound human.Metric37 rewrites AI drafts so they read naturally. Free AI detector, 1,500 words free.Try Metric37 β†’