TGViewer
Channel Public Channel
πŸ›‘ Cybersecurity & Privacy πŸ›‘ - News

πŸ›‘ Cybersecurity & Privacy πŸ›‘ - News

@cibsecurity

πŸ—ž The finest daily news on cybersecurity and privacy.

πŸ”” Daily releases.

πŸ’» Is your online life secure?

πŸ“© lalilolalo.dev@gmail.com
Subscribers
28.5K
Photos
0
Videos
0
Links
91.2K

Showing posts older than #90473 Β· Back to latest

Older Posts 20 shown
Post #90472 367
πŸ¦… Brand Impersonation Takedown: From Whack-a-Mole to Managed Response πŸ¦…

Manual brand impersonation takedowns fail because attackers move faster than ticketbased abuse reports can resolve phishing pages and fake executive profiles often do their damage within hours of going live, while manual removal can take days. A managed takedown program pairs continuous, verified monitoring with preauthorized removal incertain cases, cutting the exposure window from days to hours. This matters most for consulting and professional services firms, where a spoofed domain or fake executive profile can compromise the client trust the business is built on. How UNC3753 targeted US professional services firms in 2026 Between January and May of 2026, Google's Mandiant threat intelligence team tracked a financially motivated extortion campaign attributed to a group known ...

πŸ“– Read more.

πŸ”— Via "CYBLE"

----------
πŸ‘οΈ Seen on @cibsecurity
Cyble Brand Impersonation Takedown: From Whack-a-Mole to Managed Response Manual phishing and brand impersonation takedowns can't keep pace with attackers. See why consulting firms need managed, continuous takedown response.
Post #90471 275
🌊 10 Best AI SOC With 24/7 Human Analyst Backup: What Hybrid Coverage Actually Includes and Costs in 2026 🌊

Compare the 10 best AI SOC platforms with 247 human analyst support. See hybrid coverage, response speed, and real costs for 2026. Evaluate now. The post 10 Best AI SOC With 247 Human Analyst Backup What Hybrid Coverage Actually Includes and Costs in 2026 appeared first on UnderDefense.

πŸ“– Read more.

πŸ”— Via "UnderDefense"

----------
πŸ‘οΈ Seen on @cibsecurity
UnderDefense 10 Best AI SOC With 24/7 Human Analyst Backup: What Hybrid Coverage Actually Includes and Costs in 2026 Compare the 10 best AI SOC platforms with 24/7 human analyst support. See hybrid coverage, response speed, and real costs for 2026. Evaluate now.
Post #90470 220
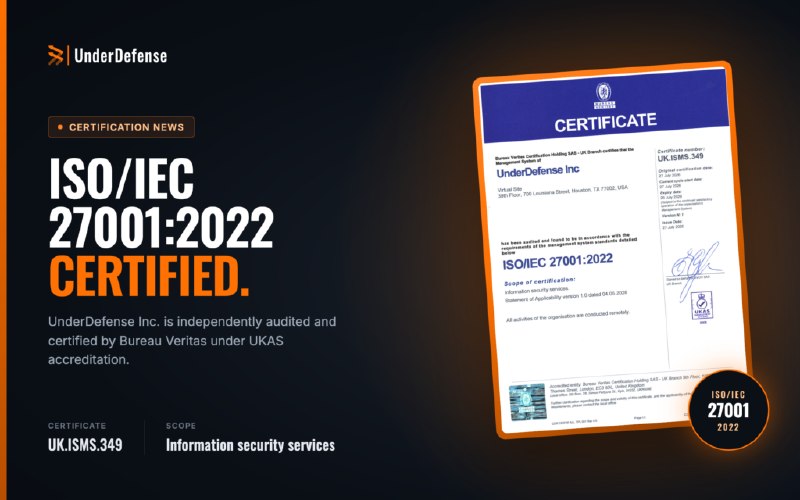
🌊 UnderDefense Inc. Achieves ISO/IEC 27001:2022 Certification 🌊

Certification scope expanded to cover the full product suite. SOC 2 Type II examination is underway. UnderDefense Inc. has received ISOIEC 270012022 certification, verified by an accredited external certification body. The certificate confirms that our information security management system meets the requirements of the international standard across the full scope of UnderDefense operations. This audit The post UnderDefense Inc. Achieves ISOIEC 270012022 Certification appeared first on UnderDefense.

πŸ“– Read more.

πŸ”— Via "UnderDefense"

----------
πŸ‘οΈ Seen on @cibsecurity
UnderDefense UnderDefense Achieves ISO/IEC 27001:2022 Certification UnderDefense Inc. is ISO/IEC 27001:2022 certified. Scope covers the full product suite. SOC 2 Type II underway. Certificate: trust.underdefense.com
Post #90469 193
🌊 Drata Pricing Guide 2026: Honest Cost Breakdown 🌊

Drata pricing decoded for CTOs percentile benchmarks, addon creep and the security budget lines a GRC platform never covers. The post Drata Pricing Guide 2026 Honest Cost Breakdown appeared first on UnderDefense.

πŸ“– Read more.

πŸ”— Via "UnderDefense"

----------
πŸ‘οΈ Seen on @cibsecurity
UnderDefense Drata Pricing Guide 2026: Honest Cost Breakdown Drata pricing decoded for CTOs: percentile benchmarks, add-on creep and the security budget lines a GRC platform never covers.
Post #90468 190
πŸ“” Infostealers Harvest 1.7 Billion Credentials in Six Months πŸ“”

Flashpoint data reveals infostealers were responsible for taking 1.7 billion credentials in the first half of 2026.

πŸ“– Read more.

πŸ”— Via "Infosecurity Magazine"

----------
πŸ‘οΈ Seen on @cibsecurity
Post #90466 170
πŸ“” ETSI Proposes 17 Cybersecurity Standards to Support Cyber Resilience Act πŸ“”

The European Telecommunications Standards Institute has launched an approval process for standards vendors will have to meet under the Cyber Resilience Act.

πŸ“– Read more.

πŸ”— Via "Infosecurity Magazine"

----------
πŸ‘οΈ Seen on @cibsecurity
Infosecurity Magazine ETSI Proposes 17 Cybersecurity Standards to Support EU CRA The European Telecommunications Standards Institute has launched an approval process for standards vendors will have to meet under the Cyber Resilience Act
Post #90464 140
πŸ“” UNISOC Modem Flaw Enables Remote Code Execution via Video Calls πŸ“”

UNISOC modem flaw enabled kernellevel code execution through video calls.

πŸ“– Read more.

πŸ”— Via "Infosecurity Magazine"

----------
πŸ‘οΈ Seen on @cibsecurity
Post #90463 176
πŸ–‹οΈ Suspected China-Nexus Actor Exploits VMware vCenter Flaw, Deploys Babuk-Derived Ransomware πŸ–‹οΈ

Cybersecurity researchers have attributed the exploitation of a newly patched security flaw in Broadcom VMware vCenter to a suspected Chinanexus advanced persistent threat APT. The attacks involve the exploitation of CVE202659310 CVSS score 9.8, a severe directorytraversal vulnerability in the VMware vCenter server that could be weaponized by a malicious actor to execute arbitrary code.

πŸ“– Read more.

πŸ”— Via "The Hacker News"

----------
πŸ‘οΈ Seen on @cibsecurity
Post #90462 189
πŸ–‹οΈ Evooo1Bot Linux Botnet Exploits Known Flaws to Turn Edge Devices Into SOCKS5 Proxies πŸ–‹οΈ

Cybersecurity researchers have flagged a previously undocumented Linux botnet family dubbed Evooo1Bot that derives its core functionality from the Mirai botnet source code and is equipped to turn internetfacing devices into SOCKS proxies. "While the malware reuses the DDoS engine from the publicly leaked Mirai source code, it extends the original framework with numerous capabilities, including.

πŸ“– Read more.

πŸ”— Via "The Hacker News"

----------
πŸ‘οΈ Seen on @cibsecurity
Post #90461 313
πŸ–‹οΈ Unisoc VoLTE Video Call Exploit Chain Can Give Attackers Full Android Kernel Access πŸ–‹οΈ

Security researchers at SSD Secure Disclosure have published a twostage exploit chain that achieves full Android kernel access on devices running Unisoc modem firmware through a VoLTE video call, with no fix from the chipset maker. The advisory, published August 17, 2026, is the second stage of a chain that began in March 2026, when SSD disclosed remote code execution in the.

πŸ“– Read more.

πŸ”— Via "The Hacker News"

----------
πŸ‘οΈ Seen on @cibsecurity
Post #90460 270
πŸ–‹οΈ How MCP Servers Can Expose Enterprise Secrets πŸ–‹οΈ

MCP servers can expose enterprise secrets through plaintext configuration files, overpermissioned access and prompt injection, often before security teams even know the server is running. As more organizations adopt AI agents into their systems, that exposure can silently become a major gap in MCP server security. The Model Context Protocol MCP allows AI agents to reach the tools and data,.

πŸ“– Read more.

πŸ”— Via "The Hacker News"

----------
πŸ‘οΈ Seen on @cibsecurity
Post #90459 171
πŸ–‹οΈ ⚑ Weekly Recap: VMware Exploits, Windows 0-Day, MCP Attacks, Browser Hijacks and More πŸ–‹οΈ

The expensive attacks are not always the clever ones. This week had plenty of proof. Exposed services got hit, old bugs found fresh use, browser sessions became attack paths, and supplychain problems kept spreading farther than the original compromise. A lot of it came down to access that was already there and defenses that assumed nobody would look too closely. So, nothing magical. Just a.

πŸ“– Read more.

πŸ”— Via "The Hacker News"

----------
πŸ‘οΈ Seen on @cibsecurity
Post #90458 206
πŸ–‹οΈ Cavern C2 Uses DNS and Google Apps Script to Blend Into Legitimate Traffic πŸ–‹οΈ

Cybersecurity researchers have traced the continued evolution of the Cavern aka Cav3rn commandandcontrol C2 framework used by Iranian nationstate hackers in attacks targeting entities in Israel. Russian cybersecurity company Kaspersky said its ongoing monitoring of the threat activity cluster since December 2025 has led to the discovery of previously unreported components that expand the.

πŸ“– Read more.

πŸ”— Via "The Hacker News"

----------
πŸ‘οΈ Seen on @cibsecurity
Post #90457 218
πŸ–‹οΈ Forminator WordPress Flaw Can Enable Unauthenticated RCE via Malicious PHP Uploads πŸ–‹οΈ

A critical security flaw has been disclosed in Forminator Forms, a WordPress plugin with more than 600,000 active installations, that could be exploited to achieve arbitrary code execution on susceptible sites. The vulnerability, tracked as CVE202615748, is rated 9.8 out of 10.0 on the CVSS scoring system. It was discovered and reported by a security researcher who goes by the online alias ".

πŸ“– Read more.

πŸ”— Via "The Hacker News"

----------
πŸ‘οΈ Seen on @cibsecurity
Post #90456 295
πŸ–‹οΈ Snowflake GitHub Actions Flaw Lets Crafted Issues Trigger Command Injection πŸ–‹οΈ

Cybersecurity researchers at Wiz have disclosed a new GitHub Actions workflow injection vulnerability in Snowflake's public snowflakedbsnowflakeconnectornet repository that it said could be exploited through a crafted GitHub issue to execute commands in a workflow containing internal Jira credentials. The issue was present in .githubworkflowsjiraissue.yml, which ran when a.

πŸ“– Read more.

πŸ”— Via "The Hacker News"

----------
πŸ‘οΈ Seen on @cibsecurity
Post #90455 193
πŸ–‹οΈ Critical GitLab GraphQL Flaw Could Let Unauthenticated Attackers Delete Public Projects πŸ–‹οΈ

GitLab has released security updates to address a critical vulnerability impacting its Community Edition CE and Enterprise Edition EE software that, under certain conditions, could allow an unauthenticated attacker to remotely modify or delete public projects and user data. The flaw, tracked as CVE202619478, has been rated Critical by GitLab and assigned a CVSS score of 9.4. Released on.

πŸ“– Read more.

πŸ”— Via "The Hacker News"

----------
πŸ‘οΈ Seen on @cibsecurity
Post #90454 174
🦿 Nearly 700,000 French Taxpayer Records Reportedly Stolen in Government Cyberattack 🦿

Frances tax authority confirmed a cyberattack exposed taxpayer data as officials investigate the breachs scope and an unverified 678,000record claim. The post Nearly 700,000 French Taxpayer Records Reportedly Stolen in Government Cyberattack appeared first on TechRepublic.

πŸ“– Read more.

πŸ”— Via "Tech Republic"

----------
πŸ‘οΈ Seen on @cibsecurity
TechRepublic French Tax Authority Breach Exposes Sensitive Taxpayer Data France’s tax authority confirmed a cyberattack exposed taxpayer data as officials investigate the breach’s scope and an unverified 678,000-record claim.
  • ❀ 2
Post #90453 184
🦿 Apple Mac Malware Lets Attackers Control Browser Sessions After Infection 🦿

AmnesiaStealer malware targets macOS with data theft and remote browsersession control, potentially exposing accounts already open on compromised Macs. The post Apple Mac Malware Lets Attackers Control Browser Sessions After Infection appeared first on TechRepublic.

πŸ“– Read more.

πŸ”— Via "Tech Republic"

----------
πŸ‘οΈ Seen on @cibsecurity
TechRepublic Mac Malware Can Control Active Browser Sessions AmnesiaStealer malware targets macOS with data theft and remote browser-session control, potentially exposing accounts already open on compromised Macs.
Older posts β†’
Threads Profile ViewerView any public Threads profile without an account.Open ThreadLook β†’Writing with AI? Make it sound human.Metric37 rewrites AI drafts so they read naturally. Free AI detector, 1,500 words free.Try Metric37 β†’