TGViewer
Channel Public Channel
APT

APT

@apt_notes

This channel discusses:

— Offensive Security
— RedTeam
— Malware Research
— OSINT
— etc

Disclaimer:
t.me/APT_Notes/6

Chat Link:
t.me/APT_Notes_PublicChat
Subscribers
16.7K
Photos
565
Videos
28
Links
909

Showing posts older than #810 · Back to latest

Older Posts 20 shown
Post #809 2.96K
⚙️ Hackers No Hashing: Randomizing API Hashes to Evade Cobalt Strike Shellcode Detection

If you utilise API hashing in your malware or offensive security tooling. Try rotating your API hashes. This can have a significant impact on detection rates and improve your chances of remaining undetected by AV/EDR.

Blog:
https://www.huntress.com/blog/hackers-no-hashing-randomizing-api-hashes-to-evade-cobalt-strike-shellcode-detection

Source:
https://github.com/matthewB-huntress/APIHashReplace

#maldev #evasion #hinvoke #cobaltstrike #redteam
  • 🔥 7
  • 👍 3
Post #808 2.67K
🎭 Masky

Masky is a python library providing an alternative way to remotely dump domain users' credentials thanks to an ADCS. A command line tool has been built on top of this library in order to easily gather PFX, NT hashes and TGT on a larger scope.

This tool does not exploit any new vulnerability and does not work by dumping the LSASS process memory. Indeed, it only takes advantage of legitimate Windows and Active Directory features (token impersonation, certificate authentication via kerberos & NT hashes retrieval via PKINIT).

Blog:
https://z4ksec.github.io/posts/masky-release-v0.0.3/

Source:
https://github.com/Z4kSec/Masky

#ad #adcs #lsass #redteam
  • 👍 7
Post #807 2.5K
🤖 BBOT: OSINT automation for hackers

This tools is capable of executing the entire OSINT process in a single command, including subdomain enumeration, port scanning, web screenshots (with its gowitness module), vulnerability scanning (with nuclei), and much more. BBOT currently has over 50 modules and counting.

Features:
— Recursive;
— Graphing;
— Modular;
— Multi-Target;
— Automatic Dependencies;
— Smart Dictionary Attacks;
— Scope Distance;
— Easily Configurable via YAML.

Blog:
https://blog.blacklanternsecurity.com/p/bbot

Source:
https://github.com/blacklanternsecurity/bbot

#external #recon #osint #redteam #bugbounty
  • 👍 9
  • 🔥 2
Post #804 2.08K
APT EDRSandBlast EDRSandBlast is a tool written in C that weaponize a vulnerable signed driver to bypass EDR detections (Kernel callbacks and ETW TI provider) and LSASS protections. Multiple userland unhooking techniques are also implemented to evade userland…
😈 EDRSandBlast: Update

— User-mode (API hooking) evasion;
— Kernel-mode (callbacks and ETW ThreatIntel events) evasion;
— Successively tested on market-leading EDR products.

https://github.com/wavestone-cdt/EDRSandblast/tree/DefCon30Release

#maldev #edr #lsass #evasion #redteam
GitHub GitHub - wavestone-cdt/EDRSandblast at DefCon30Release Contribute to wavestone-cdt/EDRSandblast development by creating an account on GitHub.
  • 👍 3
Post #803 1.69K

Forwarded from Пост Импакта

#api #params

> Ничего не могу найти на сайте, может ещё что-то посмотреть?

Иногда встречается сайт, на котором всего лишь несколько конечных точек. Казалось, все параметры были проверены на уязвимости, а в чек-листе отмечены любые возможные проверки на инъекции и логику.

Однако, бывают уязвимости, которые не видны с первого взгляда. Например (CAPEC-460) HTTP Parameter Pollution или (CWE-472) External Control of Assumed-Immutable Web Parameter. Данные ошибки возникают из-за неожиданного поведения в функциях обработки параметров.

Давайте рассмотрим первую атаку HTTP Parameter Pollution, она состоит из возможности добавления повторяющихся параметров с помощью специальных разделителей запроса.

Например, у нас открыт сайт по продаже арбузов в браузере

🌐 example.com/profile.jsp?client_id=1

Для кнопки "Открыть профиль" устанавливается динамически в ответе от сервера html:

<a href="profile.jsp?client_id=1&action=view

А теперь изменим запрос добавив в него параметр и закодировав разделитель & как %26:

🌐 example.com/profile.jsp?client_id=1%26action%3Ddelete

В результате для кнопки "Открыть профиль" задаётся html:

<a href="profile.jsp?client_id=1&action=delete&action=view

При нажатии на кнопку — профиль пользователя будет удалён. Для того чтобы заставить жертву удалить свой аккаунт, нам нужно отправить ей ссылку и подождать.

Это происходит, потому что Apache Tomcat 🐈 при анализе двух одинаковых параметров (action) берёт значение первого:

&action=delete&action=view

Вот так выглядит код на стороне сервера:

String client_id = request.getParameter("client_id");
GetMethod get = new GetMethod("https://example.com/profile");
get.setQueryString("client_id=" + client_id + "&action=" + action);
href_link=get.URL;

Разработчик должен был учесть такое поведение и проверить возможность внедрения параметра action в client_id

Вообще, приоритет и процесс обработки параметров можно взять из этой таблицы ниже:

Technology/HTTP backend        | Parsing Result    | Example         |
---------------------------------------------------------------------
ASP.NET/IIS | All occurrences | par1=val1,val2 |
ASP/IIS | All occurrences | par1=val1,val2 |
PHP/Apache | Last occurrence | par1=val2 |
JSP Servlet/Apache Tomcat | First occurrence | par1=val1 |
JSP Servlet/Oracle Application | First occurrence | par1=val1 |
IBM HTTP Server | First occurrence | par1=val1 |

Так, для Server: Apache Tomcat будет взято значение из первого совпадения action=delete
А для Server: Apache значение уже будет action=view — последний параметр

Но не все сервера используют приоритет порядка, так, например, ASP.NET/IIS конкатенирует значения. Поэтому в случаях, когда выполнению XSS мешает санитизация или WAF, можно составить следующий payload:

example.com/search?param=<audio/n="&param="src/onerror=alert()>

В результате на странице html будет <audio n="," src/onerror=alert()> и XSS успешно сработает 💣

Помимо приоритетов, нужно также вспомнить о разделителях для параметров. Существует не только привычный & (амперсанд) и , (запятая) но и ряд других символов, тут нужно обратиться к стандартам и поискать реализации. Если открыть (rfc6570) URI Template можно найти Path-Style Parameter

Обычный URL будет следующим:

example.com/users?role=admin&firstName=N

А теперь преобразуем его в вид Path-Style:

example.com/users;role=admin;firstName=N

Использование в качестве разделителя ; (точки с запятой) не повсеместно. Это приводит к различиям обработки во фреймворках и как следствие к уязвимостям, в частности, на микросервисных архитектурах:

• CVE-2021-23336 — Python библиотека urllib.parse.parse_qsl не игнорирует точку с запятой.

• ParseThru — Go библиотека net/url не игнорирует точку с запятой и выводит предупреждение http: URL query contains semicolon...

Следует помнить, что уязвимость HTTP Parameter Pollution может возникать не только в URL, но и в любой части POST/GET запроса, а также в теле JSON.

{"client_id":4, "client_id":17, "action":"delete"}
  • 👍 4
  • 🔥 4
Post #801 2.83K
⚙️ Determining AD domain name via NTLM Auth

If you have nmap (http-ntlm-info) unable to determine the FQND of an Active Directory domain via OWA, for example due to Citrix NetScaler or other SSO solutions, do it manually!

1) curl -Isk -X POST -H 'Authorization: NTLM TlRMTVNTUAABAAAAB4IIogAAAAAAAAAAAAAAAAAAAAAKANc6AAAADw==' -H 'Content-Length: 0' https://autodiscover.exmaple.com/ews

2) echo 'TlRMTVNTUAACAAAADAAMAD...' | python2 ./ntlmdecoder.py

One-Liner function for bashrc\zshrc\etc-rc:

ntlm_decode() { curl -Isk -X POST -H 'Authorization: NTLM TlRMTVNTUAABAAAAB4IIogAAAAAAAAAAAAAAAAAAAAAKANc6AAAADw==' -H 'Content-Length: 0' "$1" | awk -F 'NTLM ' '/WWW-Authenticate: NTLM/ {print $2}' | python2 "$(locate ntlmdecoder.py)"; }

Source:
ntlmdecoder.py

#ntlm #auth #sso #tricks #pentest
  • 👍 8
  • 🔥 5
  • 👎 1
Post #800 1.85K
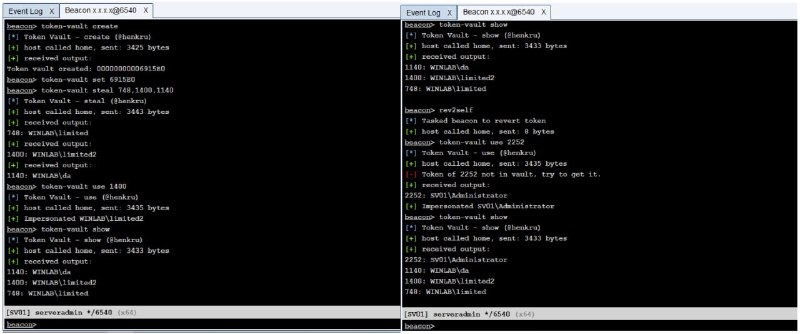
🔑 Cobalt Strike Token Vault

This Beacon Object File (BOF) creates in-memory storage for stolen/duplicated Windows access tokens allow you to:

— Hot swap/re-use already stolen tokens without re-duplicating;
— Store tokens for later use in case of a person log out.

https://github.com/Henkru/cs-token-vault

#ad #tokens #c2 #cobalt #redteam
  • 👍 5
  • ❤‍🔥 1
Post #799 2.09K
💉ClipboardInject

Abusing the clipboard to inject code into remote processes

This PoC uses the clipboard to copy a payload into a remote process, eliminating the need for VirtualAllocEx/WriteProcessMemory

https://www.x86matthew.com/view_post?id=clipboard_inject

#maldev #injection #clipboard #redteam
  • 👍 9
Post #798 2.27K
🦮 BlueHound

It is an open-source tool that helps blue teams pinpoint the security issues that actually matter. By combining information about user permissions, network access and unpatched vulnerabilities, BlueHound reveals the paths attackers would take if they were inside your network
It is a fork of NeoDash, reimagined, to make it suitable for defensive security purposes.

Blog:
🔗 https://zeronetworks.com/blog/bluehound-community-driven-resilience/

Tool:
🔗 https://github.com/zeronetworks/BlueHound

#ad #sharphound #blueteam
  • 👍 5
Post #796 2.14K
🛡 On Detection: Tactical to Functional

The goal of this series is to facilitate a conversation about the more technical aspects of attacks and how a deeper understanding at the more foundational levels helps to provide a batter base to build assumptions from.

🔗 Part 1: Discovering API Function Usage through Source Code Review
🔗 Part 2: Operations
🔗 Part 3: Expanding the Function Call Graph

#maldev #pinvoke #winapi #detection #blueteam #ttp
Medium On Detection: Tactical to Functional Part 1: Discovering API Function Usage through Source Code Review
  • 👍 3
Post #795 1.89K
Post #792 2.08K
🐚 PSAsyncShell: Asynchronous Firewall Bypass

PSAsyncShell is an Asynchronous TCP Reverse Shell written in pure PowerShell.

Unlike other reverse shells, all the communication and execution flow is done asynchronously, allowing to bypass some firewalls and some countermeasures against this kind of remote connections.

🔗 Research:
https://darkbyte.net/psasyncshell-bypasseando-firewalls-con-una-shell-tcp-asincrona/

🔗 Source:
https://github.com/JoelGMSec/PSAsyncShell

#ad #powershell #reverse #shell
  • 🔥 4
Post #790 2.15K
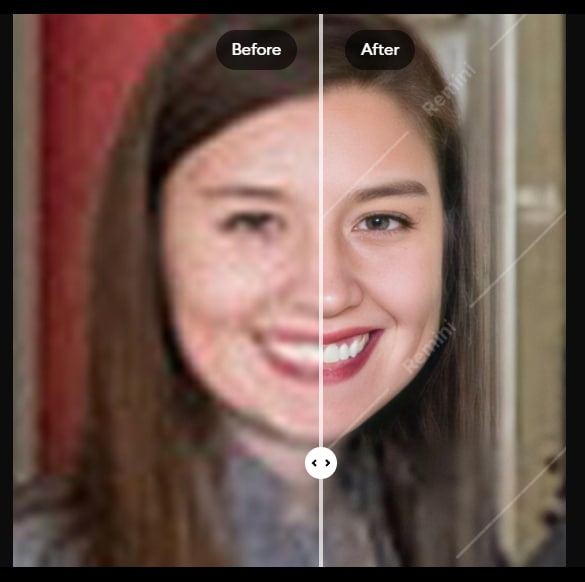
🔍 OSINT Tools

Today I'm going to talk about two excellent resources for photo editing during OSINT/IMINT.

Remini:
The image unblurring/sharpening tool could help yield better reverse image search and facial recognition result.
https://app.remini.ai/

Cleanup.Pictures:
One of the best online photo object removal tools I've ever seen.
https://cleanup.pictures/


#OSINT #IMINT #ImageAnalysis #tools
  • 👍 9
Post #789 2.39K
💉 Apache Spark RCE (CVE-2022-33891)

Apache Spark could allow an attacker to execute arbitrary commands on the system, caused by improper input validation of code path in HttpSecurityFilter when ACSs are enabled. This affects Apache Spark versions 3.0.3 and earlier, versions 3.1.1 to 3.1.2, and versions 3.2.0 to 3.2.1.

PoC (Sleep 10):
http://localhost:8080/?doAs=`echo%20%22c2xlZXAgMTAK%22%20|%20base64%20-d%20|%20bash`

Exploits:
https://github.com/HuskyHacks/cve-2022-33891
https://github.com/W01fh4cker/cve-2022-33891
https://github.com/west-wind/CVE-2022-33891

Shodan Dorks:
http.favicon.hash:856048515

#apache #spark #rce #cve
  • 👍 11
Post #788 2.03K
🔓 Unprotect

A project that is meant to provide Malware Analysts and Defenders with actionable insights and detection capabilities to shorten their response times. A catalog of over 200 tricks used by malware to bypass detection and protection tools. There are also rules for detecting these tricks.

https://unprotect.it/

#maldev #evasion #redteam #blueteam
  • 👍 3
  • 🔥 2
Older posts →
Threads Profile ViewerView any public Threads profile without an account.Open ThreadLook →Writing with AI? Make it sound human.Metric37 rewrites AI drafts so they read naturally. Free AI detector, 1,500 words free.Try Metric37 →