TGViewer
Channel Public Channel
APT

APT

@apt_notes

This channel discusses:

— Offensive Security
— RedTeam
— Malware Research
— OSINT
— etc

Disclaimer:
t.me/APT_Notes/6

Chat Link:
t.me/APT_Notes_PublicChat
Subscribers
16.7K
Photos
565
Videos
28
Links
909

Showing posts older than #788 · Back to latest

Older Posts 19 shown
Post #786 2K
👨‍👩‍👦 Book Can Save A Life

I will be very happy if this book helps at least one person to gain knowledge and learn the science of cybersecurity. The book is mostly practice oriented. This book is dedicated to my wife, Laura, and my children, Yerzhan and Munira. Also, thanks to everyone who is helping me through these difficult times. The proceeds from the sale of this book will be used to treat Munira, who is currently battling for her life at a hospital in Istanbul, Turkey.

The book is divided into three logical chapters:

— Malware development tricks and techniques;
— AV evasion tricks;
— Persistence techniques.

This book costs $16 but you can pay as much as you want. All money will go to the treatment of her daughter.

https://cocomelonc.github.io/book/2022/07/16/mybook.html

Channel author's preface:
Dear cocomelonc (
@abuyerzh) I wish you and your daughter health and well-being!
  • ❤ 24
  • 👍 3
Post #783 1.47K

Forwarded from Caster (necreas1ng)

Моя статья по пост-эксплуатации взломанного оборудования Cisco вышла в свет.

https://habr.com/ru/post/676942/

ᛝ
  • 👍 4
  • 🔥 1
Post #782 1.99K
Post #781 1.95K
🧦 Chisel Strike

A .NET XOR encrypted cobalt strike aggressor implementation for chisel to utilize faster proxy and advanced socks5 capabilities.

https://github.com/m3rcer/Chisel-Strike

#cobaltstrike #socks #proxy #redteam
  • 🔥 4
  • 👎 1
Post #780 2K
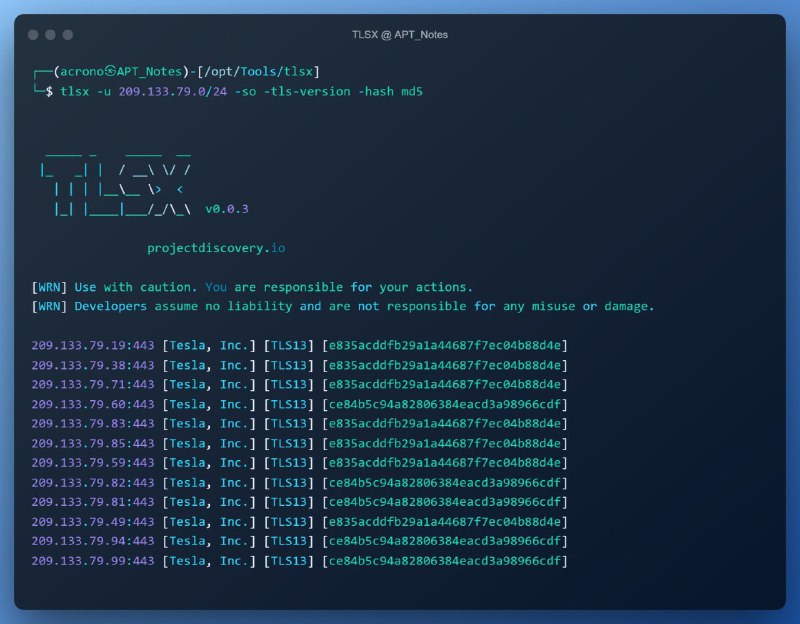
🔒 TLSX

Collection of additional assets of a target CIDR/IP/HOST from TLS certificates.

Features:
— Fast And fully configurable TLS Connection
— Multiple Modes for TLS Connection
— Multiple TLS probes
— Auto TLS Fallback for older TLS version
— Pre Handshake TLS connection (early termination)
— Customizable Cipher / SNI / TLS selection
— TLS Misconfigurations
— HOST, IP, URL and CIDR input
— STD IN/OUT and TXT/JSON output

Example:
tlsx -u 209.133.79.0/24 -san -cn -silent -resp-only | dnsx -silent | httpx | nuclei

https://github.com/projectdiscovery/tlsx

#recon #tls #grabber #tools
  • 👍 5
  • 👎 1
Post #777 2.29K
🔴 Reversing BRc4 Red-Teaming Tool Used by APT 29

On May 19, a malicious payload associated with Brute Ratel C4 (BRc4) was uploaded to VirusTotal, where it received a benign verdict from all 56 vendors that evaluated it. Beyond the obvious detection concerns, we believe this sample is also significant in terms of its malicious payload, command and control (C2), and packaging.

Blog post:
https://unit42.paloaltonetworks.com/brute-ratel-c4-tool/

Reversing the Malware by IppSec:
https://youtu.be/a7W6rhkpVSM

#maldev #c2 #brc4
Unit 42 When Pentest Tools Go Brutal: Red-Teaming Tool Being Abused by Malicious Actors Pentest and adversary emulation tool Brute Ratel C4 is effective at defeating modern detection capabilities – and malicious actors have begun to adopt it.
  • 👍 3
  • 👎 1
Post #776 2.91K
🐞 Malware Development for Dummies

In the age of EDR, red team operators cannot get away with using pre-compiled payloads anymore. As such, malware development is becoming a vital skill for any operator. Getting started with maldev may seem daunting, but is actually very easy. This workshop will show you all you need to get started!

Slides:
https://github.com/chvancooten/maldev-for-dummies/tree/main/Slides

Exercises:
https://github.com/chvancooten/maldev-for-dummies/tree/main/Exercises

#maldev #csharp #nim
  • 👍 4
Post #774 2.74K
⚔️ Maelstrom: C2 Development Blog Series

We wanted to explore how C2s function in 2022, what evasive behavior's are required, and what a minimum viable C2 looks like in a world of sophisticated endpoint protection.

Which gave us our goals for this blog series:

- Document the internals of a minimum viable C2:
* What are the ideas behind popular C2 implementations?
* What are their goals and objectives?
- Analyse and implement evasive behaviors:
* What is required to run on a contemporary Windows system?
* What is required to bypass up-to-date, modern endpoint protection?
- Produce a proof-of-concept C2:
* What is the minimum viable C2 for an operator in 2022?
* What is required to detect this minimum viable C2?

🔗 Maelstrom: An Introduction
🔗 Maelstrom: The C2 Architecture
🔗 Maelstrom: Building the Team Server
🔗 Maelstrom: Writing a C2 Implant
🔗 Maelstrom: EDR Kernel Callbacks, Hooks, and Call Stacks

#maldev #c2
  • 👍 8
Post #773 1.86K
Post #771 2.24K
⚙️ A Few Ways to Get TrustedInstaller Privileges

GetTrustedInstaller

Make an executable run with TrustedInstaller permissions under SYSTEM account.

https://github.com/rara64/GetTrustedInstaller

NtObjectManager

This module adds a provider and cmdlets to access the NT object manager namespace.

Example. Apply TrustedInstaller impersonation token to the current PowerShell process:

Install-Module -Name NtObjectManager -Confirm:$false
Restart-Service TrustedInstaller
$procId = (Get-Process TrustedInstaller).Id
$token = Get-NtTokenFromProcess -ProcessId $procId
$current = Get-NtThread -Current -PseudoHandle
$ctx = $current.Impersonate($token)
$impToken = Get-NtToken -Impersonation
$impToken.Groups

https://github.com/googleprojectzero/sandbox-attacksurface-analysis-tools/tree/main/NtObjectManager

#localsystem #trustedinstaller
  • 👍 9
Post #770 1.89K
🔎 ldeep

In-depth LDAP enumeration utility.

https://github.com/franc-pentest/ldeep

Install:

$ pip3 install ldeep

Usage Example:

Enumerate ACEs of the AdminSDHolder object

$ ldeep ldap -s 'ldap://10.10.13.37' -d megacorp -u j.doe -p 'Passw0rd!' -b 'CN=System,DC=megacorp,DC=local' sddl AdminSDHolder | jq '.[].nTSecurityDescriptor.DACL.ACEs[] | select(.Type | contains("Allowed")) | .SID + " :: " + .Type'

Convert SID to name

$ ldeep ldap -s 'ldap://10.10.13.37' -d megacorp -u j.doe -p 'Passw0rd!' from_sid <SID>

#ad #ldap
  • 🔥 5
  • 👍 1
Post #769 2.18K
😡 Brute-Ratel-C4-Community-Kit

This repository contains scripts, configurations and deprecated payload loaders for Brute Ratel C4. Anything which is added in the deprecated folder will not be a part of the latest release of BRc4.

https://github.com/paranoidninja/Brute-Ratel-C4-Community-Kit

#c2 #bof #shellcode #injection
GitHub GitHub - paranoidninja/Brute-Ratel-C4-Community-Kit: This repository contains scripts, configurations and deprecated payload loaders… This repository contains scripts, configurations and deprecated payload loaders for Brute Ratel C4 (https://bruteratel.com/) - paranoidninja/Brute-Ratel-C4-Community-Kit
Post #768 1.78K
📡 Relaying to ADFS Attacks

Praetorian has developed and is releasing an open source tool ADFSRelay and NTLMParse, which can be used for performing relaying attacks targeting ADFS and analyzing NTLM messages respectively.

https://www.praetorian.com/blog/relaying-to-adfs-attacks/

#ad #adfs #relay #ntlm
Praetorian Relaying to ADFS Attacks Overview During red team engagements over the last few years, I’ve been curious whether it would be possible to authenticate to cloud services such as Office365 via a relay from New Technology Lan Manager (NTLM) to Active Directory Federation Services (ADFS).…
  • ❤‍🔥 5
  • 🔥 1
Post #767 1.55K

Forwarded from SHADOW:Group

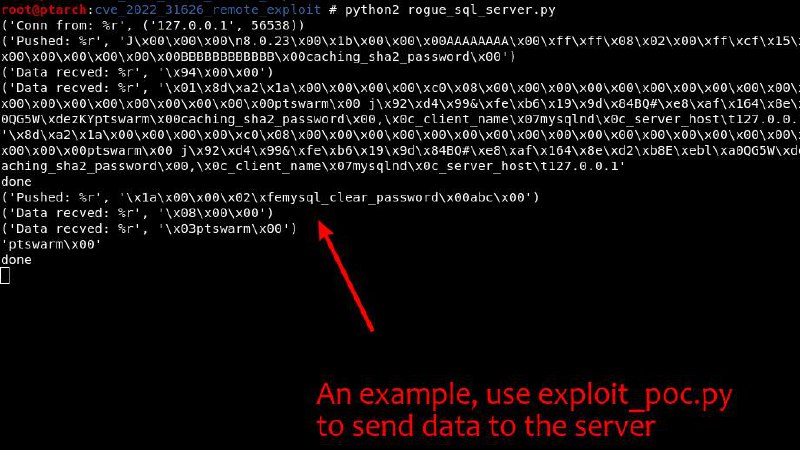
​​🐘 Удаленная эксплуатация переполнения кучи в веб-приложениях PHP (CVE 2022-31626)

Представлен PoC для RCE уязвимости в PHP <=7.4.29, которая может быть запущена через мошеннический сервер MySQL/MariaDB.

Ссылка на PoC

#web #rce
Post #766 1.91K
🦠 Mangle

Mangle is a tool that manipulates aspects of compiled executables (.exe or DLL). Mangle can remove known Indicators of Compromise (IoC) based strings and replace them with random characters, change the file by inflating the size to avoid EDRs, and can clone code-signing certs from legitimate files. In doing so, Mangle helps loaders evade on-disk and in-memory scanners.

https://github.com/optiv/Mangle

#av #edr #memory #evasion #redteam
GitHub GitHub - optiv/Mangle: Mangle is a tool that manipulates aspects of compiled executables (.exe or DLL) to avoid detection from… Mangle is a tool that manipulates aspects of compiled executables (.exe or DLL) to avoid detection from EDRs - optiv/Mangle
  • ❤‍🔥 7
Post #765 1.74K
😈 How to Detect Linux Anti-Forensics Log Tampering

When forensically examining Linux systems for malicious intrusion, responders often rely on the following three artefacts to determine logins and logouts:

— /var/run/utmp – currently logged in users
— /var/run/wtmp – current, past logins and system reboot
— /var/log/btmp – bad login attempts

Of course, these artefacts are not all you can forensically investigate for malicious access, however, these will be the focus of this anti-forensics blog post.

https://www.inversecos.com/2022/06/detecting-linux-anti-forensics-log.html

#linux #log #evasion #antiforensics
  • 👍 4
Older posts →
Threads Profile ViewerView any public Threads profile without an account.Open ThreadLook →Writing with AI? Make it sound human.Metric37 rewrites AI drafts so they read naturally. Free AI detector, 1,500 words free.Try Metric37 →