TGViewer
Channel Public Channel
APT

APT

@apt_notes

This channel discusses:

— Offensive Security
— RedTeam
— Malware Research
— OSINT
— etc

Disclaimer:
t.me/APT_Notes/6

Chat Link:
t.me/APT_Notes_PublicChat
Subscribers
16.7K
Photos
565
Videos
28
Links
909

Showing posts older than #765 · Back to latest

Older Posts 17 shown
Post #764 1.86K
🦠 Hiding C2 Traffic Using Tyk.io

A small article on the topic of hiding your malicious C2 traffic through of the TYK cloud API management service domains.
Tyk API gateway will let you manage your API ingress and routing them to different endpoints, some of them could be internally but some of them could be publicly exposed, and you can add some controls for authentication purposes while calling one of your APIs.

🔗 https://shells.systems/oh-my-api-abusing-tyk-cloud-api-management-service-to-hide-your-malicious-c2-traffic/

#c2 #rederectors #trafic #redteam
  • 👍 5
  • 🔥 2
Post #763 1.7K
APT 🐙🐍 OctoPwn & OctoPwnWeb Pentest framework running (almost) entirely in the browser via pyodide. OctoPwnWeb has been presented a41con. Talk: https://youtu.be/jStdrDHTmD4 Slides: https://docs.google.com/presentation/d/1XQFYr_OBI1lrpybsLrHWTWcYNZcF_zOmGDHiIBwSMng…
How it started:

“I waited 2 years for this, rewrote impacket for this, asked cryptographers to remake algos in python for this, spent enormous time of my life to make this happen. and it's finally here this finally works and I can't find the words to express my satisfaction.” (SkelSec)

“For the record: the two crypto guys who eventually helped me in pure-python rewrite of some algos tole me to never ever use it anywhere and also they dont want to be mentioned.” (SkelSec)
  • 👍 2
Post #762 1.98K
🐙🐍 OctoPwn & OctoPwnWeb

Pentest framework running (almost) entirely in the browser via pyodide. OctoPwnWeb has been presented a41con.

Talk:
https://youtu.be/jStdrDHTmD4

Slides:
https://docs.google.com/presentation/d/1XQFYr_OBI1lrpybsLrHWTWcYNZcF_zOmGDHiIBwSMng

Tool:
http://octopwn.porchetta.industries/

Repository:
https://github.com/skelsec/octopwnweb

Readme:
http://octopwn.porchetta.industries/readme.html

Sponsor for more features:
https://porchetta.industries

#pentest #framework
  • 👍 5
  • 🔥 2
Post #761 2.38K
🧲 PoC for MS-DFSNM coerce authentication using NetrDfsRemoveStdRoot method

Spooler service disabled, RPC filters installed to prevent PetitPotam and File Server VSS Agent Service not installed but you still want to relay DC authentication to ADCS? Don't worry MS-DFSNM have your back:

🔗 https://github.com/Wh04m1001/DFSCoerce

Inspired by:

🔗 https://github.com/topotam/PetitPotam
🔗 https://github.com/ShutdownRepo/ShadowCoerce
🔗 https://github.com/leechristensen/SpoolSample

#authentication #coercion #petitpotam #dfsnm
  • 🔥 7
  • 👍 2
Post #760 1.26K

Forwarded from RedTeam brazzers

Bitrix.pdf799.4 KB
Меньше месяца назад вышло исследование под названием "Уязвимости и атаки на CMS Bitrix". Вдохновившись этим исследованием, мой коллега Юрий (Компания BSS-Security) докрутил один из путей до RCE. Пообшавшись с разработчиками и убедившись, что уязвимость в последней версии устранена - со спокойной душой выкладываем разбор и PoC уязвимости.
Ну и как всегда рекомендация - обновляйтесь вовремя))
  • 🔥 9
Post #758 1.84K
APT 📜 Abuse AD CS via dNSHostName Spoofing This blog covers the technical details of CVE-2022-26923. Active Directory Domain Services Elevation of Privilege Vulnerability via AD CS dNSHostName Spoofing. https://research.ifcr.dk/certifried-active-directory-domain…
📜 Defused That SAN Flag

One more post about Microsoft's recent security updates - re changes to Kerberos and the new certificate extension containing the requester's SID.
The changes 'defuse' the impact of the flag that allows adding custom subject alternative names to any certificate (including the ones that 'actually' should be auto-enrolled).

https://elkement.blog/2022/06/13/defused-that-san-flag/

#ad #adcs #privesc #redteam
  • 👍 2
Post #754 2.36K
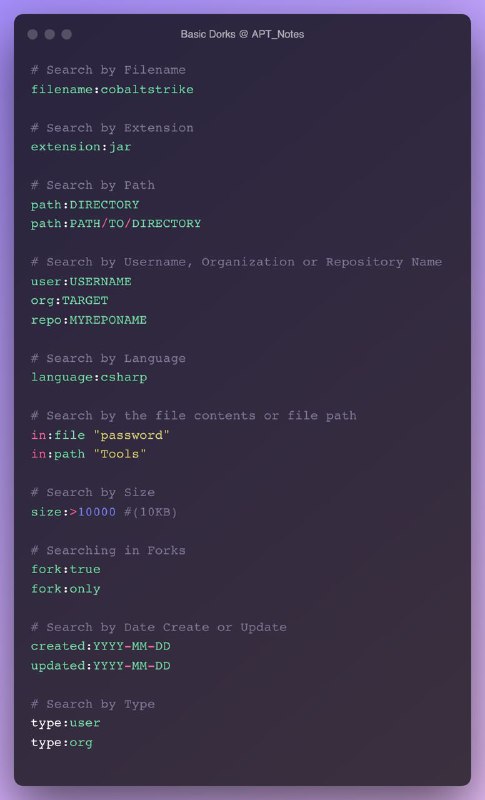
🔍 GitHub Dorks

Many people ask me how to do GitHub reconnaissance, find credentials and other information Pentest or RedTeam might need.
This post will look at some ways to search GitHub.

#github #dorks #recon #osint
  • 🔥 6
  • 👍 1
Post #752 1.51K

Forwarded from Codeby

🔥 Фильм о команде Codeby на The Standoff 2022

Друзья, уже в скором времени мы будем готовы представить вам документальный фильм об участии команды Codeby на мероприятии The Standoff 2022!

Вспомним, какие эмоции испытывали все мы каждый день соревнований, а также узнаем, что происходило в эти дни от лица игроков. А пока предлагаем вам насладиться просмотром небольшого трейлера!
  • 🔥 16
  • 👍 1
  • 👎 1
Post #751 1.83K
⚙️ Active Directory Delegation Management Tool

Is an Active Directory delegation management tool. It allows you to make a detailed inventory of delegations set up so far in a forest, along with their potential issues:

— Objects owned by users
— Objects with ACEs for users
— Non canonical ACL
— Disabled ACL inheritance
— Default ACL modified in schema
— Deleted delegation trustees

It also allows you to document your delegation model in JSON files, to obtain a more readable view:

https://github.com/mtth-bfft/adeleg

#ad #delegations #ace #acl #tools
  • 🔥 3
  • 👍 1
Post #750 1.66K

Forwarded from 1N73LL1G3NC3

1N73LL1G3NC3 Malware development: persistence - part 1. Registry run keys. C++ example. Malware development: persistence - part 2. Screensaver hijack. C++ example. Malware development: persistence - part 3. COM DLL hijack.
Malware development: persistence - part 4. Windows services. Simple C++ example.

Malware development: persistence - part 5. AppInit_DLLs. Simple C++ example.

Malware development: persistence - part 6. Windows netsh helper DLL. Simple C++ example.
cocomelonc Malware development: persistence - part 4. Windows services. Simple C++ example. ﷽
Post #747 3.37K
📒Simulating attacks with Sysmon

SysmonSimulator is an Open source Windows event simulation utility created in C language, that can be used to simulate most of the attacks using WINAPIs. This can be used by Blue teams for testing the EDR detections and correlation rules. I have created it to generate attack data for the relevant Sysmon Event IDs.

Attack coverage:

— Process Events
— File Events
— Named Pipes Events
— Registry Actions
— Image Loading
— Network Connections
— Create Remote Thread
— Raw Access Read
— DNS Query
— WMI Events
— Clipboard Capture
— Process Image Tampering

Research:
https://rootdse.org/posts/understanding-sysmon-events/

Tool:
https://github.com/ScarredMonk/SysmonSimulator

#sysmon #simulator #blueteam #lab
  • 👍 9
Post #746 4.46K
🔥 MS-MSDT Office RCE

MS Office docx files may contain external OLE Object references as HTML files. There is an HTML sceme "ms-msdt:" which invokes the msdt diagnostic tool, what is capable of executing arbitrary code (specified in parameters). The result is a terrifying attack vector for getting RCE through opening malicious docx files (without using macros).

Research:
https://doublepulsar.com/follina-a-microsoft-office-code-execution-vulnerability-1a47fce5629e

PoC:
https://github.com/JohnHammond/msdt-follina
https://github.com/chvancooten/follina.py
https://gist.github.com/tothi/66290a42896a97920055e50128c9f040

Demo Follina with Cobalt Strike:
https://www.youtube.com/watch?v=oM4GHtVvv1c

For BlueTeam:
https://gist.github.com/kevthehermit/5c8d52af388989cfa0ea38feace977f2

Everything new is well-forgotten old:
Research from August 2020. And a few other payloads.

#office #rce #msmsdt #nomacro
  • 🔥 14
  • 👍 7
Older posts →
Threads Profile ViewerView any public Threads profile without an account.Open ThreadLook →Writing with AI? Make it sound human.Metric37 rewrites AI drafts so they read naturally. Free AI detector, 1,500 words free.Try Metric37 →