TGViewer
Channel Public Channel
APT

APT

@apt_notes

This channel discusses:

— Offensive Security
— RedTeam
— Malware Research
— OSINT
— etc

Disclaimer:
t.me/APT_Notes/6

Chat Link:
t.me/APT_Notes_PublicChat
Subscribers
16.8K
Photos
565
Videos
28
Links
909

Showing posts older than #724 · Back to latest

Older Posts 17 shown
Post #723 871

Forwarded from SHADOW:Group

🧨 RCE в BIG-IP iControl REST (CVE-2022-1388)

Эта уязвимость может позволить неаутентифицированному злоумышленнику с сетевым доступом к системе BIG-IP выполнять произвольные системные команды, создавать или удалять файлы или отключать службы (CVE-2022-1388)

Дорк для Shodan:

http.title:"BIG-IP®-+Redirect" +"Server"

PoC представлен на изображении ниже или по ссылке.

Ссылка на PoC

#web #cve #rce
Post #722 927
⏱ Scheduled Task Tampering

In this post we will explore two approaches that can be used to achieve the same result: create or modify a scheduled task and execute it, without generating the relevant telemetry. First, we will explore how direct registry manipulation could be used to create or modify tasks and how this did not generate the usual entries in the eventlog. Finally, an alternative route based on tampering with the Task Scheduler ETW will be presented that will completely suppress most of logging related to the Task Scheduler.

https://labs.f-secure.com/blog/scheduled-task-tampering/

#windows #schedule #task #redteam #blueteam
Post #720 1.06K
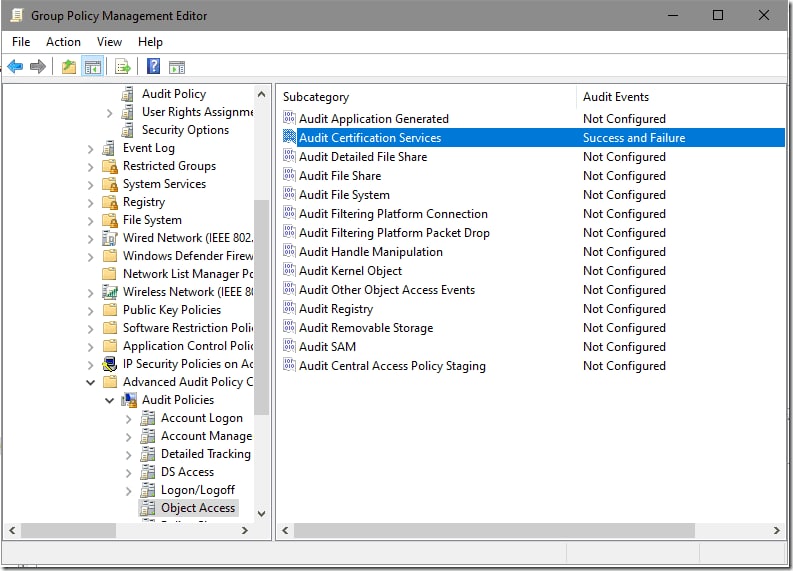
📒 Enabling ADCS Audit and Fix Bad Configs

Auditing is not enabled by default in AD CS. For some mysterious reason, Microsoft has decided to not enable AD CS auditing OOB.

To find the issue, run this command on every one of your CAs:
certutil -getreg CA\AuditFilter

To enable all auditing, do this:
certutil –setreg CA\AuditFilter 127
net stop certsvc
net start certsvc

You'll also need to enable the Certificate Service advanced auditing subcategories in a GPO linked to the OU containing your CA host objects (Figure 1). Lastly, enforce the advanced auditing subcategories! All of your previous work will be for naught if you don't enforce (Figure 2).

Fix for AD CS Templates with Bad Configs:
https://github.com/trimarcjake/adcs-snippets#fix-1-for-templates-with-bad-configs---remove-ability-to-set-a-san

#adcs #audit #recommendations #blueteam
  • 👍 3
Post #718 1.81K
APT KrbRelay with RBCD Privilege Escalation The short step-by-step writeup about how to do the LPE with KrbRelay + RBCD on a domain-joined machine using KrbRelay + Rubeus: https://gist.github.com/tothi/bf6c59d6de5d0c9710f23dae5750c4b9 #ad #kerberos #relay #rbcd…
NTLMRelay2Self over HTTP

Just a walkthrough of how to escalate privileges locally by forcing the system you landed initial access on to reflectively authenticate over HTTP to itself and forward the received connection to an HTTP listener (ntlmrelayx) configured to relay to DC servers over LDAP/LDAPs for either setting shadow credentials or configuring RBCD.

https://github.com/med0x2e/NTLMRelay2Self

#ad #ntlm #relay #rbcd #redteam
GitHub GitHub - med0x2e/NTLMRelay2Self: An other No-Fix LPE, NTLMRelay2Self over HTTP (Webdav). An other No-Fix LPE, NTLMRelay2Self over HTTP (Webdav). - med0x2e/NTLMRelay2Self
  • 👍 4
Post #714 1.23K
APT KrbRelayUp Universal no-fix local privilege escalation in windows domain environments where LDAP signing is not enforced (the default settings) https://github.com/Dec0ne/KrbRelayUp #ad #privesc #kerberos #ldap #relay
KrbRelay with RBCD Privilege Escalation

The short step-by-step writeup about how to do the LPE with KrbRelay + RBCD on a domain-joined machine using KrbRelay + Rubeus:

https://gist.github.com/tothi/bf6c59d6de5d0c9710f23dae5750c4b9

#ad #kerberos #relay #rbcd #redteam
  • 🔥 5
  • 👍 1
Post #713 887
Post #712 820
NTLM Relay

This article is not meant to be a tutorial to be followed in order to carry out a successful attack, but it will allow the reader to understand in detail the technical details of this attack, its limitations, and can be a basis to start developing his own tools, or understand how current tools work.

https://en.hackndo.com/ntlm-relay/

#ad #relay #ntlm #ntlmrelay
hackndo NTLM Relay NTLM relay is a technique of standing between a client and a server to perform actions on the server while impersonating the client. Protections such as SMB signing or MIC allow to limit the actions of an attacker. This article goes into detail about this…
Post #710 1.09K
KrbRelayUp

Universal no-fix local privilege escalation in windows domain environments where LDAP signing is not enforced (the default settings)

https://github.com/Dec0ne/KrbRelayUp

#ad #privesc #kerberos #ldap #relay
  • 🔥 5
Post #706 830
Invoke-SocksProxy

The reverse proxy creates a tcp tunnel by initiating outbond SSL connections that can go through the system's proxy. The tunnel can then be used as a socks proxy on the remote host to pivot into the local host's network.

https://github.com/p3nt4/Invoke-SocksProxy

#powershell #socks #proxy #tools
GitHub GitHub - p3nt4/Invoke-SocksProxy: Socks proxy, and reverse socks server using powershell. Socks proxy, and reverse socks server using powershell. - p3nt4/Invoke-SocksProxy
Post #705 1.03K
WSO2 RCE (CVE-2022-29464)

Critical vulnerability on WSO2 discovered by Orange Tsai. the vulnerability is an unauthenticated unrestricted arbitrary file upload which which allows unauthenticated attackers to gain RCE on WSO2 servers via uploading malicious JSP files.

Google Dorks:
inurl:"/carbon/admin/login.jsp"
inurl:"/authenticationendpoint/login.do"
inurl:"devportal/apis"
intitle:"API Publisher- Login"
intitle:"WSO2 Management Console"

https://github.com/hakivvi/CVE-2022-29464

#wso2 #rce #exploit
  • ❤ 1
Older posts →
Threads Profile ViewerView any public Threads profile without an account.Open ThreadLook →Writing with AI? Make it sound human.Metric37 rewrites AI drafts so they read naturally. Free AI detector, 1,500 words free.Try Metric37 →