TGViewer
Channel Public Channel
APT

APT

@apt_notes

This channel discusses:

— Offensive Security
— RedTeam
— Malware Research
— OSINT
— etc

Disclaimer:
t.me/APT_Notes/6

Chat Link:
t.me/APT_Notes_PublicChat
Subscribers
16.8K
Photos
565
Videos
28
Links
909

Showing posts older than #559 · Back to latest

Older Posts 20 shown
Post #558 629
DetectionLab

DetectionLab is a repository containing a variety of Packer, Vagrant, Powershell, Ansible, and Terraform scripts that allow you to automate the process of bringing an ActiveDirectory environment online complete with logging and security tooling using a variety of different platforms.

DetectionLab can currently be deployed to the following platforms:

— Virtualbox (Windows, MacOS, Linux)
— VMware Workstation/Fusion (Windows, MacOS, Linux)
— HyperV
— ESXi
— AWS
— Azure
— LibVirt (Not officially supported)
— Proxmox (Not officially supported)

https://detectionlab.network/

#lab #cloud #blueteam #redteam
Post #556 523
Post #555 495
APT Grafana — Unauthorized Arbitrary Read File The latest Grafana unpatched 0Day LFI is now being actively exploited, it affects only Grafana 8.0+ Dorks: Shodan: title:"Grafana" Fofa.so: app="Grafana" ZoomEye: grafana PoC http://example.com/public/plugins/grafana…
A (not so deep) Dive into Grafana CVE-2021-43798

This post will cover some details behind the recent Grafana vulnerability (CVE-2021-43798), which is a directory traversal bug allowing unauthenticated attackers to read files on the target server filesystem. This post will also discuss some real world scenario and attack surface of the Grafana.

https://nusgreyhats.org/posts/writeups/a-not-so-deep-dive-in-to-grafana-cve-2021-43798/

#grafana #lfi #cve
NUS Greyhats A (not so deep) Dive into Grafana CVE-2021-43798 Tired of log4shell? take some rest then
Post #554 460
Windows 10 Hardening

The project started as a simple hardening list for Windows 10. After some time, HardeningKitty was created to simplify the hardening of Windows. Now, HardeningKitty supports guidelines from Microsoft, CIS Benchmarks, DoD STIG and BSI SiSyPHuS Win10

https://github.com/0x6d69636b/windows_hardening/

#blueteam #windows #hardening #benchmarks
GitHub GitHub - 0x6d69636b/windows_hardening: HardeningKitty and Windows Hardening Settings HardeningKitty and Windows Hardening Settings. Contribute to 0x6d69636b/windows_hardening development by creating an account on GitHub.
Post #552 456
Docem

A utility to embed XXE and XSS payloads in docx, odt, pptx, etc - any documents that is a zip archive with bunch of xml files inside.

https://github.com/whitel1st/docem

#xxe #xss #doc #file #upload
Post #551 478
Invoke-WinSATBypass

This script will create a mock directory of "C:\Windows\System32" and copy a legitimate application of Windows (WinSAT.exe) into it.
It will after try to download a DLL called version.dll, which is loaded by default by WinSAT.exe, in order to perform a UAC Bypass by doing some DLL Hijacking.

https://github.com/b4keSn4ke/Invoke-WinSATBypass

#uac #bypass #winsat #tools
Post #549 444
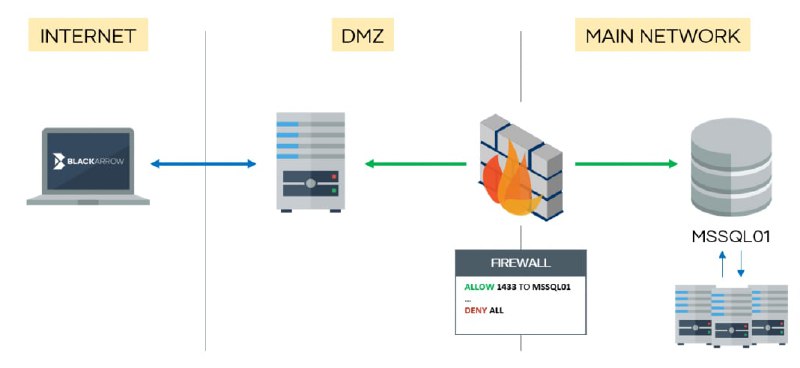
mssqlproxy

Toolkit aimed to perform lateral movement in restricted environments through a compromised Microsoft SQL Server via socket reuse. The client requires impacket and sysadmin privileges on the SQL server.

https://github.com/blackarrowsec/mssqlproxy

#mssql #proxy #pentest #tools
Post #548 403
Post #547 416
CloudSploit

CloudSploit's remediation guides are intended to be an open-source resource for improving cloud security. Many cloud IaaS providers like AWS, Azure, and Google Cloud have a shared responsibility model. They provide the physical and architectural security, along with tools to properly secure the services they offer, but it is up to the user to configure those settings properly.

https://github.com/aquasecurity/cloud-security-remediation-guides

#cloud #security #remediation #blueteam
GitHub GitHub - aquasecurity/cloud-security-remediation-guides: Security Remediation Guides Security Remediation Guides. Contribute to aquasecurity/cloud-security-remediation-guides development by creating an account on GitHub.
Post #546 617
moonwalk

moonwalk is a 400 KB single-binary executable that can clear your traces while penetration testing a Unix machine. It saves the state of system logs pre-exploitation and reverts that state including the filesystem timestamps post-exploitation leaving zero traces of a ghost in the shell.

https://github.com/mufeedvh/moonwalk

#unix #log #clearing #redteam
Post #543 584
Osmedeus

Fully automated offensive security framework for reconnaissance and vulnerability scanning

Features
— Subdomain Scan.
— Subdomain TakeOver Scan.
— Screenshot the target.
— Basic recon like Whois, Dig info.
— Web Technology detection.
— IP Discovery.
— CORS Scan.
— SSL Scan.
— Wayback Machine Discovery.
— URL Discovery.
— Headers Scan.
— Port Scan.
— Vulnerable Scan.
— Seperate workspaces to store all scan output and details logging.
— REST API.
— React Web UI.
— Support Continuous Scan.
— Slack notifications.
— Easily view report from commnad line.

https://github.com/j3ssie/Osmedeus

#osint #vulnerability #scanner #bugbounty
Post #542 562
Bug Bounty Tip — Log4j Vulnerability Cheatsheet

— How It Works
— Test Environments
— Challenges & Labs (Rooms)
— Where Payloads can be Injected
— What Information can be Extracted
— How To Identify (Services & Scanners)

#log4j #cheatsheet #bugbounty
  • ❤ 1
Post #538 497
Auto-Elevate

This tool demonstrates the power of UAC bypasses and built-in features of Windows. This utility auto-locates winlogon.exe, steals and impersonates it's process TOKEN, and spawns a new SYSTEM-level process with the stolen token. Combined with UAC bypass method #41 (ICMLuaUtil UAC bypass) from hfiref0x's UACME utility, this utility can auto-elevate a low privileged Administrative account to NT AUTHORITY\SYSTEM.

https://github.com/FULLSHADE/Auto-Elevate

#uac #bypass #windows #tools
Post #536 493
Older posts →
Threads Profile ViewerView any public Threads profile without an account.Open ThreadLook →Writing with AI? Make it sound human.Metric37 rewrites AI drafts so they read naturally. Free AI detector, 1,500 words free.Try Metric37 →