TGViewer
Channel Public Channel
APT

APT

@apt_notes

This channel discusses:

— Offensive Security
— RedTeam
— Malware Research
— OSINT
— etc

Disclaimer:
t.me/APT_Notes/6

Chat Link:
t.me/APT_Notes_PublicChat
Subscribers
16.8K
Photos
565
Videos
28
Links
909

Showing posts older than #441 · Back to latest

Older Posts 19 shown
Post #440 343
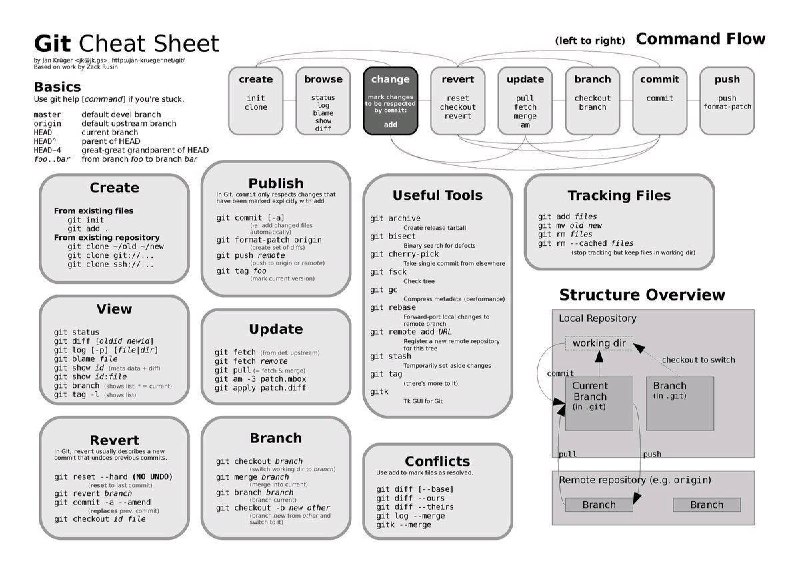
Git Cheat Sheet

#git #cheatsheet
Post #438 360
Living Off Trusted Sites (LOTS)

Attackers are using popular legitimate domains when conducting phishing, C&C, exfiltration and downloading tools to evade detection.

https://lots-project.com

#lots #redteam #blueteam #sites #upload
Post #435 396
SMBSR

Well, SMBSR is a python script which given a CIDR/IP/IP_file/HOSTNAME(s) enumerates all the SMB services listening (445) among the targets and tries to authenticate against them; if the authentication succeed then all the folders and subfolders are visited recursively in order to find secrets in files and ... secret files. In order to scan the targets for SMB ports open the masscan module is used.

https://github.com/oldboy21/SMBSR

#smb #share #secrets #redteam
GitHub GitHub - oldboy21/SMBSR: Lookup for interesting stuff in SMB shares Lookup for interesting stuff in SMB shares. Contribute to oldboy21/SMBSR development by creating an account on GitHub.
Post #434 500
NanoDump

Dumping LSASS has never been so stealthy

Features
• It uses syscalls (with SysWhispers2) for most operations
• You can choose to download the dump without touching disk or write it to a file
• The minidump by default has an invalid signature to avoid detection
• It reduces the size of the dump by ignoring irrelevant DLLs. The (nano)dump tends to be arround 10 MB in size
• You don't need to provide the PID of LSASS
• No calls to dbghelp or any other library are made, all the dump logic is implemented in nanodump
• You can use the .exe version to run nanodump outside of Cobalt Strike

https://github.com/helpsystems/nanodump

#dump #lsass #syswhispers
Post #429 414
MacOS — CVE-2021-30657 (POC)

A vulnerability in syspolicyd allows specially crafted application bundle downloaded from internet to
bypass foundational macOS security features such as File Quarantine, Gatekeeper, and Notarization.
Armed with this capability attackers could hack macOS systems with a simple user (double)-click.

https://github.com/shubham0d/CVE-2021-30657

#macos #poc #cve #syspolicyd
GitHub GitHub - shubham0d/CVE-2021-30657: A sample POC for CVE-2021-30657 affecting MacOS A sample POC for CVE-2021-30657 affecting MacOS. Contribute to shubham0d/CVE-2021-30657 development by creating an account on GitHub.
Post #428 428
KubiScan

KubiScan helps cluster administrators identify permissions that attackers could potentially exploit to compromise the clusters. This can be especially helpful on large environments where there are lots of permissions that can be challenging to track. KubiScan gathers information about risky roles\clusterroles, rolebindings\clusterrolebindings, users and pods, automating traditional manual processes and giving administrators the visibility they need to reduce risk.

https://github.com/cyberark/KubiScan

#kubernetes #rbac #scan #security #tools
GitHub GitHub - cyberark/KubiScan: A tool to scan Kubernetes cluster for risky permissions A tool to scan Kubernetes cluster for risky permissions - cyberark/KubiScan
Post #426 521
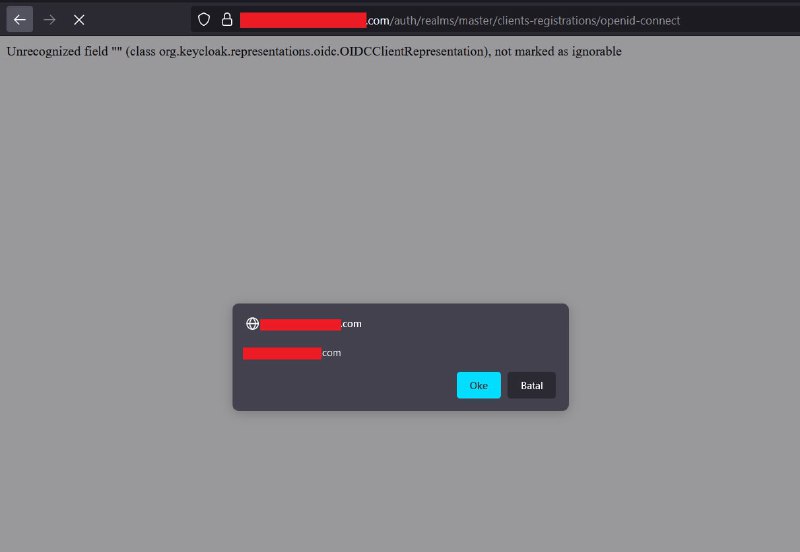
Keycloak POST-based Reflected XSS

1
. POST /auth/realms/master/clientsregistrations/openid-connect
2. Content-Type: application/json
3. Request {"<svg onload=alert(document.domain)>":1}
4. Unfiltered user-input in error message will triggered XSS

#bugbounty #keycloak #xss
Post #423 371

Forwarded from PT SWARM

How to exploit CVE-2021-40539 on ManageEngine ADSelfService Plus

👤 by Antoine Cervoise, Wilfried Bécard

ADSS offers multiple functionalities such as managing password policies for administrators or self password reset/account unlock for Active Directory users.
In this article research team explore the details of several vulnerabilities that allow an unauthenticated attacker to execute arbitrary code on the server.

📝 Contents:
• First steps
• Authentication Bypass
• Arbitrary file upload through the API
• Arguments injection
• Chaining everything together to get code execution
• Conclusion

https://www.synacktiv.com/publications/how-to-exploit-cve-2021-40539-on-manageengine-adselfservice-plus.html
Synacktiv How to exploit CVE-2021-40539 on ManageEngine ADSelfService Plus
Post #422 372
ScoutSuite

Scout Suite is an open source multi-cloud security-auditing tool, which enables security posture assessment of cloud environments. Using the APIs exposed by cloud providers, Scout Suite gathers configuration data for manual inspection and highlights risk areas. Rather than going through dozens of pages on the web consoles, Scout Suite presents a clear view of the attack surface automatically.

# https://github.com/nccgroup/ScoutSuite
# https://github.com/nccgroup/sadcloud

#aws #azure #gcp #auditing #tool
GitHub GitHub - nccgroup/ScoutSuite: Multi-Cloud Security Auditing Tool Multi-Cloud Security Auditing Tool. Contribute to nccgroup/ScoutSuite development by creating an account on GitHub.
Post #421 681
LOLBAS Cmdl32.exe

It's like a new certutil.exe but absolutely unheard of by any antivirus software!
"C:\Windows\System32\Cmdl32.exe" (signed by MS) is for you.

#lolbin #lolbas
Post #420 458
Django Debug Mode Bypass

https://target/login?next=/

https://target/admin
[301 to https://target/admin/login/?next=/admin/]

Change request to [POST]
[500 Django DEBUG mode and vary bad information]

#bugbounty #bugbountytips #bugbountytip
Older posts →
Threads Profile ViewerView any public Threads profile without an account.Open ThreadLook →Writing with AI? Make it sound human.Metric37 rewrites AI drafts so they read naturally. Free AI detector, 1,500 words free.Try Metric37 →