TGViewer
APT APT @apt_notes · 16.9K subscribers
Post #407 859
🔥 Antivirus Bypass using Code Signing 🔥

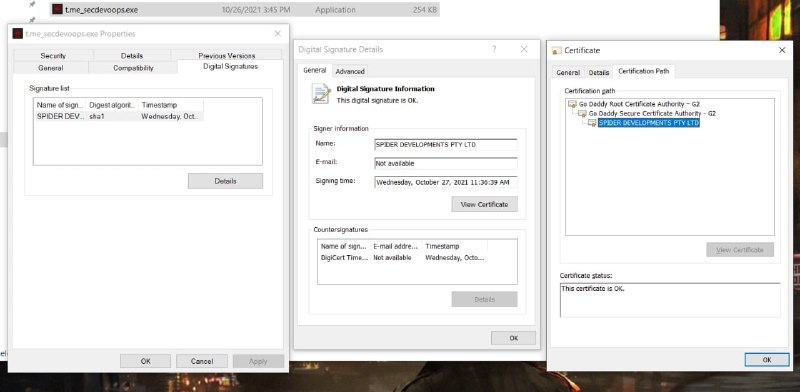
Code signing is a method software publishers use to authenticate the programs they distribute to end-users. Basically, a code-signed program tells the end-user and an end-user’s computer that the program being installed/executed is from a legitimate software publisher.

Digitally signed malware can bypass system protection mechanisms that install or launch only programs with valid signatures

You can use the SignTool to sign file with a valid certificate Go Daddy.
For example:

signtool.exe sign /f t.me_secdevoops.pfx /p "*Aspider#" /t http://timestamp.digicert.com .\yourfile
.exe

This allows you to digitally sign PE binaries such as .exe, .cab, .dll, .ocx, .msi, .xpi and .xap files.

Don't forget to share and subscribe

#av #bypass #ev #signing #code
More from @apt_notes
  1. Sep 1, 2026🔒 Certi-Bhai — IIS AppPool → NT AUTHORITY\SYSTEM via AD CS RPC A webshell under IIS AppPo…
  2. Aug 17, 2026🔒 Citrix NetScaler Pre-Auth RCE (CVE-2026-8452) Unauthenticated heap overflow in SAML sig…
  3. Aug 11, 2026Post #1201
  4. Aug 7, 2026ResetNightmare ResetNightmare (CVE-2026-27912) is a validation flaw in the Kerberos Change…
  5. Jul 24, 2026🔒 Certighost (CVE-2026-54121) — AD CS Domain Controller Impersonation Low-privileged doma…
  6. Jul 9, 2026💉 P³ — Shellcode Loader: Process Parameter Poisoning This loader implements a code inject…
Threads Profile ViewerView any public Threads profile without an account.Open ThreadLook →Writing with AI? Make it sound human.Metric37 rewrites AI drafts so they read naturally. Free AI detector, 1,500 words free.Try Metric37 →