TGViewer
APT APT @apt_notes · 16.7K subscribers
Post #906 3.4K
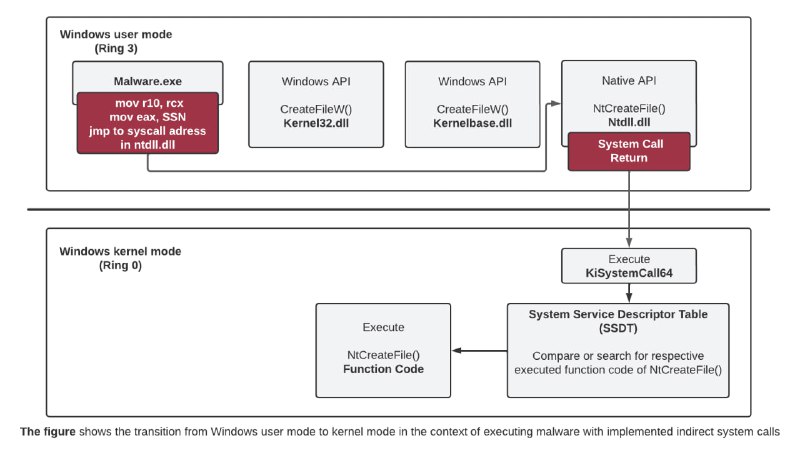
🔀 Direct Syscalls vs Indirect Syscalls

This post discusses Indirect Syscalls as a solution to eliminate indicators of compromise and avoid detection by EDRs. Indirect Syscalls allow the execution of Syscall and Return statements in the memory of ntdll.dll, which is the usual behavior in Windows.

https://redops.at/en/blog/direct-syscalls-vs-indirect-syscalls

#maldev #syscall #edr #bypass
  • 🔥 8
  • 👍 3
More from @apt_notes
  1. Sep 1, 2026🔒 Certi-Bhai — IIS AppPool → NT AUTHORITY\SYSTEM via AD CS RPC A webshell under IIS AppPo…
  2. Aug 17, 2026🔒 Citrix NetScaler Pre-Auth RCE (CVE-2026-8452) Unauthenticated heap overflow in SAML sig…
  3. Aug 11, 2026Post #1201
  4. Aug 7, 2026ResetNightmare ResetNightmare (CVE-2026-27912) is a validation flaw in the Kerberos Change…
  5. Jul 24, 2026🔒 Certighost (CVE-2026-54121) — AD CS Domain Controller Impersonation Low-privileged doma…
  6. Jul 9, 2026💉 P³ — Shellcode Loader: Process Parameter Poisoning This loader implements a code inject…
Threads Profile ViewerView any public Threads profile without an account.Open ThreadLook →Writing with AI? Make it sound human.Metric37 rewrites AI drafts so they read naturally. Free AI detector, 1,500 words free.Try Metric37 →