
🚀 Elevating Privileges in Windows via Activation Cache Poisoning
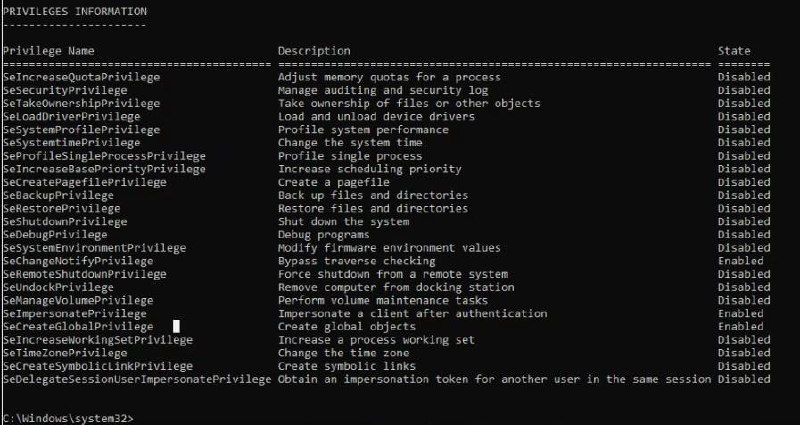
A deep dive into CVE-2024-6769, which leverages two chained bugs to escalate privileges from medium to high integrity. The first stage involves remapping the root drive, followed by a DLL hijacking exploit. The second stage poisons the Activation Cache through the CSRSS process to gain full administrator access.
🔗 Research:
https://www.coresecurity.com/core-labs/articles/cve-2024-6769-poisoning-activation-cache-elevate-medium-high-integrity
🔗 Source:
https://github.com/fortra/CVE-2024-6769
#windows #privesc #dll #hijacking
Post #1110
6.59K
- 🔥 10
- 👍 4
- ❤🔥 1