TGViewer
Channel Public Channel
Android Security & Malware

Android Security & Malware

@androidmalware

Mobile cybersecurity channel
Links: https://linktr.ee/mobilehacker
Contact: mobilehackerofficial@gmail.com
Subscribers
44.8K
Photos
136
Videos
22
Links
2.9K

Showing posts older than #2722 · Back to latest

Older Posts 20 shown
Post #2718 7.77K
The Rise of NFC Relay Malware on Mobile Devices
Cybercriminals are spreading NFC relay malware that tricks you into placing your card against your phone’s NFC chip. Once you do, the malware silently captures and relays your card data to fraudsters, who can use it for unauthorized payments or ATM withdrawals.
Reports show these scams are growing fast across the globe, with hundreds of malicious apps already detected.
https://zimperium.com/blog/tap-and-steal-the-rise-of-nfc-relay-malware-on-mobile-devices
  • ❤ 19
  • 👍 4
Post #2716 8.5K
GhostGrab is a new Android malware blending crypto mining with banking credential theft.
It hijacks SMS OTPs, harvests PII, and runs a hidden Monero miner—draining battery while stealing funds.
It compromised over 30 devices and C&C server leaks over 2800 victim SMS
https://www.cyfirma.com/research/ghostgrab-android-malware/
  • 😱 18
  • ❤ 7
  • 👍 4
  • 🌚 4
  • 🎃 1
Post #2710 9.96K
Samsung Galaxy S25 pwned
Yesterday at Pwn2Own Ken Gannon and Dimitrios Valsamaras used five different bugs to exploit the Samsung Galaxy S25 and earn $50,000
  • 👍 35
  • 🔥 23
  • ❤ 4
Post #2706 6.39K
Account takeover in Android app via JavaScript bridge
A misconfigured addJavascriptInterface + flawed domain validation + javascript:// trick enabled full cookie exfiltration via WebView.
Exploit chain: JSB dispatcher → file access handler → bypass via newline injection.
Payload:
Delivered via deeplink.
Executed JSB call to toBase64.
Read Cookies file from app sandbox.
Exfiltrated session data via callback.
https://tuxplorer.com/posts/account-takeover-via-jsb/
  • 🌚 12
  • 🔥 5
  • ❤ 2
Post #2705 11K
A vulnerability in DuckDuckGo’s Android browser allows file exfiltration via malicious intent:// URLs to gain access to a victim’s Sync account data such as account credentials and email protection information (CVE-2025-48464)
https://tuxplorer.com/posts/dont-leave-me-outdated/
  • 🔥 29
  • 🌚 6
  • 👍 3
  • 🤡 3
Post #2702 13.8K
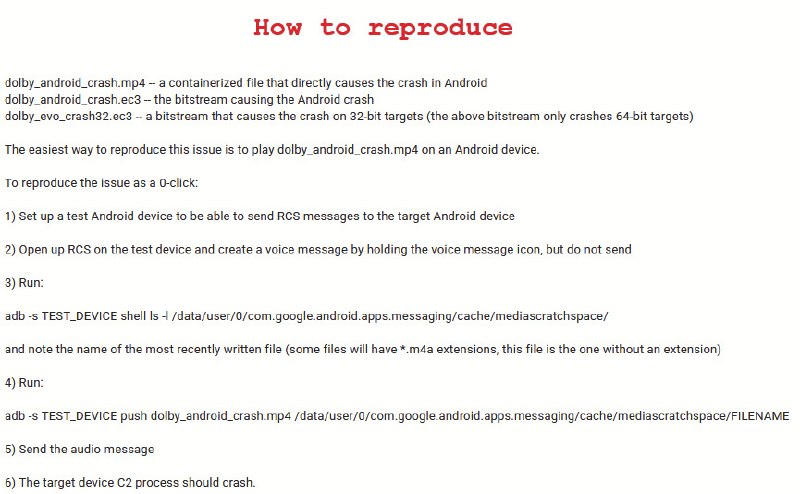
0-click vulnerability in Dolby's DDPlus decoder affected Android (CVE-2025-54957)
A malformed audio file can trigger an out-of-bounds write due to integer overflow in evolution data handling—leading to memory corruption and crashes.
Android decodes audio messages locally, making this exploitable without user interaction.
Reproduction: Just send a crafted RCS voice message (dolby_android_crash.mp4)
Details: https://project-zero.issues.chromium.org/issues/428075495
  • 🤯 24
  • ❤ 12
  • 😁 4
  • 👍 3
  • 🔥 3
Older posts →
Threads Profile ViewerView any public Threads profile without an account.Open ThreadLook →Writing with AI? Make it sound human.Metric37 rewrites AI drafts so they read naturally. Free AI detector, 1,500 words free.Try Metric37 →