TGViewer
Channel Public Channel
Android Security & Malware

Android Security & Malware

@androidmalware

Mobile cybersecurity channel
Links: https://linktr.ee/mobilehacker
Contact: mobilehackerofficial@gmail.com
Subscribers
44.9K
Photos
136
Videos
22
Links
2.9K

Showing posts older than #2702 · Back to latest

Older Posts 17 shown
Post #2698 7.27K
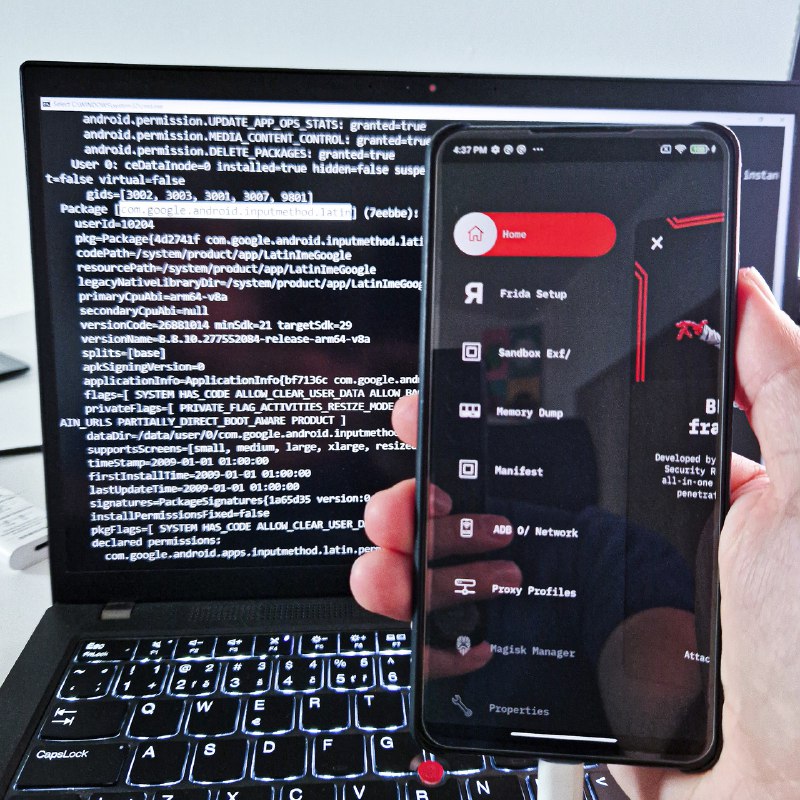
New Android BEERUS framework for dynamic analysis & reverse engineering
BEERUS brings Frida auto-injection, sandbox exfiltration, memory dumps, Magisk integration and more for on device app analysis.
https://github.com/hakaioffsec/beerus-android
  • 👍 22
  • 🔥 14
  • ❤ 4
  • 🤣 4
  • 👎 1
Post #2693 12K
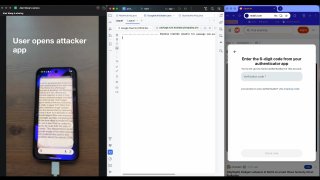
New Pixnapping Attack allows any Android app without permissions to leak info displayed by other apps exploiting Android APIs and a hardware side channel (CVE-2025-48561)
Pixnapping is not fixed and probably affects all Androids.
PoC: Not available yet.
Video demonstrates stealing 2FA codes from Google Authenticator. It's like taking screenshot. Pixnapping exploits a side channel that allows the malicious app to map the pixels at those coordinates to letters, numbers, or shapes.
Info: https://www.pixnapping.com/
  • 🤯 29
  • 👍 8
  • 👏 3
  • ❤ 2
Post #2691 8.18K
Post #2688 7.63K
iOS Crypto Heist: iMessage Zero-Click RCE Chain (CVE-2025-31200, CVE-2025-31201)
CVE-2025-31200 is a zero-day, zero-click RCE in iOS CoreAudio’s AudioConverterService, triggered by a malicious audio file via iMessage/SMS. Exploitation bypassed Blastdoor, enabled kernel escalation (CVE-2025-31201), and allowed token theft until patched in iOS 18.4.1 (Apr 16, 2025)
Info: https://github.com/JGoyd/iOS-Attack-Chain-CVE-2025-31200-CVE-2025-31201
PoC exploit: https://www.dropbox.com/scl/fi/oerpnhq1ui3xfswsszfh2/Audio-clip.amr?rlkey=7n54m1o84poezyipxvd2f9slx&e=3&st=b1tkonvr&dl=0
GitHub GitHub - JGoyd/iOS-Attack-Chain-CVE-2025-31200-CVE-2025-31201: CVE-2025-31200 is a zero-day, zero-click RCE in iOS CoreAudio’s… CVE-2025-31200 is a zero-day, zero-click RCE in iOS CoreAudio’s AudioConverterService, triggered by a malicious audio file via iMessage/SMS. Exploitation bypassed Blastdoor, enabled kernel escalati...
  • 🔥 16
  • 🤡 5
  • ❤ 1
Post #2687 7.84K
Post #2685 7.5K
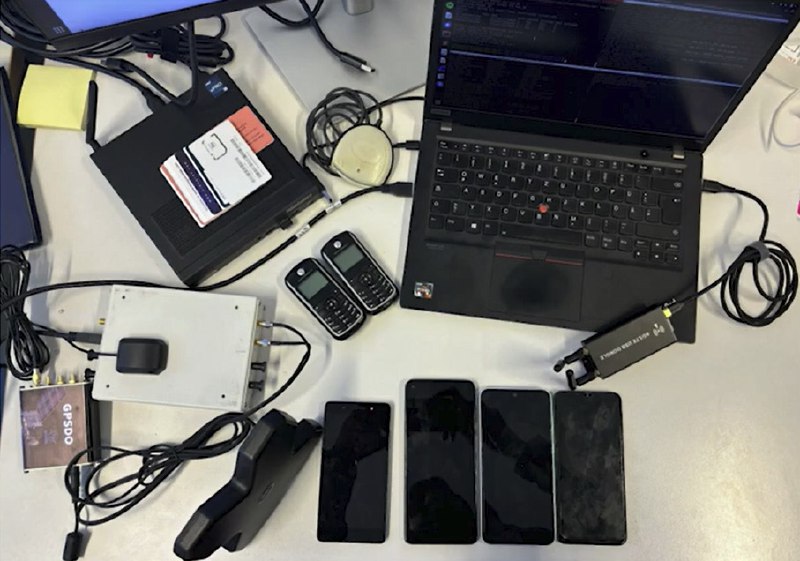
Phones auto-connecting to "FreeWiFi_Secure" Wi-Fi network leak full IMSI in cleartext during EAP-SIM exchange
Anyone nearby with sniffer could capture it → track users, or correlate identities.
Fixed pushed disabling FreeWiFi_Secure on legacy boxes starting Oct 1, 2025.
https://7h30th3r0n3.fr/the-vulnerability-that-killed-freewifi_secure/
  • 🔥 12
  • 🥱 4
  • ❤ 2
  • 🌚 2
Post #2684 6.54K
Post #2683 6.21K
Older posts →
Threads Profile ViewerView any public Threads profile without an account.Open ThreadLook →Writing with AI? Make it sound human.Metric37 rewrites AI drafts so they read naturally. Free AI detector, 1,500 words free.Try Metric37 →