TGViewer
Android Security & Malware Android Security & Malware @androidmalware · 44.9K subscribers
Post #2698 7.27K
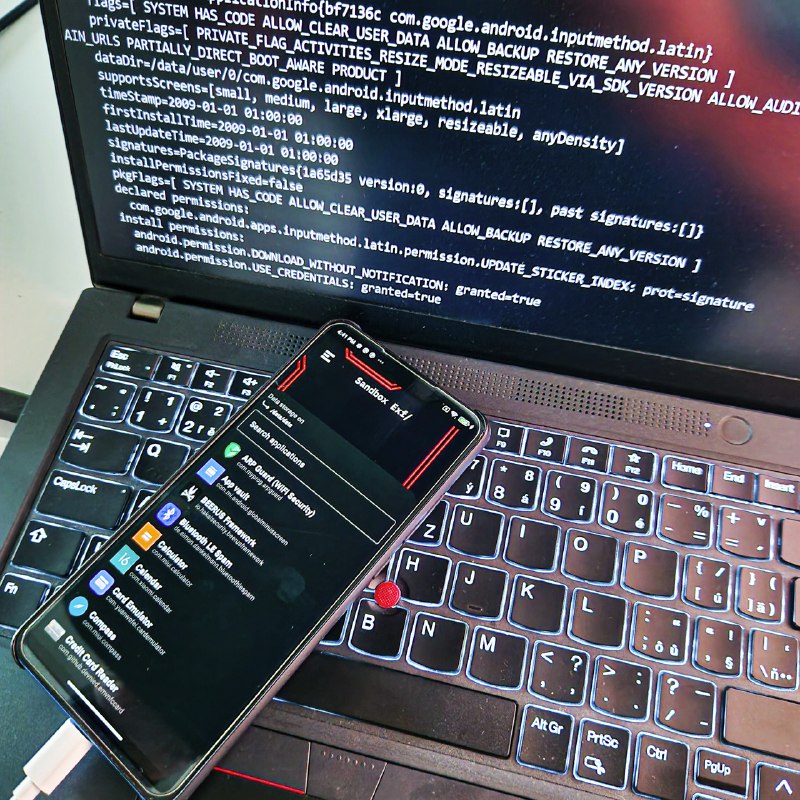
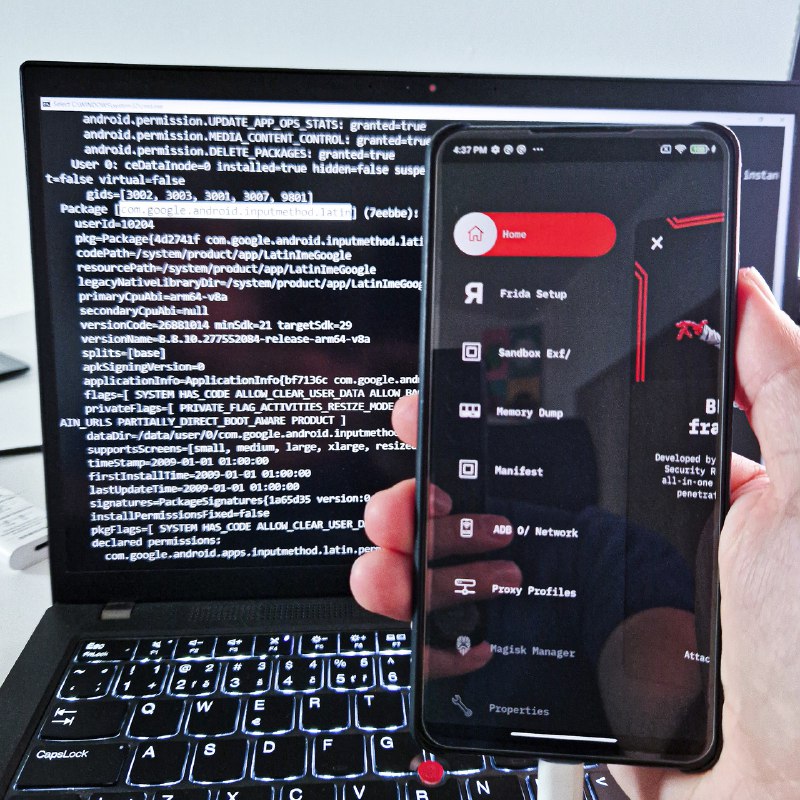
New Android BEERUS framework for dynamic analysis & reverse engineering
BEERUS brings Frida auto-injection, sandbox exfiltration, memory dumps, Magisk integration and more for on device app analysis.
https://github.com/hakaioffsec/beerus-android
  • 👍 22
  • 🔥 14
  • ❤ 4
  • 🤣 4
  • 👎 1
More from @androidmalware
  1. Sep 29, 2026CVE-2026-20687: AppleJPEGDriver startDecoder Timeout UAF — iOS/macOS kernel vulnerability…
  2. Sep 29, 2026How we found 24 Android vulnerabilities using our open source AI security agent https://gi…
  3. Sep 29, 2026From BlackCat to Panda Workshop: Inside the Evolving C2 Panel Behind RATHat https://www.cl…
  4. Sep 28, 2026apk-reverse: An Agent Skill for Android APK reverse engineering, debloating, ad removal, s…
  5. Sep 28, 2026A native APK and DEX decompiler written in Rust https://github.com/Ch0pin/rdx
  6. Sep 28, 2026RemControl: AI Built the Overlays. Victims Lose their PINs https://www.group-ib.com/blog/r…
Threads Profile ViewerView any public Threads profile without an account.Open ThreadLook →Writing with AI? Make it sound human.Metric37 rewrites AI drafts so they read naturally. Free AI detector, 1,500 words free.Try Metric37 →