TGViewer
Channel Public Channel
Whitehat Lab

Whitehat Lab

@wh_lab

Авторский канал об информационной безопасности
Свежие CVE, Red Team инструменты, внутренняя инфраструктура и другое
Edu only

Автор: @exited3n
Subscribers
3.18K
Photos
507
Videos
1
Links
566

Showing posts older than #766 · Back to latest

Older Posts 20 shown
Post #765 1.21K
🔄🐕 RustHound-CE 2.5.7

Cross-platform and cross-compiled BloodHound collector tool written in Rust, making it compatible with Linux, Windows, and macOS. It therefore generates all the JSON files that can be analyzed by BloodHound Community Edition


Работает с BloodHound-CE

Установка:

# Install from cargo
cargo install rusthound-ce


Сбор:

rusthound-ce -i 192.168.1.10 -d domain.local -u user@domain.local -p 'pass' -z


🖥 Repo

#rusthound #soft #bloodhound #rust

✈️ Telegram 💬 MAX
  • 🔥 4
Post #764 1.26K
💻 ADPathFinder 1.2.0

Инструмент для построения путей атак в домене через BloodHound CE, также покрывает AD CS, MSSQL, SCCM, трасты и т.д.

🔗 Research

ADPathFinder is an attack mapping tool for pentesters and red teamers. It analyses SharpHound data and unifies it with OpenGraph plugins to surface attack paths to high-value targets such as Domain Admins and Domain Controllers, starting from low-privileged users and computers


🐱 Repo
📚 Wiki

#windows #adpathfinder #soft

✈️ Telegram 💬 MAX
NetSPI ADPathFinder: OpenGraph Attack Path Mapping in BloodHound CE ADPathFinder unifies SharpHound data with OpenGraph collectors like MSSQLHound and ConfigManBearPig. Discover how this tool maps complex, cross-dataset privilege escalation paths across AD, ADCS, MSSQL, and SCCM, and brings vital graph context to your password…
  • 👍 5
  • ❤ 1
Post #763 1.19K
🐸 Frogscope

Full external application attack surface management and exposure management


🐱 Repo

#soft #python

✈️ Telegram 💬 MAX
Post #762 1.07K

Forwarded from APT

🔒 Certi-Bhai — IIS AppPool → NT AUTHORITY\SYSTEM via AD CS RPC

A webshell under IIS AppPool\DefaultAppPool can enroll against the ADCS RPC endpoint and come back with a certificate for the host machine account. Outbound domain traffic from a virtual AppPool identity is authenticated as HOST$, so the default Machine template treats the CSR as a legitimate computer enrollment.
The issued cert produces a PKINIT TGT for that machine account. S4U2Self turns it into an Administrator CIFS ticket on the same box, which is local SYSTEM-equivalent access and a path to hash dump. Potato-family impersonation is not part of the chain.

🔗 Research:
https://www.mannulinux.org/2026/08/Privilege-escalation-from-IIS-AppPool-to-NT-AuthoritySYSTEM-via-AD-CS-RPC-endpoint.html

🔗 Source:
https://github.com/incredibleindishell/Certi-Bhai

#ad #adcs #iis #privesc #pkinit #s4u2self #windows
  • 👍 4
  • 🔥 3
  • 😱 1
Post #761 1.23K
🔄💻 Delegations v1.1.0

Delegations is a tool that allows you to work with all types of Kerberos delegations (unconstrained, constrained, and resource-based constrained delegations) in Active Directory


UPD

Отличный инструмент пост эксплуатации для работы со всеми видами делегирования

💻 Repo

#windows #ad #delegations #redteam

✈️ Telegram 💬 MAX
  • ❤ 1
  • 👍 1
Post #759 1.52K
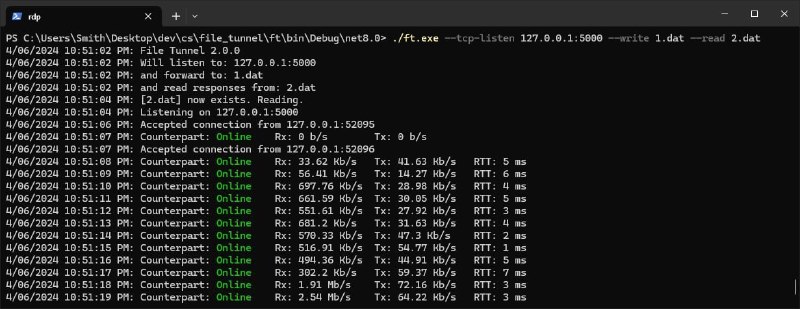
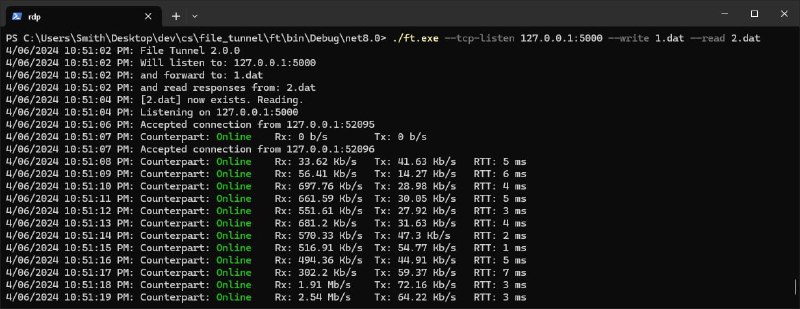
🔄💻 File Tunnel v3.5.3

TCP туннель через файл

Добавлена полная поддержка macOS

Новые FS в v3:

S3 Buckets
Dropbox
FTP
Citrix


Поддерживаемые FS:

Bypassing a firewal
l:

# Host A
ft.exe -L 5000:127.0.0.1:3389 --write "\\server\share\1.dat" --read "\\server\share\2.dat"

# Host B
ft.exe --read "\\server\share\1.dat" --write "\\server\share\2.dat"


Tunnel TCP through RDP:

# Host A
ft.exe -L 5000:192.168.1.50:8888 --write "C:\Temp\1.dat" --read "C:\Temp\2.dat"

# Host B
ft.exe --read "\\tsclient\c\Temp\1.dat" --write "\\tsclient\c\Temp\2.dat"


💻 Repo

#windows #filetunnel #soft

✈️ Telegram 💬 MAX
  • 👍 3
Post #756 2.04K
CVE-2026-63077 - критическая уязвимость в TeamCity

🔗 Research
🔗 Additional Guidance Following Reports of Active Exploitation

Неаутентифицированный пользователь с доступом к серверу может обойти проверки аутентификации и выполнить произвольные команды с привилегиями процесса TeamCity


🐱 PoC

#cve #poc #teamcity

✈️ Telegram 💬 MAX
  • 🔥 7
  • ❤ 2
Post #755 2K
⚙️ XSS2Shell - WordPress Pre-Auth XSS - RCE Chain

XSS в самой популярной cms в мире с оценкой по CVSS 8.9

🔗 Disclosure

XSS2Shell is a pre-authentication XSS to code-execution chain affecting WordPress Core (all versions back to 4.7, ~500M+ sites). A single crafted failed-login attempt runs attacker JavaScript in the WordPress origin; against a logged-in administrator it escalates to full RCE


Условия для full RCE:

🐥 A victim already logged in as a single-site Administrator
🐥 Explicit interaction (typically one click) with an attacker-controlled page
🐥 Specific WordPress features aligned (Application Passwords, plugin upload capability, etc.)


🐱 PoC
🐱 Nuclei шаблон

#cve #poc #wordpress #web #xss #rce

✈️ Telegram 💬 MAX
  • 👍 3
  • 🔥 2
Post #754 1.17K

Forwarded from 1N73LL1G3NC3

ResetNightmare

ResetNightmare (CVE-2026-27912) is a validation flaw in the Kerberos Change Password protocol that allows for resetting the password of any target user/computer account, without knowing the current one. The attack requires an unpatched domain controller, and the ability to write a userPrincipalName (UPN) on any account you control. Alternatively, the vulnerability can also be abused by an attacker having the ability to create new users/computers in any OU, as creating a user/computer allows you to get GenericWrite permissions over it.

Blog: Identity Crisis: Novel Vulnerabilities Leading to Kerberos Downgrade, DoS, and Full Domain Takeover
  • ❤ 7
  • 👍 1
Post #753 1.75K
🖥 Zapscape - CVE-2026-64561

Позволяет атакующему с правами root в гостевой виртуальной машине (KVM escape) выйти из нее и выполнить код с root правами на хостовой системе

🐱 Подробный разбор
🐱 PoC

#cve #poc #linux

✈️ Telegram 💬 MAX
  • 👍 7
  • ❤ 1
  • 🔥 1
  • 😱 1
Post #752 1.69K
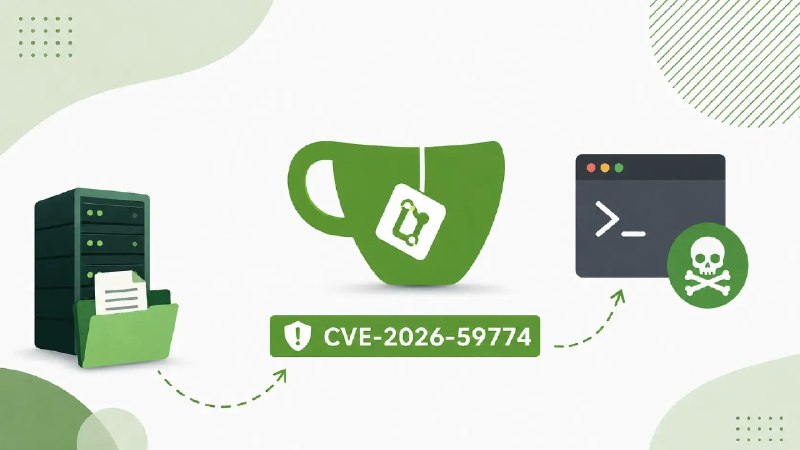
⚙️ CVE-2026-59774 - Unauthenticated Arbitrary File Read can lead to RCE in Gitea

Для успешной атаки достаточно, чтобы в Gitea существовал хотя бы один публично читаемый репозиторий с включённым модулем кода

Gitea registers POST /{username}/{reponame}/markup with optional sign-in,
repository assignment, and a repository-unit reader check. An anonymous user
passes that check for a public repository with a normal readable code unit.


Уязвимость в эндпоинте:

POST /{owner}/{repo}/markup


Затронутые версии с 1.22.1 по 1.27.0 включительно, патч в 1.27.1

🐱 Report

#cve #gitea #web

✈️ Telegram 💬 MAX
Post #751 1.44K

Forwarded from Blue (h/c)at Café

🎸 Вышел Prowl 1.3.0

Главное в обновлении:
🔵 поиск секретов в PDF, DOCX, XLSX, PPTX, архивах и почтовых экспортax
🔵 локальный OCR для изображений и сканированных PDF
🔵 сканирование логов и артефактов GitHub Actions и GitLab CI
🔵 новые детекторы и проверка ключей DeepSeek, DeepInfra, Fireworks и Perplexity
🔵 усиленная защита от небезопасных URL, редиректов и архивных бомб
🔵 175 правил, 84 верификатора и 80 E2E-сценариев

ТЫК
GitHub Release v1.3.0 · Lercas/prowl Documents, mail, and OCR Recursively scan ZIP/JAR, TAR/TAR.GZ/TGZ/GZIP, DOCX/XLSX/PPTX, EML/EMLX/MBOX, MIME attachments, and PDF text layers across filesystem, repository, and Git-history sources....
  • ❤ 8
  • 👍 3
  • 🔥 1
Post #750 2.16K
💻 AD CS Template Hardening: ESC1–ESC16 Defense Playbook

Большой гайд по защите AD CS

🔗 Defense Playbook

#ad #adcs #windows

✈️ Telegram 💬 MAX
  • 🔥 10
  • 🤔 1
Post #749 2.41K
💻 OctoC2

C2 через API github по HTTPS протоколу

GitHub-native C2 for authorized security research, with encrypted multi-channel transport and resilient failover


🐱 Repo

#redteam #octoc2 #c2

✈️ Telegram 💬 MAX
  • 👍 4
Post #748 3.15K
🌟 wp2shell (CVE-2026-63030 / CVE-2026-60137)

Online чекер - https://wp2shell.com

WordPress REST API Batch endpoint (/wp-json/batch/v1) SQL Injection 
Unauthenticated RCE


Nuclei шаблон
:

id: wp2shell-batch-exposure

info:
name: WordPress wp2shell Exposure (CVE-2026-63030, CVE-2026-60137)
author: zephrsec
severity: critical
reference:
- https://slcyber.io/research-center/wp2shell-pre-authentication-rce-in-wordpress-core/
classification:
cve-id: CVE-2026-63030,CVE-2026-60137
tags: wordpress,cve2026,rce,sqli,wp2shell

http:
- raw:
- |
GET / HTTP/1.1
Host: {{Hostname}}
- |
POST /?rest_route=/batch/v1 HTTP/1.1
Host: {{Hostname}}
Content-Type: application/json

{}

req-condition: true
redirects: true

extractors:
- type: regex
name: wp_version
part: body_1
group: 1
regex:
- 'name="generator" content="WordPress ([0-9.]+)"'

matchers-condition: and
matchers:
- type: dsl
dsl:
- >-
compare_versions(wp_version, ">=6.9.0", "<6.9.5") ||
compare_versions(wp_version, ">=7.0.0", "<7.0.2") ||
compare_versions(wp_version, ">=6.8.0", "<6.8.6")
- type: word
part: body_2
words:
- '"rest_missing_callback_param"'
- '"rest_invalid_param"'
condition: or


🔗 Research
🐱 PoC

#cve #web #pentest #wordpress #poc

✈️ Telegram 💬 MAX
  • ❤ 4
  • 👍 2
Post #747 1.38K

Forwarded from Дневник Комбеза

Semgrep Rules

Последнее время мы с командой всё чаще задумывались о том, что mobsfscan в части своего Semgrep-компонента, мягко говоря, местами глючный и довольно ограниченый.

А если попробовать найти достаточно полный набор Semgrep-правил для мобильных приложений, быстро выясняется, что хорошие правила разбросаны по всему необъятному интернету🔞

Поэтому мы решили собрать всё это в одном месте и создали репозиторий:

https://github.com/Sib-Coder/semgrep-mobile-rules

В нём постарались собрать максимально полный набор проверок для мобильных приложений и при этом избавиться от дубликатов.

Будем очень рады вашей поддержке, новым правилам и идеям для развития репозитория.

Давайте делать мобилки безопаснее вместе 😎
GitHub GitHub - Sib-Coder/semgrep-mobile-rules: Правила семгреп для проверки безопасности мобильных приложений Правила семгреп для проверки безопасности мобильных приложений - Sib-Coder/semgrep-mobile-rules
  • 🔥 5
Post #746 2.84K
🔄💻 Keycred v1.2.2

CLI tool and library that implements the KeyCredentialLink structures according to section 2.2.20 of the Active Directory Technical Specification (MS-ADTS)


UPD:

Added SOCKS5 support for auth/burn
Added badge for KCLs that are not validated write compatible to indicate that computer accounts cannot restore these after clearing them


🐱 Repo

#windows #ad #redteam #soft

✈️ Telegram 💬 MAX
Post #744 2.01K
🔄💻 File Tunnel v3.2.0

TCP туннель через файл

Новые FS в v3:

S3 Buckets
Dropbox
FTP
Citrix


Поддерживаемые FS:

Bypassing a firewal
l:

# Host A
ft.exe -L 5000:127.0.0.1:3389 --write "\\server\share\1.dat" --read "\\server\share\2.dat"

# Host B
ft.exe --read "\\server\share\1.dat" --write "\\server\share\2.dat"


Tunnel TCP through RDP:

# Host A
ft.exe -L 5000:192.168.1.50:8888 --write "C:\Temp\1.dat" --read "C:\Temp\2.dat"

# Host B
ft.exe --read "\\tsclient\c\Temp\1.dat" --write "\\tsclient\c\Temp\2.dat"


💻 Repo

#windows #filetunnel #soft

✈️ Telegram 💬 MAX
  • 👍 5
  • ❤ 1
Older posts →
Threads Profile ViewerView any public Threads profile without an account.Open ThreadLook →Writing with AI? Make it sound human.Metric37 rewrites AI drafts so they read naturally. Free AI detector, 1,500 words free.Try Metric37 →