
Blue Team Toolkit: What Every Defender Should Have in Their Arsenal
In today’s threat landscape, detection and response are everything. I recently reviewed a solid Blue Team Toolkit that brings together the essential tools every SOC analyst and defender should know.
Here’s a snapshot of what a strong blue team stack looks like 👇
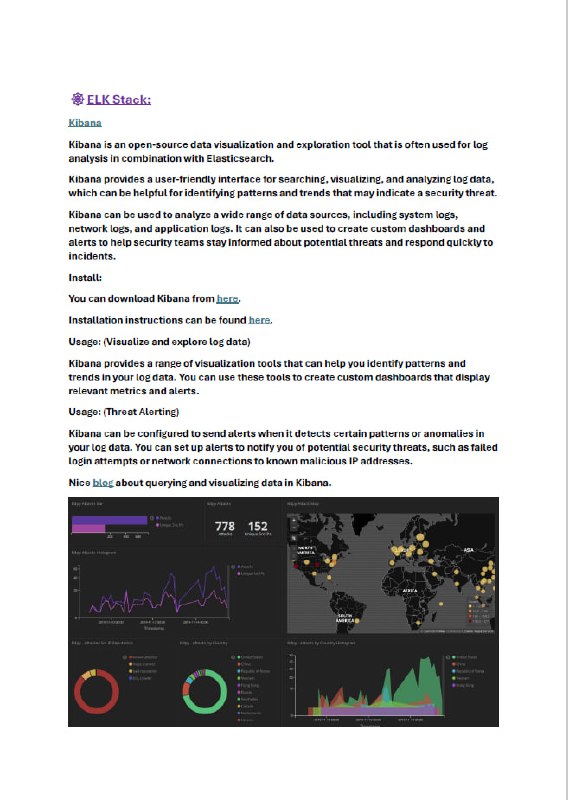
🔍 Monitoring & SIEM – Splunk, ELK Stack, Microsoft Sentinel
➡️ Centralised logging, correlation, and alerting
🧪 Threat Hunting & Detection – Sysmon, Sigma rules, Velociraptor
➡️ Deep visibility into endpoint activity
🖥 Endpoint Security (EDR/XDR) – CrowdStrike, Defender for Endpoint
➡️ Real-time detection and response
🌐 Network Analysis – Wireshark, Zeek, Suricata
➡️ Traffic inspection & anomaly detection
🧰 Forensics & Incident Response – Autopsy, FTK, Volatility
➡️ Investigating breaches and memory analysis
☁️ Cloud Security – AWS CloudTrail, Azure Defender
➡️ Monitoring cloud-native environments
SEE ALSO:
📌 nmap Fee Lab Online
#definsive
Post #8146
2.05K

- 👍 6
- ❤ 1