SOC Incident Response Playbook — 100+ Pages of Real-World Runbooks
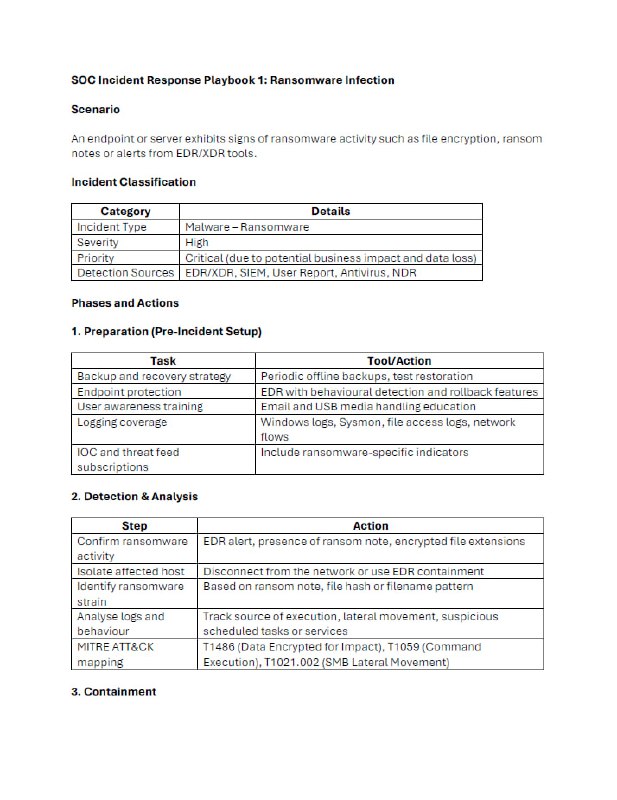
This SOC Incident Response Playbook is a multi-scenario compendium that gives you ready-to-run workflows for incidents like:
💣 Ransomware infections (EDR/XDR, backups, containment paths)
🧑💻 Insider data exfiltration (DLP, CASB, proxy & email controls)
☁️ Cloud account compromise (M365/Azure/AWS/GWS identity abuse)
🌐 Web app exploitation (WAF, logs, SAST/DAST, secure coding feedback loop)
🔗 Supply chain compromise (trojanised updates, vendor risk & third-party access)
💾 USB-delivered malware
🌊 DDoS against public-facing services
📧 Business Email Compromise (BEC)
🔐 Unauthorised privilege escalation & DB access
🛰 DNS tunnelling, cloud misconfig exposure, RDP brute force, dev environment abuse & more
Each playbook is structured with: Preparation → Detection & Analysis → Containment → Eradication → Recovery → Lessons Learned & Success Metrics, plus typical tools (SIEM, EDR/XDR, CSPM, DLP, CASB, WAF, etc.) so you can plug it directly into your SOC procedures or SOAR.
#defensive
Post #7972
3.68K

- ❤ 10