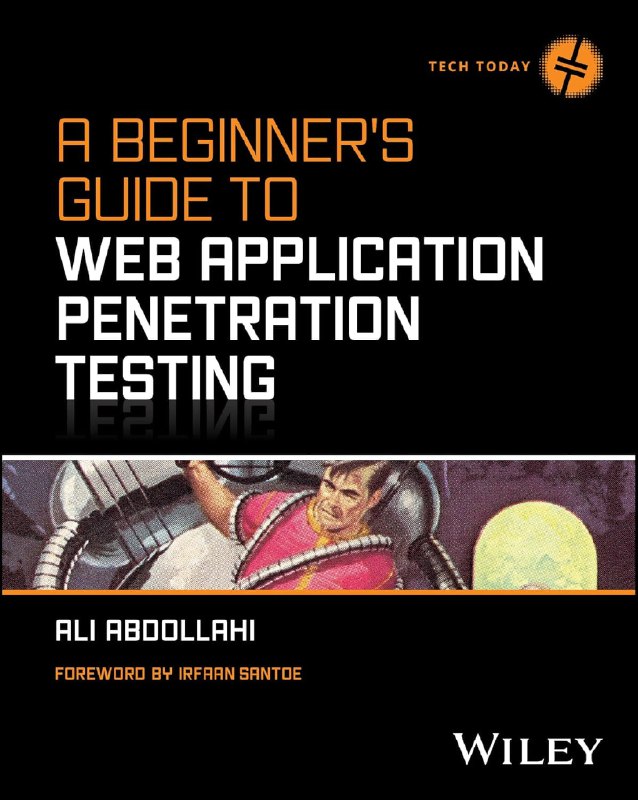
A Beginner's Guide To Web Application Penetration Testing, Ali Abdollahi, 2025
You'll learn about common vulnerabilities and how to perform a variety of effective attacks on web applications. Consistent with the approach publicized by the Open Web Application Security Project (OWASP), the book explains how to find, exploit and combat the ten most common security vulnerability categories, including broken access controls, cryptographic failures, code injection, security misconfigurations, and more.
You will also learn to identify and exploit vulnerabilities using automated tools and manual testing methodologies. The book provides hands-on guidance on using leading web application security tools, such as Burp Suite, OWASP ZAP, and Nmap. It covers how to conduct common attacks such as SQL injection, cross-site scripting (XSS), and cross-site request forgery (CSRF), required for a practical understanding of web application vulnerabilities.
Beyond just identifying vulnerabilities, the book guides on analyzing testing results to improve the security measures of web applications systematically. It explores web application security frameworks and standards, helping you to align your security practices with industry-recognized guidelines. The book focuses on practical exercises and real-world examples, making it an essential tool for anyone looking to understand or improve the security of web applications. This hands-on approach ensures that you can translate theoretical knowledge into actionable skills.
❗️GitHub
⚠️OVA download
⛳️YouTube
#book #web
Post #6717
2.08K

- 👍 6
- 🤝 2