TGViewer
Channel Public Channel
Sys-Admin InfoSec

Sys-Admin InfoSec

@sysadm_in_channel

News of cybersecurity / information security, information technology, data leaks / breaches, cve, hacks, tools, trainings
* Multilingual (En, Ru).
* Chat - @sysadm_in
* Job - @sysadm_in_job
* DNS - OpenBLD.net
* ? - @sysadminkz
Subscribers
12.9K
Photos
250
Videos
2
Links
4.6K

Showing posts older than #5479 · Back to latest

Older Posts 20 shown
Post #5476 4.07K
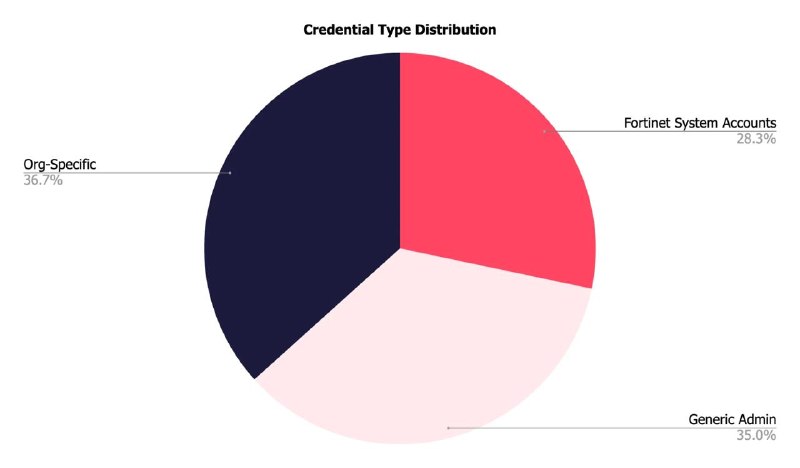
FortiBleed - Breach How 80,000+ Corporate= Firewalls Were Quietly Compromised

If your organization uses a Fortinet firewall or VPN product and appears in this dataset, treat your network perimeter as already compromised and act immediately. SOCRadar rates this campaign Critical..:

https://socradar.io/blog/fortibleed-fortinet-firewalls-compromised/
Post #5475 3.26K
Post #5472 3.57K
Post #5471 3.15K

Forwarded from OpenBLD.net (Yevgeniy Goncharov)

⚡ DNS is not just about domains. It is about Trust.

Recent supply chain incidents are a strong reminder that modern attacks often start through tools and workflows developers already trust:

• npm packages and dependency updates
• compromised maintainer accounts
• VSCode extensions
• GitHub Actions workflows
• fake installers and update mechanisms

Several recent cases highlight this trend:

• Axios compromised on npm - malicious versions dropped a Remote Access Trojan >
• Compromised VSCode Nx Console >
• OpenAI TanStack npm supply chain attack >
• OpenAI Axios developer tool compromise >
• GitHub unauthorized access to internal repositories >

The key takeaway: supply chain attacks are becoming more relevant to every developer, engineering team, and company.

DNS security should not be treated as an optional layer.

It can provide visibility and control when malicious code attempts to:

• connect to C2 infrastructure
• reach phishing domains
• communicate with fake update servers
• exfiltrate data through suspicious endpoints

If malicious code has already entered the environment, visibility becomes critical...

At this point, the key questions are simple:

• Can you see where it is trying to connect?
• Can you understand whether that connection is expected?
• Can you react before the incident becomes bigger?

OpenBLD.net - Security starts earlier than incident response.

Watch yourself, your emails, your extensions, and your DNS. Peace ✌️
Post #5470 2.36K
Post #5468 2.62K
AppSecFest 2026 - В эту пятницу в Алматы, Farabi Hub

Будут экспертные эксперты, тимлиды, специалисты, представители IT-индустрии, AppSec/DevSecOps-практики, инженеры по безопасности.

+ будет открытое CTF-соревнование от команды mimicats – где можно пропробовать свои скиллы в реальных задачах по ИБ (максимум практики, никакой теории)
+ Воркшопы с живое общением на темы AppSec, DevSecOps, инженерной культуры, процессы, и даже факапы

• Начало: 15 мая, 09:00, Farabi Hub

Все спикеры заслуживают внимания, многих знаю лично, все детали здесь: appsecfest.kz
Post #5467 2.33K

Forwarded from Sys-Admin Up (Yevgeniy Goncharov)

New TrickMo Variant: Device Take Over malware targeting Banking, Fintech, Wallet & Auth apps

..The malware’s primary command-and-control channel has been migrated onto The Open Network (TON) using .adnl endpoints routed through an embedded local TON proxy..:

https://www.threatfabric.com/blogs/new-trickmo-variant-device-take-over-malware-targeting-banking-fintech-wallet-auth-app
ThreatFabric New TrickMo Variant: Device Take Over malware targeting Banking, Fintech, Wallet & Auth apps Perseus is a new Device Takeover (DTO) malware family that specifically looks for user-generated content stored in note taking applications.
Post #5464 2.57K
TCLBANKER: Brazilian Banking Trojan Spreading via WhatsApp and Outlook

Trojan that contains a dynamic infection chain with a heavy anti-analysis loading component that can deploy two embedded payloads (worm, banker). The observed infection chain bundles a malicious MSI installer inside a ZIP file. These MSI installer packages are abusing a signed Logitech program called Logi AI Prompt Builder..:

https://www.elastic.co/security-labs/tclbanker-brazilian-banking-trojan
Post #5463 2.4K
Post #5462 2.53K
Post #5460 2.61K
Older posts →
Threads Profile ViewerView any public Threads profile without an account.Open ThreadLook →Writing with AI? Make it sound human.Metric37 rewrites AI drafts so they read naturally. Free AI detector, 1,500 words free.Try Metric37 →