TGViewer
Channel Public Channel
road to OSCP

road to OSCP

@road_to_oscp

🇺🇦 тестуємо 🇺🇦
Subscribers
1.87K
Photos
89
Videos
1
Links
146
Recent Posts 20 shown
Post #356 2.84K

Forwarded from Gravity's Rainbow

#network #nmap #nse

[ Nmap Scripting Engine (NSE) - useful scripts collection ]

The Nmap Scripting Engine (NSE) is one of Nmap's most powerful and flexible features. It allows users to write (and share) simple scripts (using the Lua programming language ) to automate a wide variety of networking tasks.

We collected some of useful (and mostly unknown or not popular) scripts in one post (that will be regularly updated).

- nfs-ls -> get useful information about files from NFS exports
- ipidseq -> finding zombie hosts that can later be passed in to -sI
- broadcast-listener -> sniffs the network for incoming broadcast communication and attempts to decode the received packets
- grab_beacon_config -> simple PoC script to scan and acquire CobaltStrike Beacon configurations
- http-security-headers -> checks for the HTTP response headers related to security given in OWASP Secure Headers Project
- http-ntlm-info -> enumerates information from remote HTTP services with NTLM authentication enabled
- winrm -> WinRM service detection
- http-enum -> enumerates directories used by popular web applications and servers

Subscribe to see more: t.me/gravity_rainbow
  • 👍 5
Post #355 2.7K
#mobile #frida

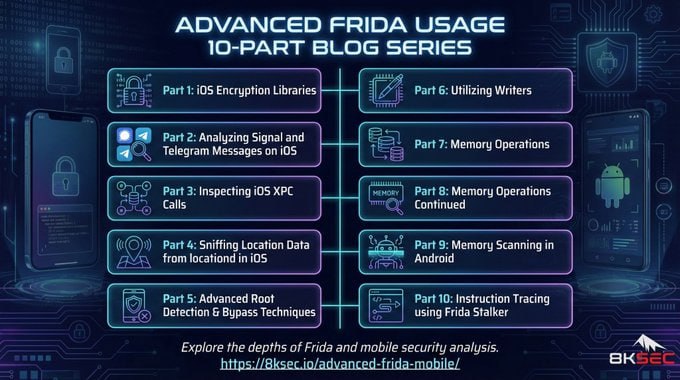
[ Advanced Frida Series ]

📱 Ready to level up your Mobile Reversing & Dynamic Instrumentation game? Most Frida tutorials cover the basics. 8ksec.io built this Frida series for advanced instrumentation against complex iOS and Android targets.

🔎 Topics include:
🔹 Hooking Objective-C and Swift methods
🔹 Extracting secrets from encrypted iOS databases
🔹 Tracing Signal and Telegram message handling
🔹 Analyzing Android root checks across Java, native, and syscalls
🔹 Patching ARM64 instructions at runtime
🔹 Instruction-level tracing with Frida Stalker

🔗 Start the Advanced Series here: https://8ksec.io/advanced-frida-mobile
  • ❤ 6
  • 👍 2
Post #354 2.99K
#responder #internal

[ Responder 3.2.0.0 ]

Responder 3.2.0.0 is out!
All new year updates +
- IMAP and SMTP StartTLS
- IMAPS TLS server on port 993
- DHCPv6 poisoning (pure python) using _dirkjan
mitm6 attacks
- Kerberos, DNS server updates
- Etc.

https://github.com/lgandx/Responder
  • ❤ 3
Post #352 2.47K
#proxmox

[ Living off the Hypervisor - LOLPROX ]

Curated catalog of native Proxmox VE binaries and techniques that adversaries can abuse for post-exploitation operations.

Proxmox is at its core just a Debian image with some hypervisor tooling but the hyper visor tooling is what makes it unique from an attacker perspective.

https://lolprox.yxz.red

Blogpost: https://blog.zsec.uk/lolprox

LOLPROX - Through a Defender's Eyes

https://blog.zsec.uk/lolprox-defend
  • ❤ 5
Post #349 3.55K
[ Living Off the Land: Windows Post-Exploitation Without Tools ]

Blog about post-exploitation using only built-in, signed Microsoft tools (PowerShell, WMI, certutil, bitsadmin, and more), without uploading any custom binaries or dropping suspicious artifacts.

https://xbz0n.sh/blog/living-off-the-land-windows

(note from admin: don't forget that PS/WMIC and other things that are described in this article will also be detected)
  • ❤ 10
Post #348 1.81K
[ Cobalt Strike 4.12: Fix Up, Look Sharp! ]

Cobalt Strike 4.12 is LIVE, complete with a new look for the GUI! Additionally:
- A REST API
- User Defined Command and Control (UDC2)
- New process injection options
- New UAC bypasses
- and more!
Check out the release blog for details.


https://www.cobaltstrike.com/blog/cobalt-strike-412-fix-up-look-sharp
  • ❤ 8
Post #346 1.86K
#ssh #windows

[ Windows' Built-in OpenSSH for Offensive Security ]

Windows includes OpenSSH by default - ssh.exe. This means all those wonderful tricks we used as washed-up *nix sysadmins, we can now revisit as Offensive Security Consultants! This article shows how Windows’ OpenSSH can be used as a network proxy implant, deployed as a “remote-access trojan” for lower privileged users, and as a data exfiltration tool.

https://pulsesecurity.co.nz/articles/windows-ssh-is-awesome
  • 🔥 7
  • 👍 3
  • ❤ 2
  • 😁 1
Post #345 1.61K
#exec #lateral

[ GoExec - Remote Execution Multitool ]

GoExec is a new take on some of the methods used to gain remote execution on Windows devices. GoExec implements a number of largely unrealized execution methods and provides significant OPSEC improvements overall.

https://github.com/FalconOpsLLC/goexec

P.S. From here on, this channel is now live again. Expect more posts soon.
  • ❤ 8
  • 🔥 6
Post #344 2.59K
GODAP

A complete TUI for LDAP

Features:

• Supports authentication with password, NTLM hash, Kerberos ticket or PEM/PKCS#12 certificate
• Formats date/time, boolean and other categorical attributes into readable text
• Pretty colors & cool emojis
• LDAPS & StartTLS support
• Fast explorer that loads objects on demand
• Recursive object search bundled with useful saved searches
• Flexible group members & user groups lookups
• Supports creation, editing and removal of objects and attributes
• Supports moving and renaming objects
• Supports searching deleted & recycled objects
• Supports exporting specific subtrees of the directory into JSON files
• Interactive userAccountControl editor
• Interactive DACL viewer + editor
• Interactive ADIDNS viewer + editor (basic)
• GPO Viewer
• SOCKS support

https://github.com/Macmod/godap

Thanks to: @hybgl
  • ❤ 6
  • 👍 5
Post #340 2.98K
LLC (Linux Log Cleaner)

A convenient tool for modifying or deleting information in Linux log files, includes:
- /var/log/lastlog: Contains the last login of each user. Command to view: lastlog
- /var/run/utmp: Contains information about currently active login sessions. Command to view: who, w
- /var/log/wtmp: Stores the history of logins and logouts. Command to view: last
- /var/log/btmp: Records failed login attempts. Command to view: lastb


https://github.com/Macr0phag3/LLC
  • 👍 5
  • ❤ 1
Post #337 3.72K
A platform that provides intentionally vulnerable applications for learning source code review. Currently, 25 challenges are available.

It looks very interesting and promising

https://vulnerable.codes/

Thanks to: "Руслан 😎😎😎😎😎"
  • 🔥 13
  • ❤ 3
  • 👍 1
Post #336 3.28K
ScriptSentry is a powerful tool for automating the detection of unsafe configurations in logon scripts. It can identify issues such as:

- Unsafe UNC Folder Permissions
- Unsafe UNC File Permissions
- Unsafe Logon Script Permissions
- Unsafe GPO Logon Script Permissions
- Unsafe NETLOGON/SYSVOL Permissions
- Plaintext Credentials


This tool is described in detail in the blog post Hidde Menace: How to Identify Misconfigured and Dangerous Logon Scriptsn

https://github.com/techspence/ScriptSentry
  • 🔥 4
  • ❤ 3
  • 👍 3
Post #334 3.21K
З новим роком, далі - більше!

Happy New Year! The best is yet to come!
  • 🔥 15
  • ❤ 8
  • 👍 4
Older posts →

About this channel

How can I read @road_to_oscp without a Telegram account?
TGViewer shows the public web preview Telegram publishes for road to OSCP: recent posts, photos, videos and the subscriber count, with no app, login or account.
How many subscribers does road to OSCP have?
road to OSCP (@road_to_oscp) has 1.87K subscribers on Telegram, refreshed roughly every 30 minutes.
Does road to OSCP know I viewed it here?
No. Public channel previews carry no viewer identity, and TGViewer has no accounts or tracking of what you look up.
Threads Profile ViewerView any public Threads profile without an account.Open ThreadLook →Writing with AI? Make it sound human.Metric37 rewrites AI drafts so they read naturally. Free AI detector, 1,500 words free.Try Metric37 →