TGViewer
Channel Public Channel
Reverse Dungeon

Reverse Dungeon

@reverse_dungeon

Reverser's notes
The Mentor
1989
Subscribers
5.01K
Photos
744
Videos
59
Links
2.3K

Showing posts older than #4075 · Back to latest

Older Posts 20 shown
Post #4072 2.28K
Залил в библиотеку обнаруженные сегодня выпуски журнала "Микропроцессорные средства и системы"

図書館.きく.コム
  • ❤‍🔥 8
Post #4070 1.81K

Forwarded from Cybred

Выложили доклады с конференции DEF CON 33. Она прошла в Лас-Вегасе и оказалась одной из самых крупных DEF CON за всю историю — конференцию посетили около 26 000 человек, а на YouTube уже опубликовано более 350(!) видео.

Среди них много докладов на самые разные темы — от классического веба и hardware-хакинга (и куда же без AI) до совсем неожиданных направлений: гайда по отмыванию средств с помощью криптовалюты, современного подхода к кардингу и взлома физических замков в отелях.

Один из участников, даже не смотря на угрозы судом, рассказал, как ему удалось разреверсить современные морские двигатели, найти способ удаленно менять их мощность, и перехватывать управление.

Собрал пару интересных тем, чтобы ты мог оценить для себя:
1. Exploiting Security Side Channels in E2E Encrypted Msngrs
2. Mapping the Shadow War From Estonia to Ukraine
3. Infecting the Boot to Own the Kernel
4. New Red Team Networking Techniques for Initial Access and Evasion
5. Breakin 'Em All – Overcoming Pokemon Go's Anti Cheat Mechanism
6. BitUnlocker: Leverage Windows Recovery to Extract BitLocker Secrets
7. Turning Microsoft's Login Page into our Phishing Infrastructure
8. Tactical Flipper Zero You Have 1 Hour and No Other Equipment
9. How malicious packages on npm bypass existing security tools
10. TSPU: Russia's Firewall and Defending Against Digital Repression

Полный плейлист со всеми докладами тут.
YouTube DEF CON 33 - Reverse Engineering Marine Engines: Make powerboats do your bidding - Alex Lorman As the autonomous boat market has grown from nascent to ~$17 billion dollars, much of the infrastructure has gotten more and more accessible. Small flight controllers/autopilots are now only a click and configuration away. Servos, speed controllers and actuators…
  • ❤ 5
  • ❤‍🔥 3
Post #4069 1.39K

Forwarded from Sec Note

Sec Controls: The Art of Breaking Through

The definitive red team guide to understanding and bypassing Windows security controls: Windows Defender (static + AMSI + behavioral), AppLocker, WDAC, SmartScreen, ASR Rules, Credential Guard (VBS/LSAIso), Sysmon, PPL, and a comprehensive EDR deep-dive covering kernel callbacks, ETW-TI, API hooks, BYOVD, EDRKillShifter, EDRSilencer, sleep obfuscation, call stack spoofing, process injection, and the complete EDR kill chain. Every bypass mapped to MITRE ATT&CK.

#malware #evasion
  • ❤ 9
  • 🐳 1
Post #4065 2.07K

Forwarded from MEPhI CTF (Pavel Blinnikov)

Прямо сейчас проходит недельный Crackmes.one Reverse Engineering CTF 2026

Ивент начался 14 февраля в 03:00 по МСК и продлится до 21 февраля 03:00. Все таски только на реверс.

https://crackmesone.ctfd.io
  • 🐳 2
  • ❤ 1
  • ❤‍🔥 1
Post #4061 1.96K

Forwarded from MEPhI CTF (Pavel Blinnikov)

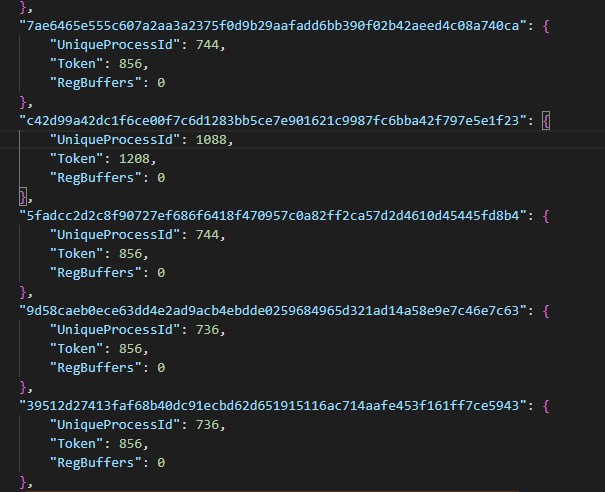
Письмо в редмондскую компанию Microsoft:

"Я 11 лет считаю оффсеты до поля UniqueProcessId у вас в EPROCESS — он то 744, то 736, иногда 1088, а вчера вообще 464 был. Вы что там, сумасшедшие что ли все???"

by @thsage
  • 🐳 13
  • ❤‍🔥 8
Post #4057 1.5K

Forwarded from HyperDbg News & Updates

Slides and recordings for our @FOSDEM talks are up! Join [Björn Ruytenberg] and [Sina Karvandi] for an in-depth introduction into @HyperDbg 's features and internals, or find out what's the latest in anti-anti-debugging techniques and HV transparency for malware reversing:

- https://fosdem.org/2026/schedule/event/APB9WC-mbec_slat_and_hyperdbg_hypervisor-based_kernel-_and_user-mode_debugging/

- https://fosdem.org/2026/schedule/event/CDPRDX-invisible_hypervisors_debugging_with_hyperdbg/
  • ❤ 5
Post #4054 1.58K

Forwarded from Linux Kernel Security (Andrey Konovalov)

A 0-click exploit chain for the Pixel 9 Part 2: Cracking the Sandbox with a Big Wave

Article by Seth Jenkins about exploiting a use-after-free in the driver for BigWave — an AV1 decoding hardware component present on Pixel SOCs.

Seth used the bug to escalate privileges from the mediacodec SELinux context and obtain root on Pixel 9.

This exploit is a part of an RCE chain developed by Seth and Natalie Silvanovich.
  • ❤ 1
Older posts →
Threads Profile ViewerView any public Threads profile without an account.Open ThreadLook →Writing with AI? Make it sound human.Metric37 rewrites AI drafts so they read naturally. Free AI detector, 1,500 words free.Try Metric37 →